
CrystalX MaaS Combines RAT, Stealer and Prankware Features
Summary
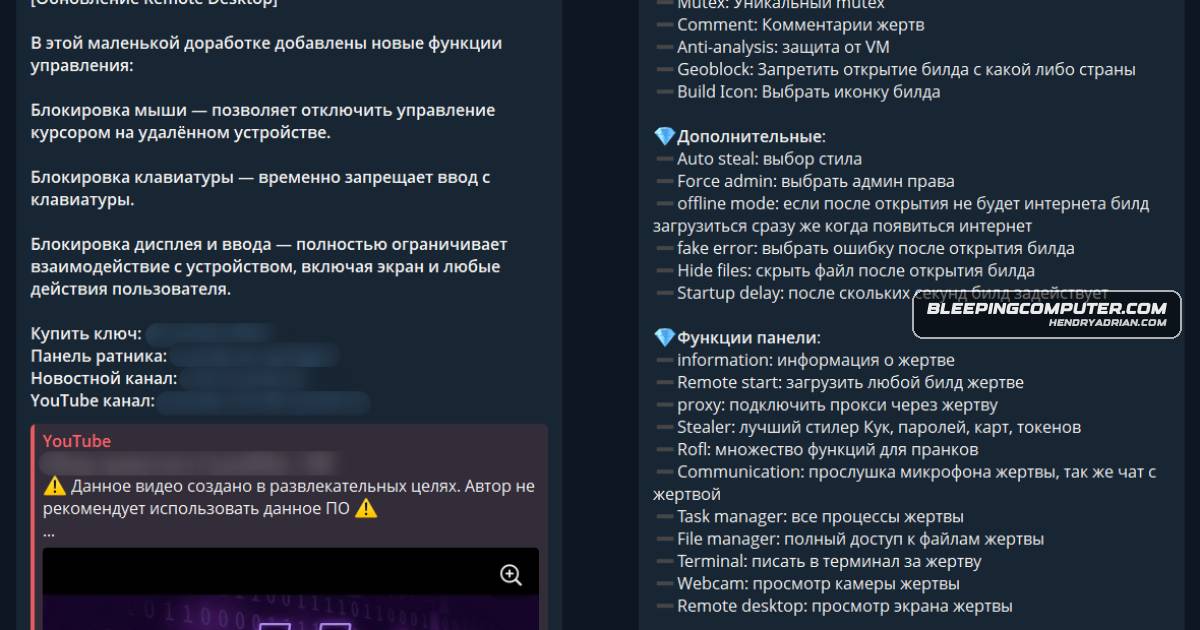
Kaspersky says CrystalX is a Telegram- and YouTube-promoted MaaS with remote access, keylogging, clipboard theft and prankware features. Its infostealer targets browsers and apps, but was temporarily disabled pending an upgrade.
Key points
- CrystalX emerged in January with a tiered subscription model and was promoted on Telegram and YouTube.
- Kaspersky reports strong similarities to WebRAT (Salat Stealer), including panel design, Go-based code and a bot-based sales system.
- Its builder supports customization, geoblocking and anti-analysis features; payloads are zlib-compressed and ChaCha20-encrypted.
- CrystalX uses WebSocket C2 and offers remote command execution, file transfer, file-system browsing and built-in VNC control.
- The infostealer targets Chromium-based browsers, Yandex, Opera, Steam, Discord and Telegram; Kaspersky found it temporarily disabled while being prepared for an upgrade.
- Other capabilities include real-time keylogging, audio/video capture and clipboard replacement of detected wallet addresses.
- Prankware can disrupt or distract victims through actions such as changing wallpaper, disabling input devices and showing fake notifications; users are advised to avoid untrusted downloads.
Article Details
- Event Type
- A newly promoted malware-as-a-service offering, identified in the article as CrystalRAT and CrystalX.
- Impact
- The malware is described as capable of remote control, file transfer, keylogging, clipboard hijacking, and collecting browser and app data, as well as capturing audio and video. Its prankware features can disrupt or distract users while data theft runs. The article does not report confirmed infections or victim impact.
MITRE ATT&CK
T1021.005 · VNCThe malware provides real-time remote control through built-in VNC.T1056.001 · KeyloggingThe malware includes a keylogger that streams keystrokes to its command-and-control server.T1059.003 · Windows Command ShellThe remote access module can execute commands via CMD.T1105 · Ingress Tool TransferThe remote access module supports uploading and downloading files.T1115 · Clipboard DataThe malware monitors the clipboard for wallet addresses and replaces them with addresses supplied by the attacker.T1123 · Audio CaptureThe malware can capture audio from the microphone.T1125 · Video CaptureThe malware can capture video.T1497.001 · System ChecksThe builder supports VM detection as an anti-analysis feature.T1622 · Debugger EvasionThe builder supports anti-debugging features.
Malware
CrystalRATA new malware-as-a-service called CrystalRAT is being promoted on Telegram, offering remote access, data theft, keylogging, and clipboard hijacking capabilities.CrystalXCrystalX is a new malware-as-a-service promoted on Telegram and YouTube that offers remote access, data theft, keylogging, clipboard hijacking, and a variety of prankware features.Salat StealerKaspersky links CrystalX to WebRAT (Salat Stealer) and describes a Go-based builder, user-friendly control panel, zlib-compressed ChaCha20-encrypted payloads, WebSocket C2, browser and app infostealers, remote VNCWebRATKaspersky links CrystalX to WebRAT (Salat Stealer) and describes a Go-based builder, user-friendly control panel, zlib-compressed ChaCha20-encrypted payloads, WebSocket C2, browser and app infostealers, remote VNC
Products
DiscordModules include an infostealer targeting Chromium-based browsers and apps like Steam, Discord, and Telegram, plus remote access, VNC control, audio/video capture, real-time keylogging, and a clipboard clipper.OperaCrystalX’s infostealer component, which Kaspersky found to be temporarily disabled as it is being prepared for an upgrade, targets Chromium-based browsers via the ChromeElevator tool, Yandex, and Opera.SteamModules include an infostealer targeting Chromium-based browsers and apps like Steam, Discord, and Telegram, plus remote access, VNC control, audio/video capture, real-time keylogging, and a clipboard clipper.TelegramCrystalX is a new malware-as-a-service promoted on Telegram and YouTube that offers remote access, data theft, keylogging, clipboard hijacking, and a variety of prankware features.YandexCrystalX’s infostealer component, which Kaspersky found to be temporarily disabled as it is being prepared for an upgrade, targets Chromium-based browsers via the ChromeElevator tool, Yandex, and Opera.YouTubeCrystalX is a new malware-as-a-service promoted on Telegram and YouTube that offers remote access, data theft, keylogging, clipboard hijacking, and a variety of prankware features.