
Trend Micro Reports Pawn Storm PRISMEX Campaign Targeting NATO Logistics
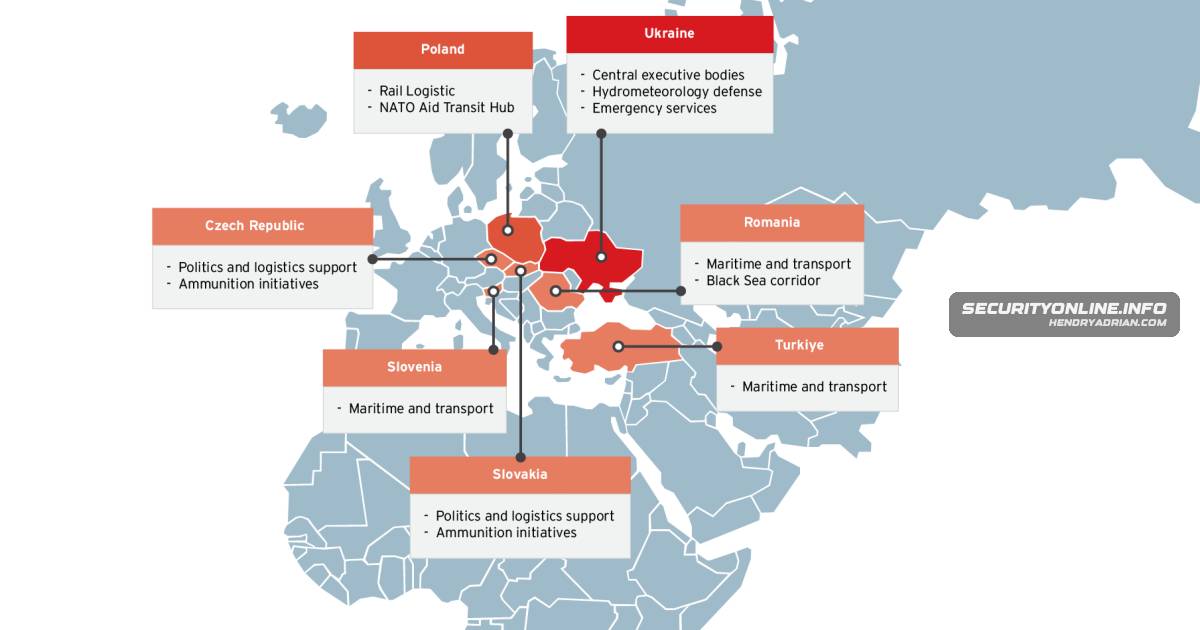
Summary
Trend Micro reports that Pawn Storm used the PRISMEX malware suite in early 2026 against Ukrainian defense and Western military-aid logistics, exploiting two Microsoft vulnerabilities and using steganography, COM hijacking, fileless execution and Filen[.]io for C2.
Key points
- Trend Micro attributes an early-2026 campaign targeting Ukrainian defense and Western military-aid infrastructure to Pawn Storm, also known as APT28.
- The report says the campaign exploited CVE-2026-21513 and CVE-2026-21509; exploitation reportedly began 11 days before a February 10, 2026 patch.
- PRISMEX comprises four named components: PrismexSheet, PrismexDrop, PrismexLoader and PrismexStager.
- PrismexSheet reportedly hides payloads in image data; PrismexDrop establishes persistence through COM hijacking.
- PrismexLoader reportedly extracts payloads using a “Bit Plane Round Robin” algorithm, while PrismexStager uses Filen[.]io for command-and-control.
- Reported targets include Polish rail logistics, transport and maritime sectors in Romania, Slovenia and Turkey, and political and logistics partners in Czechia and Slovakia.
Article Details
- Event Type
- Reported Pawn Storm malware campaign exploiting Windows and Microsoft Office vulnerabilities against Ukrainian defense and Western military-aid logistics.
- Impact
- Trend Micro reports that the campaign used the PRISMEX malware suite for espionage and potential disruption of Ukrainian defense and Western military-aid infrastructure, including NATO logistics and regional transport sectors. The article says the vulnerabilities were exploited in the wild before a patch was released; it reports no specific operational damage.
MITRE ATT&CK
T1027.003 · SteganographyThe reported PRISMEX campaign uses steganography to conceal payloads in image data.T1102.002 · Bidirectional CommunicationThe report says PrismexStager uses the legitimate Filen.io service for command-and-control communications.T1546.015 · Component Object Model HijackingPrismexDrop reportedly establishes persistence through COM hijacking.
CVE
CVE-2026-21509Microsoft · Microsoft 365 Apps for Enterprise; Microsoft · Microsoft Office 2016; +3 moreTrend Micro finds the campaign exploits CVE-2026-21513 and CVE-2026-21509, leverages advanced steganography, fileless techniques, COM hijacking, and Filen.io for C2 to strike NATO logistics hubs and regional transportCVE-2026-21513Microsoft · Windows 10 Version 1607; Microsoft · Windows 10 Version 1809; +19 moreTrend Micro finds the campaign exploits CVE-2026-21513 and CVE-2026-21509, leverages advanced steganography, fileless techniques, COM hijacking, and Filen.io for C2 to strike NATO logistics hubs and regional transport
Threat Actors
Malware
PRISMEXPawn Storm (APT28/Fancy Bear) has escalated operations in early 2026 by deploying a coordinated malware suite called PRISMEX to disrupt Ukrainian defense and Western military aid infrastructure.PrismexDropPrismexDrop: A native dropper that establishes persistence through COM hijacking, effectively allowing the malware to run with the privileges of trusted processes like explorer.exe.PrismexLoaderPrismexLoader: A DLL that extracts payloads using a unique “Bit Plane Round Robin” algorithm.PrismexSheetPrismexSheet: A malicious Excel dropper that uses steganography to hide payloads within binary data.PrismexStagerPrismexStager: A stager that abuses the legitimate cloud service Filen.io for command-and-control (C2) communications, allowing malicious traffic to blend into normal web activity.
Vendors
Products
Filen.ioand CVE-2026-21509, leverages advanced steganography, fileless techniques, COM hijacking, and Filen.io for C2 to strike NATO logistics hubs and regional transport sectors.Microsoft OfficePawn Storm has been observed exploiting a critical Windows zero-day (CVE-2026-21513) in the MSHTML Framework alongside a security feature bypass in Microsoft Office (CVE-2026-21509).Microsoft WindowsPawn Storm has been observed exploiting a critical Windows zero-day (CVE-2026-21513) in the MSHTML Framework alongside a security feature bypass in Microsoft Office (CVE-2026-21509).MSHTML FrameworkPawn Storm has been observed exploiting a critical Windows zero-day (CVE-2026-21513) in the MSHTML Framework alongside a security feature bypass in Microsoft Office (CVE-2026-21509).
Countries
Czech RepublicCzech Republic and Slovakia: Aimed at political and logistical partners involved in ammunition initiatives.PolandTargets include NATO logistics hubs and transport sectors in Poland, Romania, Slovenia, Turkey, Czechia, and Slovakia.RomaniaTargets include NATO logistics hubs and transport sectors in Poland, Romania, Slovenia, Turkey, Czechia, and Slovakia.SlovakiaTargets include NATO logistics hubs and transport sectors in Poland, Romania, Slovenia, Turkey, Czechia, and Slovakia.SloveniaTargets include NATO logistics hubs and transport sectors in Poland, Romania, Slovenia, Turkey, Czechia, and Slovakia.TurkeyTargets include NATO logistics hubs and transport sectors in Poland, Romania, Slovenia, Turkey, Czechia, and Slovakia.UkrainePawn Storm escalated attacks in early 2026 against Ukraine and Western aid networks.