
CERT-UA Reports Few Confirmed Infections in AGEWHEEZE Phishing Campaign
Summary
CERT-UA says a phishing campaign impersonating the agency used AGEWHEEZE malware, with only a few infections confirmed. Cyber Serp claimed far wider compromise, which the article does not independently verify.
Key points
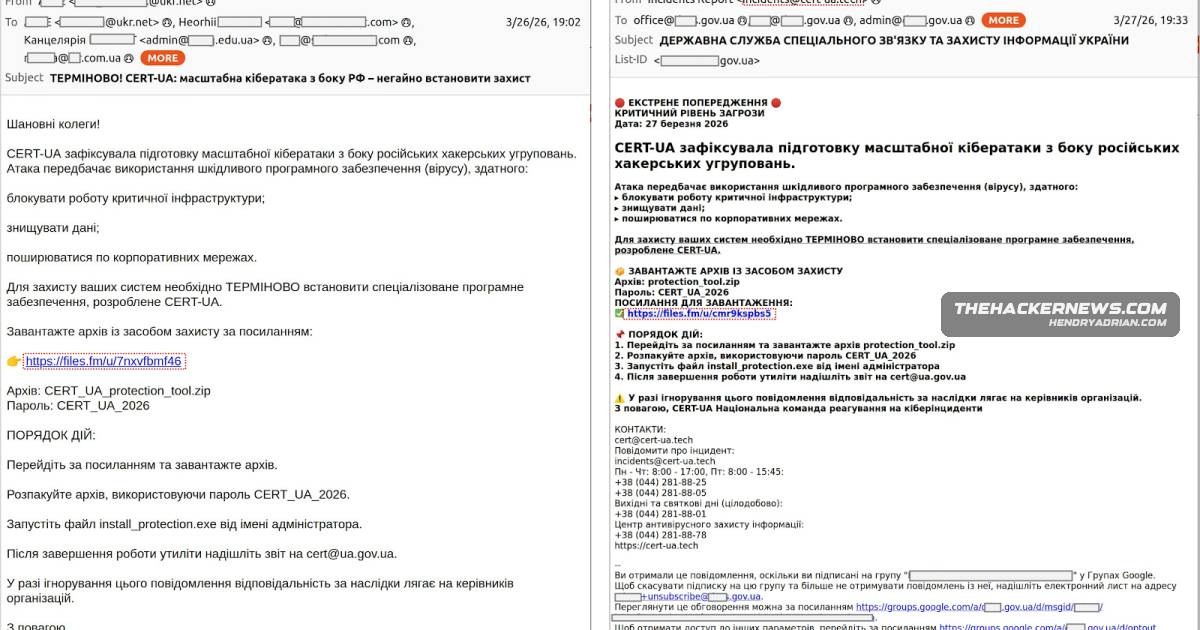
- Emails sent March 26–27, 2026, impersonated CERT-UA and distributed a password-protected ZIP named CERT_UA_protection_tool.zip.
- The ZIP delivered AGEWHEEZE, a Go-based remote access trojan that communicates over WebSockets with 54.36.237.92.
- AGEWHEEZE supports remote commands, file operations, screenshots and input emulation; it can persist through scheduled tasks, Registry changes or the Startup folder.
- CERT-UA said it identified no more than a few infected personal devices belonging to employees of educational institutions.
- Cyber Serp claimed the emails reached 1 million ukr[.]net mailboxes and that more than 200,000 devices were compromised; these claims are not independently confirmed in the article.
- Some emails came from incidents@cert-ua[.]tech, and the fake cert-ua[.]tech site was assessed as likely AI-generated.
- Separately, Cipher acknowledged that an employee's credentials at one of its technology companies were compromised, but said its infrastructure was operating normally and the affected user had access to one project without sensitive data.
Article Details
- Event Type
- Phishing and malware-distribution campaign impersonating CERT-UA to deliver the AGEWHEEZE remote access trojan.
- Impact
- CERT-UA reported only a few confirmed infections, on personal devices belonging to employees of educational institutions. Cyber Serp claimed the emails reached 1 million ukr[.]net mailboxes and compromised more than 200,000 devices; those claims were not confirmed in the article. Separately, Cipher acknowledged that attackers compromised an employee’s credentials but said its infrastructure remained operational and the employee had access to one project that contained no sensitive data.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cert-ua[.]tech | Fake website used in the campaign to impersonate CERT-UA. |
incidents@cert-ua[.]tech | Sender address used for phishing emails impersonating CERT-UA. | |
| IPV4 | 54[.]36[.]237[.]92 | External server AGEWHEEZE communicates with over WebSockets. |
MITRE ATT&CK
Threat Actors
Cyber SerpThe article associates Cyber Serp with the campaign attributed to UAC-0255/Cyber Serp. Cyber Serp claimed the emails reached 1 million mailboxes, that more than 200,000 devices were compromised, and responsibility for an alleged Cipher breach; these claims are not confirmed, and the reported campaign infections were limited.UAC-0255The campaign was tracked as UAC-0255 and attributed in the article to UAC-0255/Cyber Serp. The article does not clearly establish whether these names are aliases.
Malware
Products
Countries
Industries
CybersecurityResponse Team of Ukraine (CERT-UA) has disclosed details of a new phishing campaign in which the cybersecurity agency itself was impersonated to distribute a remote administration tool known as AGEWHEEZE.Software developmentThe targets of the campaign included state organizations, medical centers, security companies, educational institutions, financial institutions, and software development companies.