
MuddyWater Used Chaos Ransomware as Espionage Decoy, Rapid7 Says
Summary
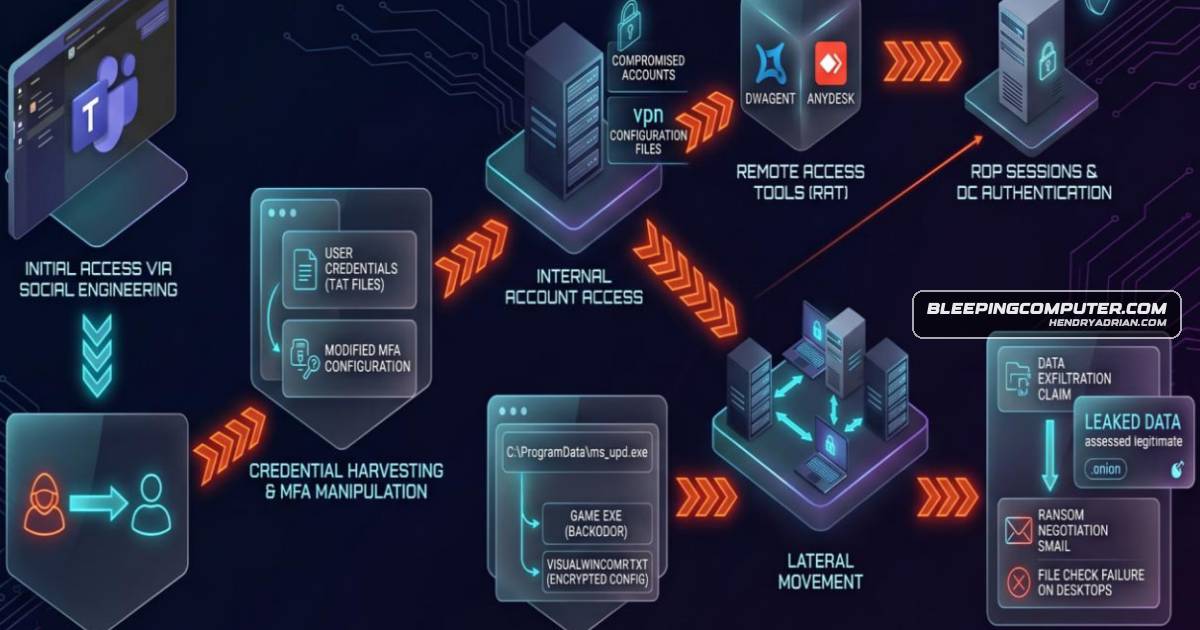
Rapid7 says an intrusion it investigated used Chaos ransomware as cover for suspected MuddyWater espionage, with Microsoft Teams social engineering, credential theft, MFA manipulation and remote-access tools. Attribution is moderate-confidence.
Key points
- Rapid7 attributes the intrusion to MuddyWater with moderate confidence, citing infrastructure overlap, a code-signing certificate linked to Stagecomp and Darkcomp, and operational tradecraft.
- Attackers reportedly initiated Microsoft Teams chats and screen-sharing sessions to harvest credentials, manipulate MFA settings and sometimes deploy AnyDesk.
- Credential theft reportedly used phishing pages posing as Microsoft Quick Assist or tricked victims into entering passwords in local text files.
- After compromising accounts, attackers accessed internal systems including a domain controller and established persistence using RDP, DWAgent and AnyDesk.
- The loader ms_upd.exe dropped Game.exe, disguised as a Microsoft WebView2 application; Rapid7 says the backdoor has anti-analysis and anti-VM checks and supports 12 commands.
- Rapid7 assesses that the Chaos ransomware activity and related extortion claims likely served to conceal the suspected espionage operation rather than pursue financial gain.
Article Details
- Event Type
- A cyber-espionage intrusion reportedly disguised as a Chaos ransomware attack, with Rapid7 attributing it to MuddyWater at moderate confidence.
- Impact
- Attackers used Microsoft Teams social engineering to harvest credentials and manipulate MFA settings, then accessed internal systems and established remote persistence using RDP, DWAgent, AnyDesk, and a custom backdoor. The reported activity included data exfiltration and extortion emails; Rapid7 suggests the ransomware appearance was intended to conceal espionage rather than pursue financial gain.
MITRE ATT&CK
T1021.001 · Remote Desktop ProtocolThe attackers used RDP to establish persistence and access internal systems.T1056.003 · Web Portal CaptureThe attackers used phishing pages masquerading as Microsoft Quick Assist to capture credentials.T1059.001 · PowerShellThe backdoor supports PowerShell command execution.T1059.003 · Windows Command ShellThe backdoor supports CMD command execution.T1219 · Remote Access ToolsThe attackers used AnyDesk and DWAgent for remote access.T1556.006 · Multi-Factor AuthenticationThe attackers manipulated victims' multi-factor authentication settings.
Threat Actors
chaosThe article describes Chaos as a ransomware-as-a-service operation. The reported intrusion was presented as a Chaos ransomware attack, but Rapid7 assessed that it was likely a cover for MuddyWater espionage rather than evidence of Chaos's involvement.Mango SandstormThe article identifies Mango Sandstorm as another name for MuddyWater, which Rapid7 attributed to the intrusion with moderate confidence.MuddyWaterRapid7 attributed the intrusion to MuddyWater with moderate confidence, citing infrastructure overlap, a code-signing certificate, and operational tradecraft.QilinThe article reports that MuddyWater deployed Qilin ransomware in a late-2025 attack against an Israeli organization.SeedwormThe article identifies Seedworm as another name for MuddyWater, which Rapid7 attributed to the intrusion with moderate confidence.Static KittenThe article identifies Static Kitten as another name for MuddyWater, which Rapid7 attributed to the intrusion with moderate confidence.
Malware
ChaosMuddyWater disguised a state-sponsored cyber-espionage operation as a Chaos ransomware attack, using Microsoft Teams social engineering to steal credentials, bypass MFA, and establish remote persistence.DarkcompRapid7’s attribution cites infrastructure overlap, a code-signing certificate linked to Stagecomp/Darkcomp, and operational tradecraft pointing to MuddyWater.Game.exe#MuddyWater #Chaos #MicrosoftTeams #Game.exems_upd.exePersistence and remote access were achieved via RDP, DWAgent, AnyDesk, and a custom backdoor (Game.exe) dropped by ms_upd.exe.Qilin#MuddyWater #Chaos #MicrosoftTeams #Game.exeStagecompRapid7’s attribution cites infrastructure overlap, a code-signing certificate linked to Stagecomp/Darkcomp, and operational tradecraft pointing to MuddyWater.
Vendors
Products
AnyDeskPersistence and remote access were achieved via RDP, DWAgent, AnyDesk, and a custom backdoor (Game.exe) dropped by ms_upd.exe.DWAgentPersistence and remote access were achieved via RDP, DWAgent, AnyDesk, and a custom backdoor (Game.exe) dropped by ms_upd.exe.Microsoft Quick AssistCredential theft occurred either via phishing pages masquerading as Microsoft Quick Assist or by tricking victims into typing their passwords into local text files.Microsoft TeamsMuddyWater disguised a state-sponsored cyber-espionage operation as a Chaos ransomware attack, using Microsoft Teams social engineering to steal credentials, bypass MFA, and establish remote persistence.Microsoft WebView2Next, they leveraged a malware loader (ms_upd.exe) to drop a custom backdoor (Game.exe), disguised as a Microsoft WebView2 application.