
Cisco Talos Tracks China-Nexus UAT-8302 Campaign Targeting Government Agencies
Summary
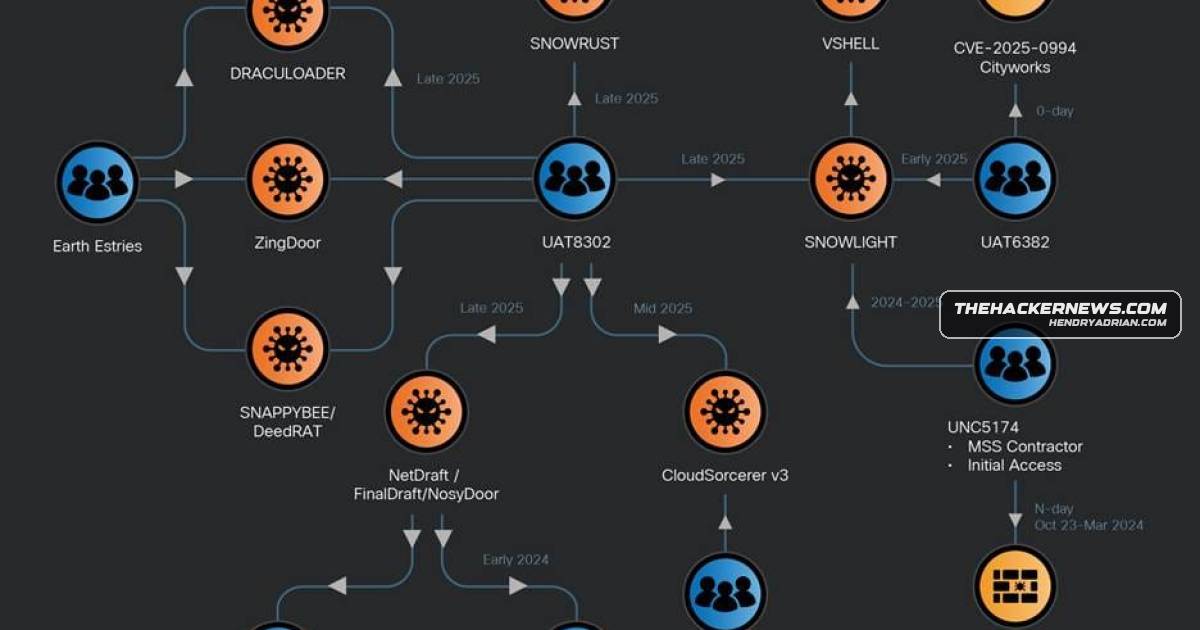
Cisco Talos attributes attacks on South American and southeastern European government entities to China-nexus APT UAT-8302, which deploys NetDraft, CloudSorcerer and VShell; initial access is suspected to involve web-application exploits.
Key points
- Talos tracks UAT-8302 activity against South American government entities since late 2024 and southeastern European agencies in 2025.
- Post-compromise activity includes deployment of NetDraft (also known as NosyDoor), CloudSorcerer v3.0 and VShell.
- The Rust-based SNOWRUST, a variant of SNOWLIGHT, retrieves and executes VShell; Stowaway and SoftEther VPN are used for alternative backdoor access.
- Operators conduct network reconnaissance, use gogo for automated scanning and move laterally. Initial access is unknown but suspected to involve weaponized zero-day or N-day web-application exploits.
- Talos says shared malware artifacts indicate operating relationships with other China-aligned threat clusters.
- The article also describes Trend Micro's broader “Premier Pass-as-a-Service” model, in which Earth Estries passes initial access to Earth Naga for follow-on activity.
Article Details
- Event Type
- Reported China-nexus APT campaign targeting government entities in South America and southeastern Europe, with custom malware deployment and reported sharing of tools and access among threat groups.
- Impact
- UAT-8302 has targeted South American government entities since late 2024 and agencies in southeastern Europe in 2025. Reported activity includes network reconnaissance, lateral movement, and deployment of backdoors and other malware. Initial access methods are unknown; weaponized web-application exploits are suspected.
MITRE ATT&CK
People
Asheer MalhotraCisco Talos researcher named as a co-author of the technical report describing UAT-8302's activity.Brandon WhiteCisco Talos researcher named as a co-author of the technical report describing UAT-8302's activity.Jungsoo AnCisco Talos researcher named as a co-author of the technical report describing UAT-8302's activity.
Threat Actors
CL-STA-0049Reported as one of the threat clusters previously associated with NetDraft/NosyDoor.Earth AluxReported as one of the threat clusters previously associated with NetDraft/NosyDoor.Earth EstriesTrend Micro reported that Earth Estries obtained initial access and passed it to Earth Naga for follow-on exploitation under the described “Premier Pass-as-a-Service” model.Earth NagaTrend Micro reported that Earth Naga received initial access from Earth Estries for follow-on exploitation under the described “Premier Pass-as-a-Service” model.Ink DragonReported as one of the threat clusters previously associated with NetDraft/NosyDoor.JewelbugReported as one of the threat clusters previously associated with NetDraft/NosyDoor.LongNosedGoblinESET tracks the use of NosyDoor to this group.REF7707Reported as one of the threat clusters previously associated with NetDraft/NosyDoor.Space PiratesNamed in the article as an alternative name for Erudite Mogwai, which Solar reported deployed NosyDoor against Russian IT organizations.UAT-8302Cisco Talos attributes attacks on government entities in South America since late 2024 and southeastern European agencies in 2025 to this China-nexus APT. Reported activity includes reconnaissance, lateral movement, and deployment of custom malware.WebwormNamed in the article as an alternative name for Erudite Mogwai, which Solar reported deployed NosyDoor against Russian IT organizations.
Malware
CloudSorcererThe group uses tools such as the .NET backdoor NetDraft (NosyDoor), CloudSorcerer, VShell and SNOWRUST, and appears to share access and tooling with other China-aligned actors under models like “PremierFinalDraftamong the malware families is a .NET-based backdoor dubbed NetDraft (aka NosyDoor), a C# variant of FINALDRAFT (aka Squidoor) that has been previously linked to threat clusters known as Ink Dragon, CL-STA-0049,NetDraft (NosyDoor)The group uses tools such as the .NET backdoor NetDraft (NosyDoor), CloudSorcerer, VShell and SNOWRUST, and appears to share access and tooling with other China-aligned actors under models like “PremierSNOWLIGHTUAT-8302 has also been observed using a Rust-based variant of SNOWLIGHT called SNOWRUST to download the VShell payload from a remote server and execute it.SNOWRUSTThe group uses tools such as the .NET backdoor NetDraft (NosyDoor), CloudSorcerer, VShell and SNOWRUST, and appears to share access and tooling with other China-aligned actors under models like “PremierSQUIDOORfamilies is a .NET-based backdoor dubbed NetDraft (aka NosyDoor), a C# variant of FINALDRAFT (aka Squidoor) that has been previously linked to threat clusters known as Ink Dragon, CL-STA-0049, Earth Alux,VshellThe group uses tools such as the .NET backdoor NetDraft (NosyDoor), CloudSorcerer, VShell and SNOWRUST, and appears to share access and tooling with other China-aligned actors under models like “Premier
Tools
gogoUpon gaining a foothold, the attackers are known to conduct extensive reconnaissance to map out the network, run open-source tools like gogo to perform automated scanning, and move laterally across the environment.SoftEther VPNBesides using custom malware, the threat actor sets up alternative means of backdoor access using proxy and VPN tools like Stowaway and SoftEther VPN.StowawayThe attackers use SNOWRUST to retrieve VShell and employ proxy/VPN tools like Stowaway and SoftEther for persistent access.