
APT37 Uses Trojanized Android Games to Deliver BirdCall Spyware
Summary
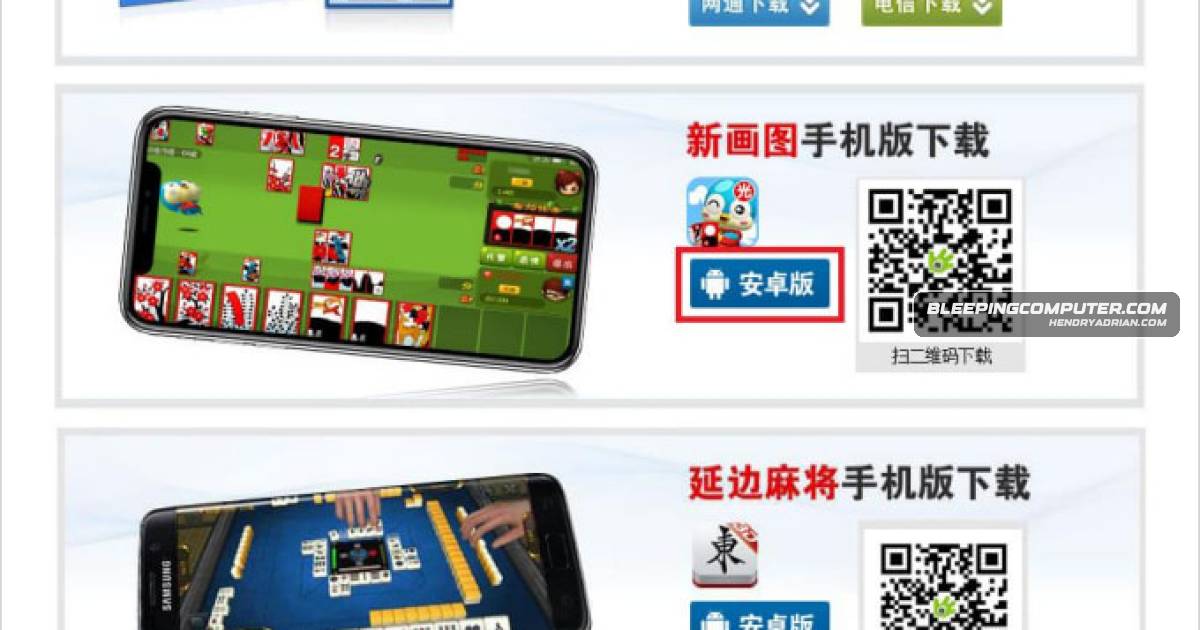
ESET says APT37 delivered at least seven versions of its Android BirdCall backdoor through trojanized APKs on sqgame[.]net, targeting users in China’s Yanbian region and collecting messages, contacts, location, screenshots, audio, and files.
Key points
- ESET attributes the campaign to APT37, which delivered BirdCall through trojanized Android APKs hosted on sqgame[.]net.
- The Android variant was developed around October 2024, with at least seven versions identified.
- BirdCall collects contacts, call logs, SMS, device information, and geolocation; it also takes screenshots, records audio from 7 p.m. to 10 p.m. local time, and exfiltrates files.
- The malware sends system and device information to a command-and-control server and plays a silent MP3 loop to help keep its process running.
- Unlike the Windows version, the Android variant lacks features including shell command execution, traffic proxying, and browser or messenger data targeting.
- Users are advised to download apps only from official marketplaces and trusted publishers.
Article Details
- Event Type
- APT37 reportedly delivered trojanized Android APKs through a compromised game platform in a supply-chain attack.
- Impact
- ESET reported that the Android BirdCall variant can collect contacts, call logs, SMS, device and location information, take screenshots, record audio, and exfiltrate files. The observed attacks targeted users in the Yanbian region of China.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | sqgame[.]net | Compromised game platform through which the reported attacks delivered trojanized APKs. |
Threat Actors
APT37Reportedly delivered the Android BirdCall variant through trojanized APKs on sqgame[.]net. The article identifies ScarCruft and Ricochet Chollima as alternate names for APT37.Ricochet ChollimaReportedly delivered the Android BirdCall variant through trojanized APKs on sqgame[.]net. The article identifies Ricochet Chollima as an alternate name for APT37.
Malware
BirdCallAPT37 (aka ScarCruft/Ricochet Chollima) delivered an Android variant of the BirdCall backdoor through trojanized APKs on the sqgame[.]net game platform.RokRATOn Windows systems, the infection chain begins with the installation of a trojanized DLL (mono.dll) that downloads and executes RokRAT, which then deploys the Windows version of BirdCall.
Products
AndroidAPT37 (aka ScarCruft/Ricochet Chollima) delivered an Android variant of the BirdCall backdoor through trojanized APKs on the sqgame[.]net game platform.Microsoft WindowsThe Android build lacks several Windows BirdCall features, such as shell command execution, traffic proxying, browser/messenger targeting, and process killing.