
Trojanized DAEMON Tools Installers Deliver Backdoors in Ongoing Supply-Chain Attack
Summary
Kaspersky says trojanized, digitally signed DAEMON Tools installers infected thousands across 100+ countries since April 8; about a dozen high-value systems received second-stage payloads, including QUIC RAT. The campaign is ongoing.
Key points
- Kaspersky reports trojanized DAEMON Tools versions 12.5.0.2421–12.5.0.2434, including DTHelper.exe, DiscSoftBusServiceLite.exe, and DTShellHlp.exe.
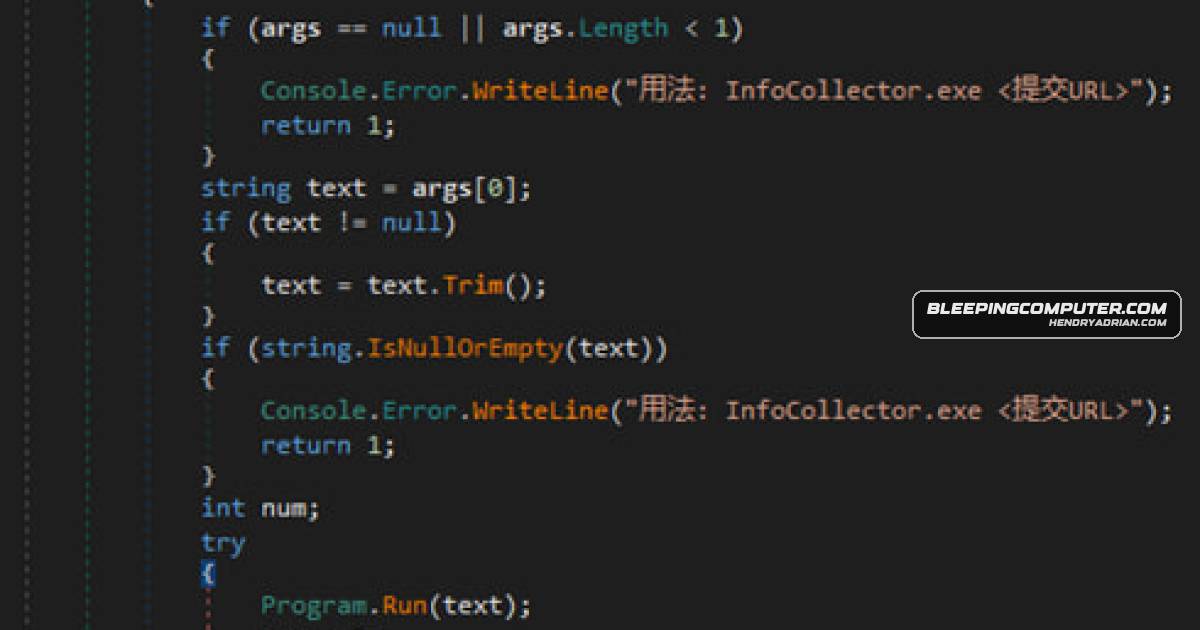
- The first-stage payload collects host and system information, including hostnames, MAC addresses, running processes, installed software, and system locale.
- Some profiled systems received a lightweight backdoor that can execute commands, download files, and run code in memory.
- Kaspersky says thousands of systems across more than 100 countries were infected, but second-stage payloads reached only about a dozen machines.
- Targets receiving later-stage payloads included retail, scientific, government, and manufacturing organizations in Russia, Belarus, and Thailand.
- Kaspersky observed QUIC RAT on at least one Russian educational institute’s system; the malware supports multiple communication protocols and can inject code into legitimate processes.
- The campaign is ongoing and evaded detection for almost a month; Kaspersky advises organizations that used DAEMON Tools to inspect machines for abnormal activity on or after April 8.
Article Details
- Event Type
- Software supply-chain attack involving trojanized DAEMON Tools installers.
- Impact
- The compromise infected thousands of systems in more than 100 countries. According to Kaspersky, only around a dozen high-value targets received second-stage payloads, including organizations in Russia, Belarus, and Thailand. In at least one case involving a Russian educational institute, attackers deployed QUIC RAT. The attack was reported as ongoing.
MITRE ATT&CK
T1055 · Process InjectionQUIC RAT was reported to inject malicious code into legitimate processes.T1057 · Process DiscoveryThe first-stage payload collected information about running processes.T1082 · System Information DiscoveryThe first-stage payload collected system information, including hostname, MAC address, and system locale.T1105 · Ingress Tool TransferThe backdoor could download additional files or payloads.T1518 · Software DiscoveryThe first-stage payload collected information about installed software.
Malware
Vendors
Products
Countries
Belaruscountries since April 8, while only about a dozen high-value targets—including organizations in Russia, Belarus, and Thailand—received second-stage payloads such as a lightweight backdoor and QUIC RAT.Russiathan 100 countries since April 8, while only about a dozen high-value targets—including organizations in Russia, Belarus, and Thailand—received second-stage payloads such as a lightweight backdoor and QUIC RAT.ThailandApril 8, while only about a dozen high-value targets—including organizations in Russia, Belarus, and Thailand—received second-stage payloads such as a lightweight backdoor and QUIC RAT.
Industries
GovernmentOnly around a dozen machines received next-stage payloads—targeting retail, scientific, government, and manufacturing organizations in Russia, Belarus, and Thailand—despite infections in thousands across 100+ countries.ManufacturingOnly around a dozen machines received next-stage payloads—targeting retail, scientific, government, and manufacturing organizations in Russia, Belarus, and Thailand—despite infections in thousands across 100+ countries.RetailOnly around a dozen machines received next-stage payloads—targeting retail, scientific, government, and manufacturing organizations in Russia, Belarus, and Thailand—despite infections in thousands across 100+ countries.