cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · securityweek.com

The Human IOC: Why Security Professionals Struggle With Social Vetting

The author argues that security teams should vet negative information about people and organizations as rigorously as security intelligence, and suggests asking questions, requesting evidence, contacting the target, and assessing the source's history.
Mar 12, 2026
Security Insights · cyberbuilders.substack.com

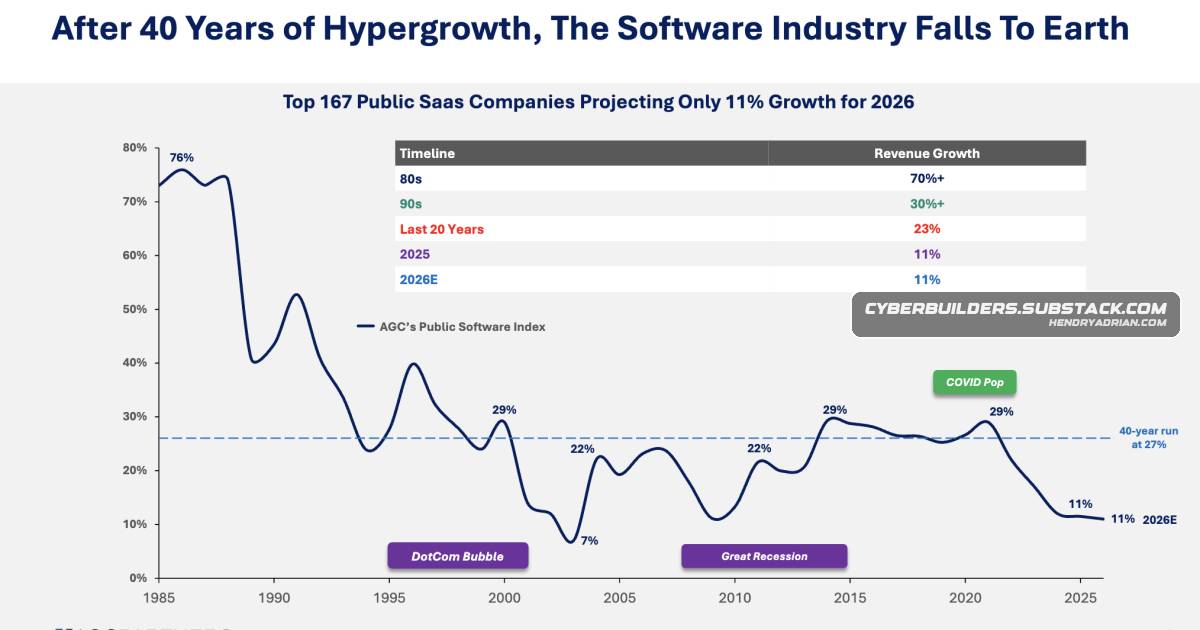
AI Is Challenging Seat-Based Software Models—and Cybersecurity Vendors Face the Shift

The article examines how slowing SaaS growth and AI agents could disrupt seat-based software economics, while cybersecurity remains a distinct, growing market facing consolidation and questions about AI, bundling, and tool stacks.

Mar 12, 2026
Security Insights · cybersecurityclub.substack.com

HTB Academy Offers Hands-On Ethical Hacking Training Paths

A promotional overview of HTB Academy’s hands-on cybersecurity training, including role-based and skill-based learning paths, offensive security modules, and a signup offer for 50 free cubes.

Mar 12, 2026
Security Insights · cybersecurityclub.substack.com

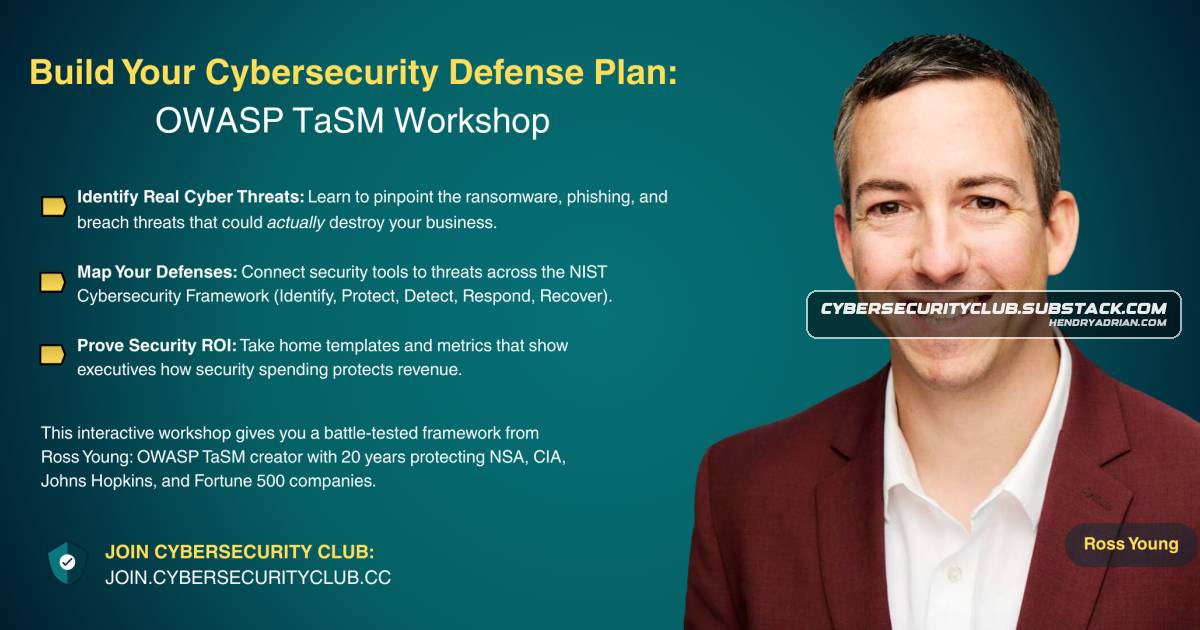
Use NIST CSF and Threat Mapping to Find Gaps in Your Security Program

The article recommends mapping controls across the NIST Cybersecurity Framework’s five functions, then using the TaSM framework to prioritize safeguards against business-relevant threats. It promotes a virtual workshop on the approach.

Mar 11, 2026
Security Insights · securityweek.com

CISO Aimee Cardwell on Security Leadership, Burnout and AI-Generated Fraud

CISO Aimee Cardwell discusses leadership, team empowerment and burnout prevention, and warns that AI-generated, personalized email conversations could enable convincing invoice fraud.

Mar 11, 2026
Security Insights · any.run

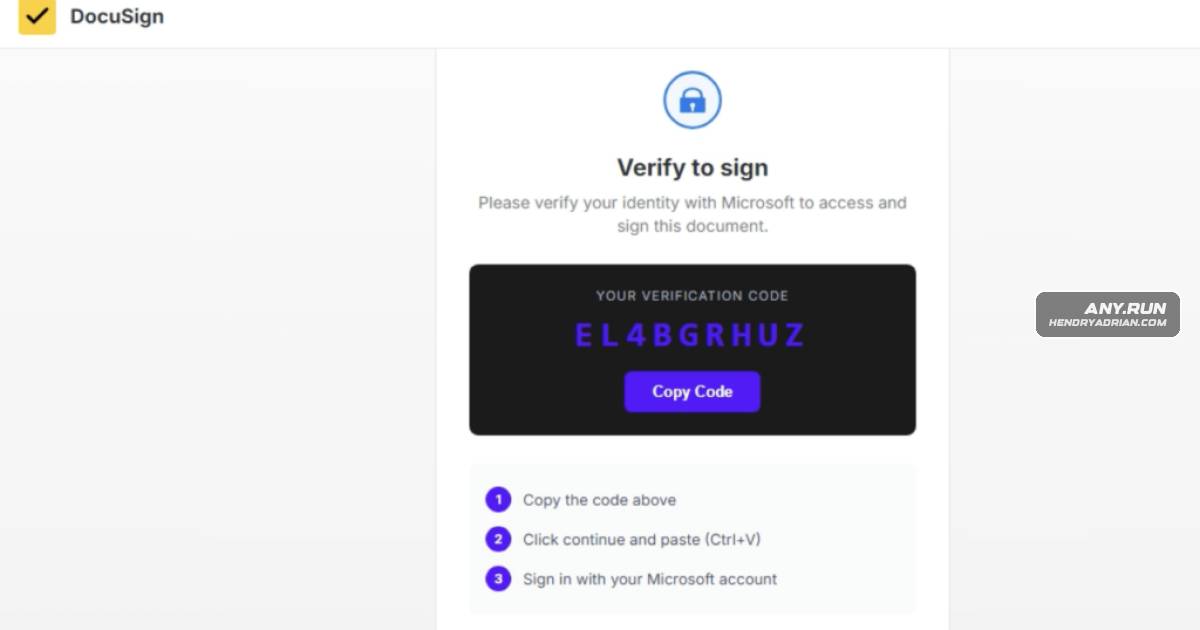
OAuth Device Code Phishing Campaigns Use Microsoft Login Flow to Steal Tokens

ANY.RUN analysts report more than 180 URLs in a week abusing Microsoft OAuth device authorization: victims enter attacker-generated codes on legitimate Microsoft pages, granting attackers tokens. The article describes SSL decryption exposing campaign scripts and network

Mar 11, 2026
Security Insights · picussecurity.com

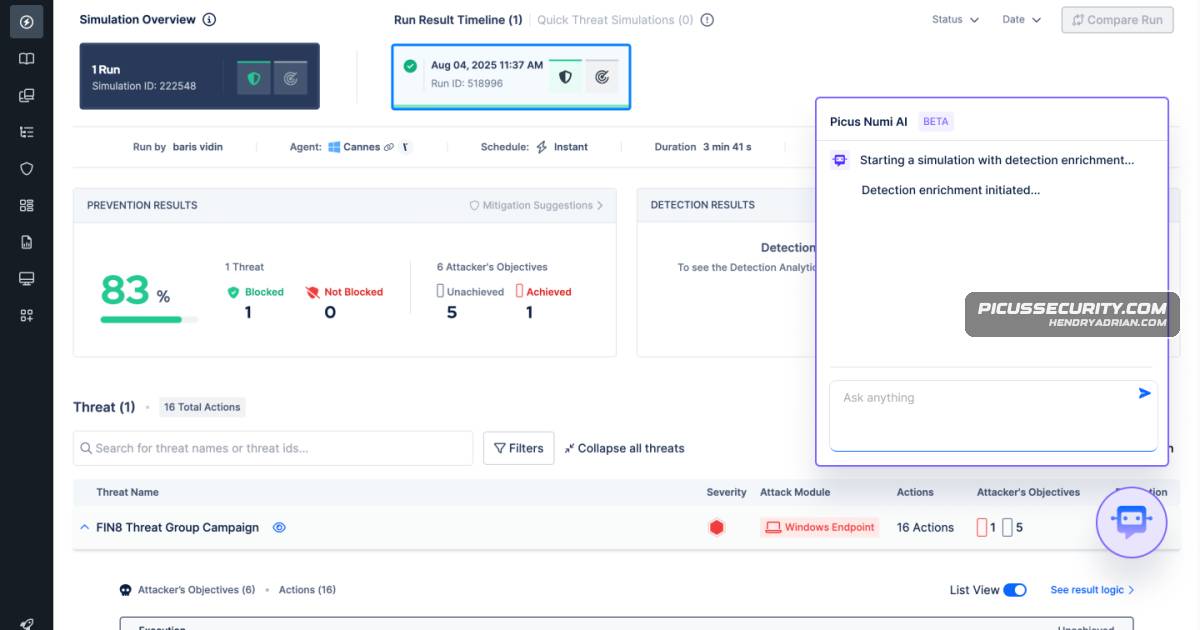
Picus Proposes Four-Agent AI Workflow for Breach-and-Attack Simulation

Picus argues that AI-accelerated attacks widen the gap with manual defense workflows and describes a four-agent BAS approach for turning threat intelligence into safe simulations, evidence-based remediation, and re-testing in minutes.

Mar 10, 2026
Security Insights · thecyberexpress.com

CISO Hannah Suarez: Cyber Risk Management Must Start with the Business

CISO Hannah Suarez says organizations should align cybersecurity with business priorities, clarify cloud and supplier responsibilities, and select framework controls based on risk rather than treating compliance as a checklist.

Mar 10, 2026
Security Insights · specterops.io

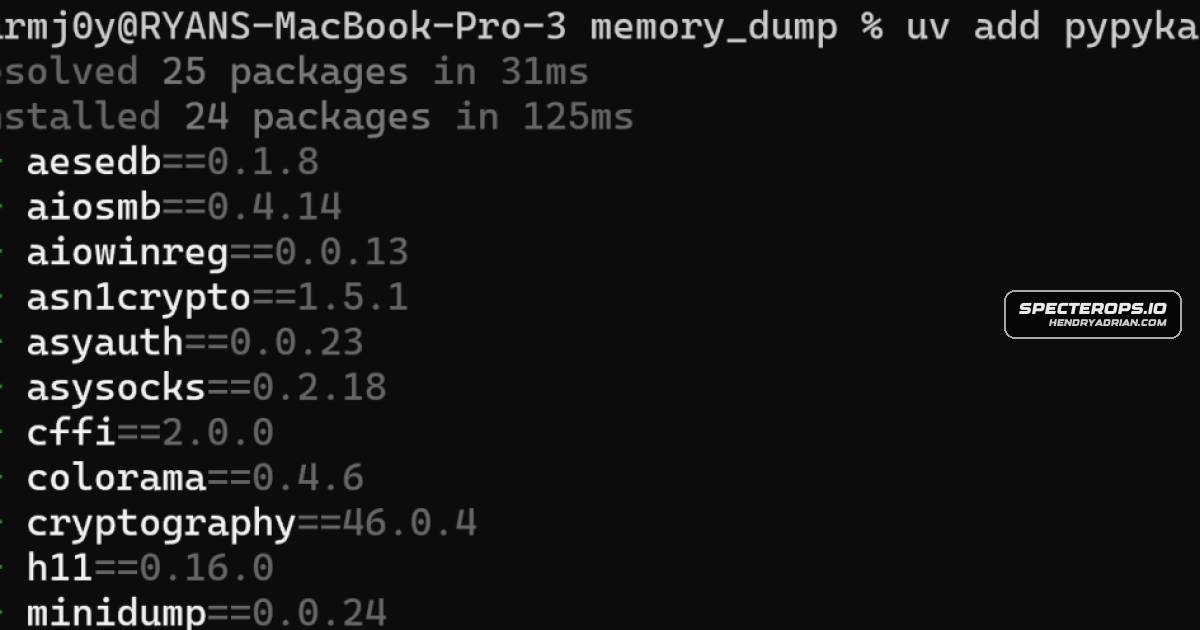
Nemesis 2.X Guide Shows How to Build Enrichment Modules, Rules, and C2 Connectors

A hands-on Nemesis 2.X development guide shows how to build and test file-enrichment modules, including LSASS minidump parsing with pypykatz, customize YARA and Nosey Parker rules, and create C2 connectors, with optional Claude Code and Codex skills.

Mar 10, 2026
Security Insights · team-cymru.com

Thermo Fisher’s Matt McKnew Discusses Ransomware Evolution and Insider Threats

Thermo Fisher incident response manager Matt McKnew discusses how playbooks and documentation improve response, ransomware’s shift to business-like operations, insider threats exploiting weak processes, and DPRK fake IT-worker scams.

Mar 9, 2026
Security Insights · socradar.io

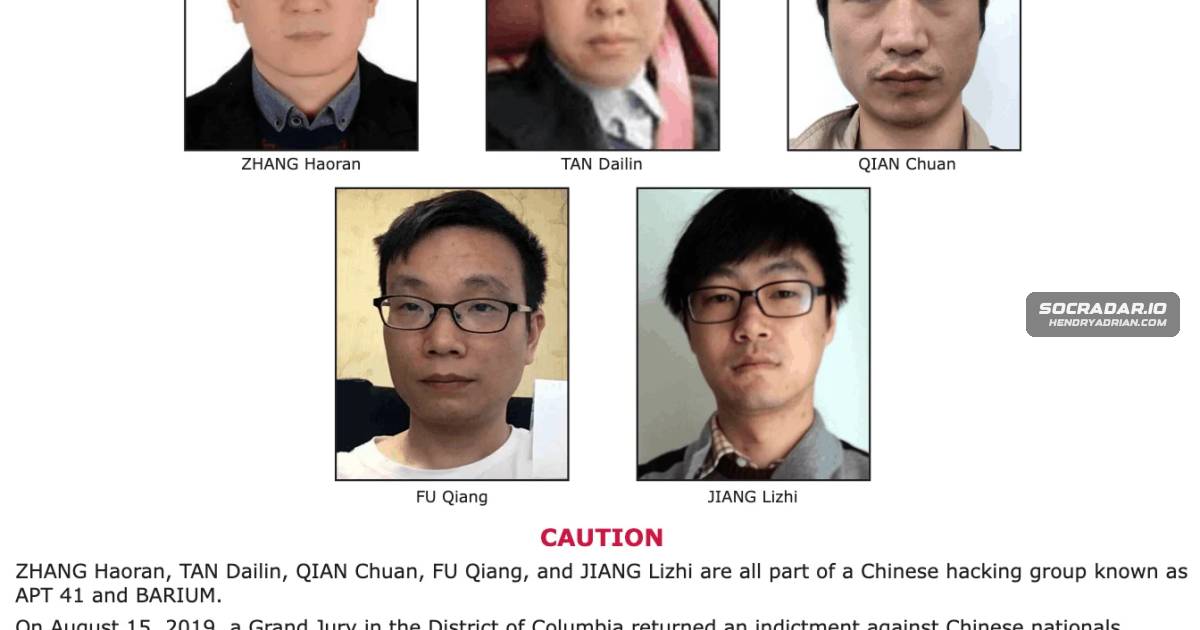
APT41 Profile: Espionage, Cybercrime and Intrusion Tradecraft

The profile describes APT41’s dual espionage and financially motivated activity, exploit-driven access, stealth and persistence techniques, campaigns including TOUGHPROGRESS’s Google Calendar C2, and recommended defenses.

Mar 6, 2026
Security Insights · cloudsek.com

AI-Assisted Reconnaissance Lowers Barriers to Targeting Exposed US Industrial Systems

The article argues that AI can speed reconnaissance of internet-exposed US industrial control systems as Iranian-aligned groups mobilize, drawing on prior CyberAv3ngers activity and recommending restricting access, replacing default credentials, and blocking exposed ICS

Mar 6, 2026
Security Insights · cisecurity.org

How Government Agencies Can Strengthen Software Security with Secure by Design

CIS and SAFECode describe how government agencies can use Secure by Design practices to assess vendor software, build security into development, address legacy risks, and support zero-trust and resilient services.

Mar 5, 2026
Security Insights · darkowl.com

How Ransomware-as-a-Service Affiliates Divide Work and Share Profits

The article explains how ransomware-as-a-service operators and affiliates divide roles, share revenue, and conduct extortion, and why affiliate activity can persist as ransomware brands are disrupted or rebranded.

Mar 5, 2026
Security Insights · huntress.com

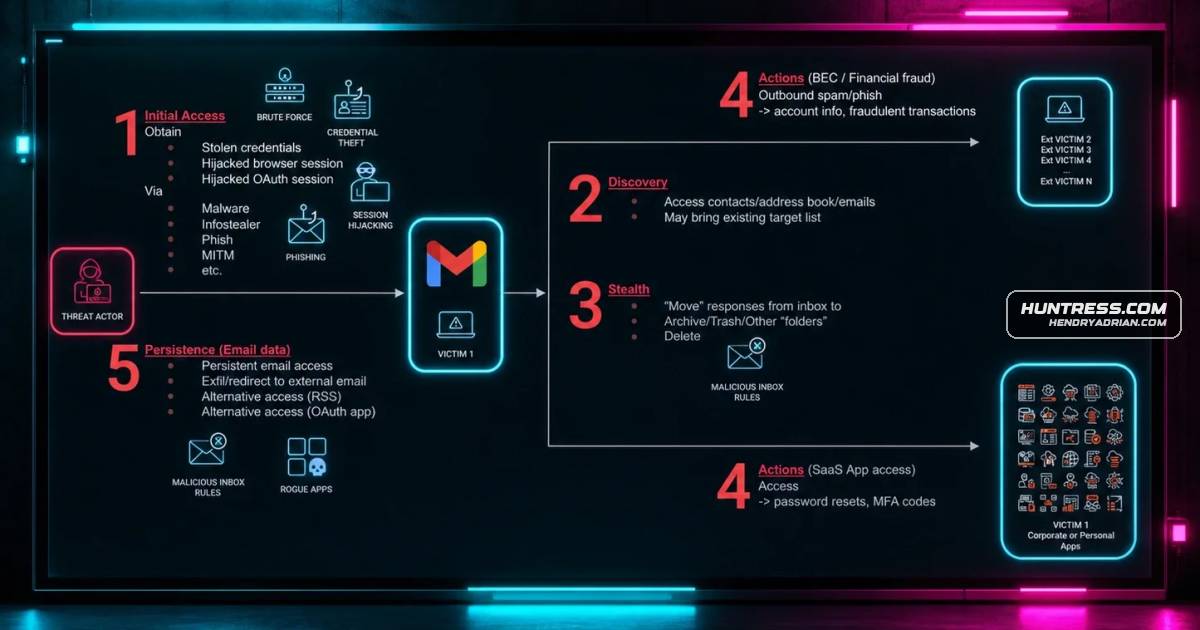
How BEC Attackers Abuse Google Workspace Identity Features

The article explains how BEC campaigns can use stolen credentials, tokens, OAuth abuse, mailbox manipulation and forwarding rules to expand access and hide activity. It recommends monitoring identity behavior and correlating activity across SaaS platforms.

Mar 5, 2026
Security Insights · huntress.com

Change Healthcare Ransomware Attack Highlights Pharmacy Cybersecurity Risks

The Change Healthcare ransomware attack disrupted pharmacy services and exposed healthcare’s reliance on connected vendors. The article outlines defenses pharmacies can adopt, including MFA, EDR, staff training, vendor risk reviews, and offline backups.

Mar 5, 2026
Security Insights · huntress.com

SSO and MFA: How They Differ and Why Organizations Should Use Both

SSO streamlines access to multiple applications through one login, while MFA adds identity checks. The article recommends combining them, favoring passkeys, biometrics, or push factors over SMS and one-time codes.

Mar 5, 2026
Security Insights · team-cymru.com

Tokio Marine HCC Intelligence Lead Says SMBs Face Scaled Ransomware Attacks

Tokio Marine HCC’s Alex Bovicelli says ransomware actors target SMBs at scale, often using brute force against SSL VPNs and other services. He recommends threat modeling, MFA, protected admin access and account lockout policies.

Mar 3, 2026
Security Insights · cybersecurityclub.substack.com

How to Map and Prioritize AI Security Risks with a Threat Matrix

The article outlines how a threat matrix using the TaSM framework can help organizations map and prioritize AI risks, including data leaks, model supply-chain issues, and misuse, and promotes a live workshop on applying it.

Mar 2, 2026
Security Insights · cyberbuilders.substack.com

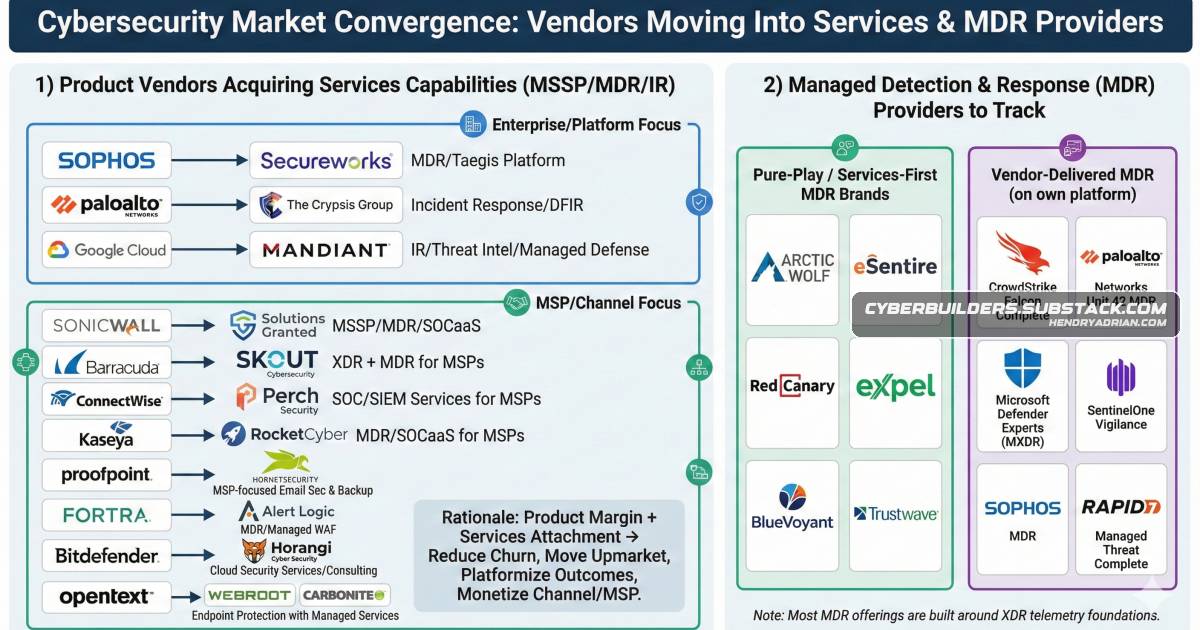
AI Is Reshaping Cybersecurity Services and Managed Defense

The article argues that AI will blur the line between cybersecurity products and services, automate some SOC work, and push service providers toward scalable, continuous, productized managed defense.

Feb 26, 2026
Security Insights · huntress.com

How Trafficking-Fueled Scam Operations Use Manipulation and AI

A Huntress article recounts a trafficking survivor’s account of forced scam work in Southeast Asia, explains pig-butchering tactics and enabling infrastructure, and offers steps to help people avoid fraud.

Feb 26, 2026
Security Insights · darktrace.com

Darktrace Report Highlights Identity Risks and AI-Accelerated Threats for CISOs

Darktrace's 2026 threat report highlights stolen or misused accounts, automated attacks and shrinking exploitation timelines, arguing that CISOs need stronger runtime visibility, rapid response and resilience across AI, cloud and identity systems.

Feb 26, 2026
Security Insights · darkowl.com

Ethical and Legal Guidelines for Dark Web Research

The article explains ethical and legal risks in dark web threat-intelligence research, drawing on DOJ guidance and recommending passive monitoring, written rules of engagement, thorough records, data minimization, and legal review before active engagement.

Feb 24, 2026
Security Insights · cybersecurityclub.substack.com

Cybersecurity Club Shares Cloud Security, Intelligence and Exploitation Learning Resources

Cybersecurity Club highlights resources for cloud security certification, intelligence analysis, Munge vulnerability research, binary exploitation, reverse engineering, and foundational IT learning.

Feb 23, 2026
PreviousPage 38 of 54 Next
© 2026 cyber.hendryadrian.com