
OAuth Device Code Phishing Campaigns Use Microsoft Login Flow to Steal Tokens
Summary
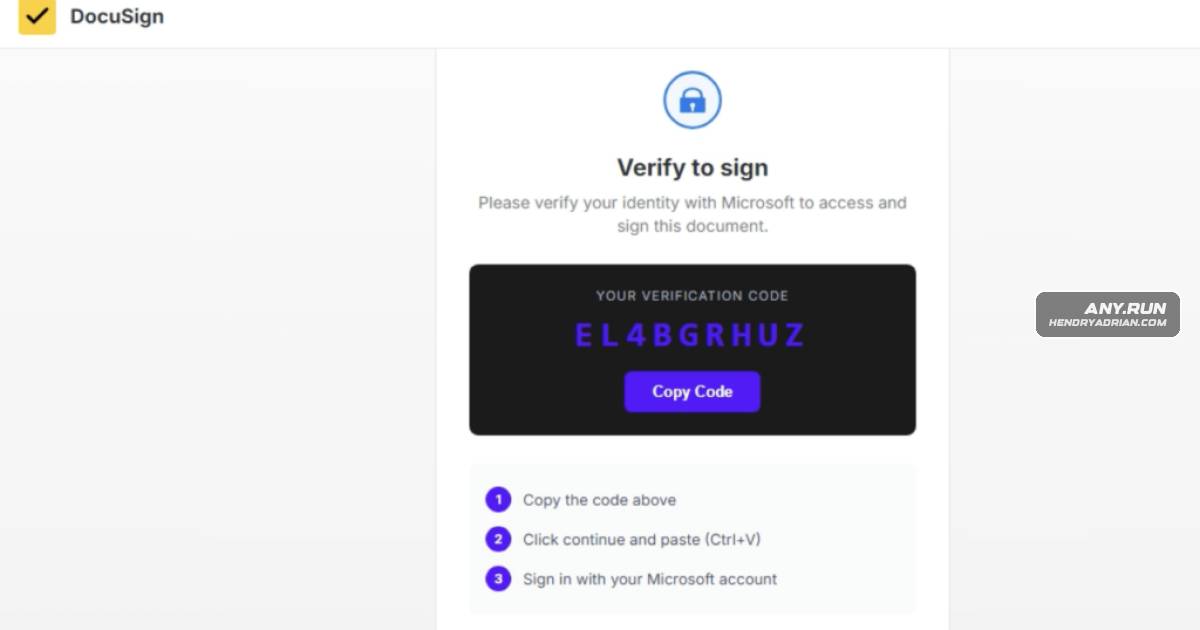
ANY.RUN analysts report more than 180 URLs in a week abusing Microsoft OAuth device authorization: victims enter attacker-generated codes on legitimate Microsoft pages, granting attackers tokens. The article describes SSL decryption exposing campaign scripts and network
Key points
- ANY.RUN analysts report detecting more than 180 phishing URLs in one week, including infrastructure on worker[.]dev and related domains.
- Attackers initiate OAuth device authorization and display a user_code on a phishing page; victims enter it at microsoft[.]com/devicelogin after authenticating on a legitimate Microsoft page.
- The article says this approval can issue access and refresh tokens to attackers without collecting credentials on a fake login page.
- The article describes encrypted HTTPS traffic and legitimate Microsoft infrastructure as obstacles for domain- and form-based phishing detection.
- ANY.RUN says its sandbox can extract TLS keys from process memory to reveal scripts, API requests such as /api/device/start and /api/device/status, and the X-Antibot-Token header.
- Suggested responses include current threat intelligence, sandbox analysis with SSL decryption, and threat hunting to correlate campaign infrastructure.
Article Details
- Topic
- Phishing campaigns abuse Microsoft’s OAuth Device Code flow to induce victims to approve attacker-initiated authorizations, enabling token-based Microsoft 365 account takeover. The article describes SSL decryption as a way to expose the campaigns’ encrypted network activity and phishing infrastructure.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | aarathe-ramraj-tipgroup-com-au-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | ab-monvoisinproduction-com-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | aiinnovationsfly[.]com | Listed as phishing infrastructure associated with the campaign. |
| DOMAIN | andy-bardigans-com-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | astrolinktech[.]com | Listed as phishing infrastructure associated with the campaign. |
| DOMAIN | dennis-saltertrusss-com-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | dibafef289[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | rockymountainhi[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | sandra-solorzano-duncanfamilyfarms-net-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | singer-bodners-bau-at-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | subzero908[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | tyler2miler-proton-me-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
| DOMAIN | workspace1717-outlook-com-s-account[.]workers[.]dev | Listed as phishing infrastructure used by the OAuth Device Code phishing campaign. |
Vendors
ANY.RUNPhishing campaigns abusing Microsoft’s OAuth Device Code flow have rapidly increased, with ANY.RUN analysts detecting more than 180 phishing URLs in a single week that trick victims into approving attacker-initiatedMicrosoftPhishing campaigns abusing Microsoft’s OAuth Device Code flow have rapidly increased, with ANY.RUN analysts detecting more than 180 phishing URLs in a single week that trick victims into approving attacker-initiated
Products
ANY.RUN SandboxANY.RUN Sandbox extracts SSL keys from process memory to decrypt HTTPS traffic, revealing hidden scripts and network activity that enable faster investigations and reduced MTTD and MTTR.Microsoft 365 Apps for EnterpriseAccess tokens and refresh tokens allow attackers to operate within Microsoft 365 without needing stolen credentials.
Tools
Countries
IndiaRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.United StatesRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.
Industries
EducationRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.Financial organizationsCampaign analysis shows targeting of technology companies, educational institutions, financial organizations, and government agencies, although any Microsoft 365 user can be affected.Government & AdministrationRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.ManufacturingRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.TechnologyRecently, the industries most at risk include Technology, Education, Manufacturing, and Government & Administration; primarily in the United States and India, though other countries are also affected.