
Picus Proposes Four-Agent AI Workflow for Breach-and-Attack Simulation
Summary
Picus argues that AI-accelerated attacks widen the gap with manual defense workflows and describes a four-agent BAS approach for turning threat intelligence into safe simulations, evidence-based remediation, and re-testing in minutes.
Key points
- The article argues that LLM-enabled attackers can automate steps such as network mapping and credential dumping, while defenders’ manual handoffs slow threat response.
- A scenario attributed to Picus CTO Volkan Ertürk describes a Fortinet misconfiguration used to reach 2,500 organizations across 106 countries in under an hour; the article provides no incident-specific corroboration.
- Picus’s proposed BAS workflow uses Researcher, Red Teamer, Simulator, and Coordinator agents to move from threat intelligence to remediation.
- The Researcher structures threat intelligence; the Red Teamer matches it to safety-checked atomic tests and builds attack recipes and blueprints.
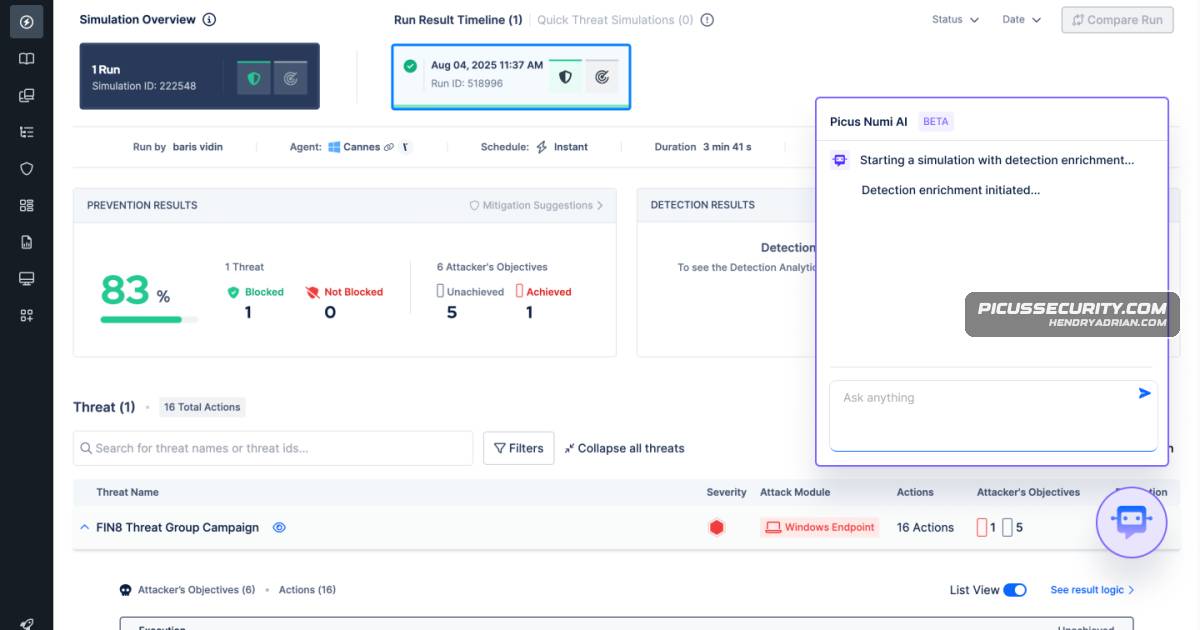
- The Simulator runs tests across endpoint, cloud, network, SIEM, and EDR defenses, producing evidence of detection or blocking; Picus claims 90%+ MITRE ATT&CK coverage.
- The Coordinator can create tickets, trigger SOAR playbooks, and recommend vendor-specific mitigations, with human review or automated deployment and re-simulation to check fixes.
- The article recommends starting with a controlled pilot use case, then moving successful workflows to production with defined metrics.
Article Details
- Topic
- Using generative AI agents to accelerate breach and attack simulation (BAS), security control validation, and remediation.
MITRE ATT&CK
T1003 · OS Credential DumpingThe described attack workflow includes dumping credentials from Active Directory.T1046 · Network Service DiscoveryThe article describes internal network mapping to identify infrastructure and services.T1059 · Command and Scripting InterpreterThe article describes AI-prioritized execution of offensive tools and scripted attack steps.T1078 · Valid AccountsThe article describes using stolen credentials to obtain higher-privilege access, including Domain Admin.T1190 · Exploit Public-Facing ApplicationThe article describes exploiting a Fortinet appliance misconfiguration to gain initial access.T1595 · Active ScanningThe article describes AI-driven vulnerability assessment and scanning as part of the attacker workflow.
People
Vendors
Products
Numi AIThrough its conversational AI interface, Numi AI, security teams can move from navigating complex dashboards to expressing high-level intent, and the platform handles the rest.Picus PlatformHow Picus Platform’s Generative AI Transforms the BAS WorkflowPicus Threat Library[Atomic tests / Test artifacts ] Enterprise atomic test library entries used for simulation – example: Picus Threat Library atomic tests (specific test names or file hashes not listed).Security Control Validation (SCV)customers and more than 12 years of threat research powering its Threat Library, Picus’ Security Control Validation (SCV) module provides the high-fidelity atomic attack sets that make the Red Teamer and Simulator