
Using Impacket DACLEdit to Demonstrate Active Directory Privilege Escalation
Summary
A lab walkthrough shows how misconfigured Active Directory DACLs can enable password resets, Domain Admin group changes, and DCSync, then recommends ACL restoration, auditing, least privilege, and monitoring.
Key points
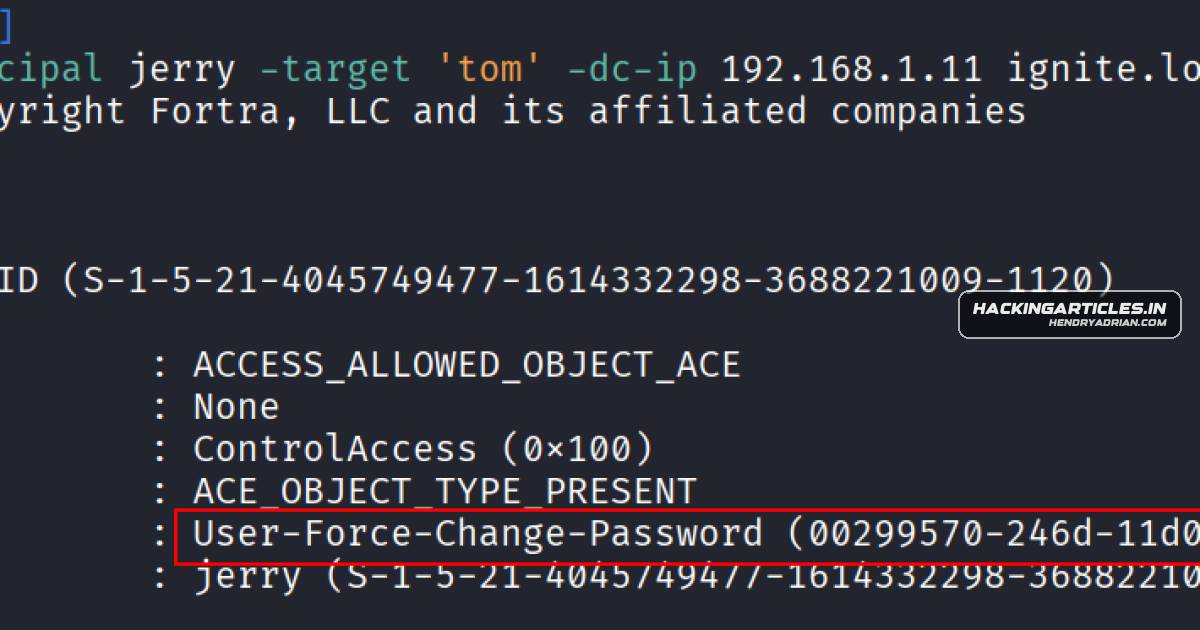
- The ignite.local lab demonstrates ForceChangePassword abuse to reset another user's password, with steps to verify and restore the DACL.
- FullControl or WriteMembers permissions on Domain Admins can let a low-privilege user add themselves to the group.
- Granting both replication rights on the domain root enables DCSync credential dumping, including the krbtgt hash.
- The walkthrough uses Impacket DACLEdit, Impacket secretsdump, NetExec, and bloodyAD.
- Suggested monitoring includes Windows Event IDs 4670, 4728/4732/4756, and 4769 replication-related activity.
- Recommended defenses include auditing sensitive DACLs, least privilege, tiered administration, and rotating the krbtgt password.
Article Details
- Topic
- Active Directory DACL misconfiguration abuse for privilege escalation, privileged-group manipulation, and DCSync credential dumping, with detection and remediation guidance demonstrated in an ignite.local lab.
MITRE ATT&CK
Vendors
Products
Microsoft Active DirectoryDiscretionary Access Control List (DACL) misconfigurations in Active Directory can allow low-privilege users to escalate to Domain Admin and harvest all domain credentials using techniques like ForceChangePassword,Microsoft Defender for IdentityDeploy Microsoft Defender for Identity (MDI) or equivalent — it detects DCSync attempts, suspicious DACL modifications, and lateral movement patterns.
Tools
BloodHoundUse tools like BloodHound, PingCastle, or Semperis DSP to enumerate attack paths.bloodyadThe article demonstrates a full ignite.local lab with exact impacket and bloodyAD commands, verification steps, and DACL restoration guidance, and recommends auditing and monitoring (Event IDs and DCSync indicators) toImpacketThe article demonstrates a full ignite.local lab with exact impacket and bloodyAD commands, verification steps, and DACL restoration guidance, and recommends auditing and monitoring (Event IDs and DCSync indicators) toNetExecNetExec’s change-password module performs the password reset — no knowledge of tom’s current password required:PingCastleUse tools like BloodHound, PingCastle, or Semperis DSP to enumerate attack paths.Semperis DSPUse tools like BloodHound, PingCastle, or Semperis DSP to enumerate attack paths.