cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · bleepingcomputer.com

AI Agents Are Outpacing Fixed Security Workflows, Article Argues for Identity-Based Controls

A sponsored analysis argues that autonomous AI agents outpace fixed security workflows, especially when they inherit human credentials. It recommends a live identity foundation and environment-specific workflows; Token Security says over one-fifth of local agents have.}

Jul 16, 2026
Security Insights · matthewrosenquist.substack.com

How AI Is Reshaping Cybersecurity and Board-Level Risk Oversight

Edna Conway discusses how AI may accelerate vulnerability discovery and exploitation, and how boards and CISOs can address cyber risk through resilience planning, business-focused communication, and cross-functional collaboration.

Jul 15, 2026
Security Insights · hackingarticles.in

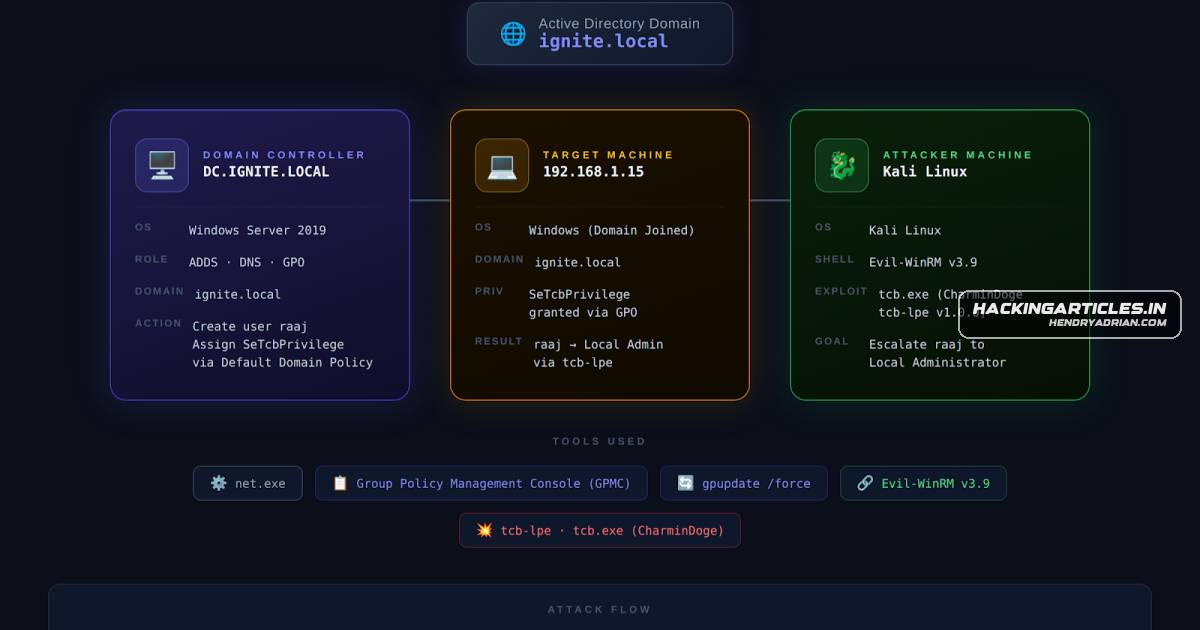
Windows Lab Shows Local Privilege Escalation Through Misassigned SeTcbPrivilege

A lab walkthrough demonstrates how a standard domain account granted SeTcbPrivilege through Group Policy can use tcb-lpe to gain local administrator rights, and outlines auditing, monitoring, and least-privilege mitigations.

Jul 15, 2026
Security Insights · netspi.com

ADPathFinder Maps Cross-Dataset Attack Paths in BloodHound

ADPathFinder combines BloodHound data with OpenGraph collectors to map privilege-escalation paths across AD, ADCS, MSSQL, and SCCM. It also audits cracked passwords with account and graph context and generates reports.

Jul 15, 2026
Security Insights · decodedsecurity.com

3 Reasons I’d Choose a Cybersecurity Career Again

A cybersecurity manager argues that the field remains a strong career choice because demand is real, its breadth creates varied opportunities, and there are paths for people from different backgrounds. The article highlights GRC and privacy roles.

Jul 15, 2026
Security Insights · huntress.com

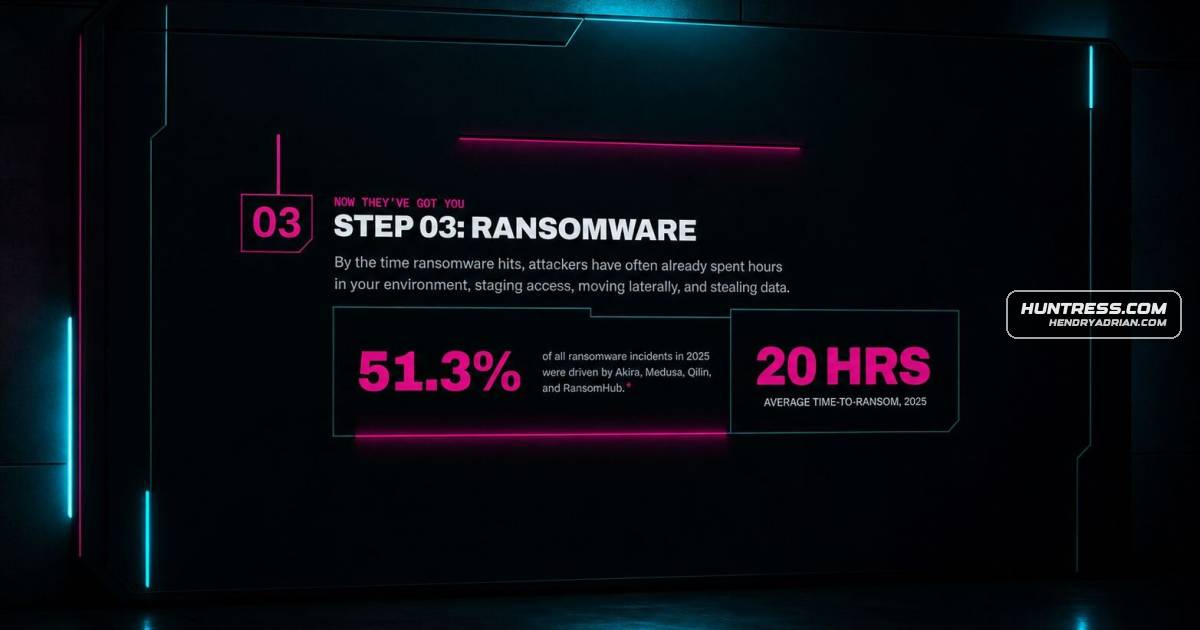
Ransomware Attacks Often Begin Long Before Encryption, Huntress Says

Huntress explains how ransomware intrusions can build through brokered access, identity abuse and trusted-tool misuse before encryption. The article cites six intrusions linked to an exposed Citrix gateway and summarizes 2025 threat trends.

Jul 15, 2026
Security Insights · recordedfuture.com

Anthropic’s Fable Export Controls Highlight Risks of Frontier AI Dependence

The article examines US export controls on Anthropic’s Fable, the uncertainty surrounding the decision, and the security and business risks of relying on frontier AI. It recommends diversified models, fallback options, and resilient workflows.

Jul 15, 2026
Security Insights · thehackernews.com

How SAML AuthnContext and OIDC AMR/ACR Support Step-Up Authentication

The explainer describes how SAML AuthnContext and OpenID Connect AMR and ACR convey authentication methods and assurance levels, helping applications make access decisions and request stronger authentication for sensitive actions.

Jul 14, 2026
Security Insights · aikido.dev

How Aikido Intel Detects Open-Source Malware and Vulnerabilities

Aikido describes Intel’s package-monitoring pipeline, which combines static rules, sandbox analysis, AI and researcher review to flag malware, and tracks project changes to identify potential undisclosed vulnerabilities.

Jul 14, 2026
Security Insights · hackingarticles.in

Windows SeTakeOwnershipPrivilege Can Enable SYSTEM Escalation Through Accessibility Binaries

A lab tutorial shows how misdelegated SeTakeOwnershipPrivilege can let a standard domain user replace Utilman.exe or osk.exe and obtain SYSTEM access on a Windows domain controller; it also recommends policy restrictions, integrity monitoring, NLA and WDAC.

Jul 13, 2026
Security Insights · securityweek.com

Former Blackhat Hacker Jesse McGraw Describes His Shift to OSINT Child-Safety Work

Jesse McGraw, formerly known as GhostExodus, discusses his criminal hacking, including unauthorized access to computers at a Dallas medical facility, and his later shift to legal OSINT work supporting online child safety.

Jul 13, 2026
Security Insights · wiz.io

Why Infrastructure-as-Code Coverage Matters for Cloud Security

The article argues that IaC coverage measures how much cloud infrastructure is governed and traceable through code, and proposes a funnel from resources that could be codified to those mapped to maintainable source code.

Jul 13, 2026
Security Insights · cyberscoop.com

AI-Generated Code Turns Security Debt Into a Governance Challenge

The article argues that AI-assisted development can increase security debt faster than teams can review and remediate it. It cites a Veracode report finding that AI coding tools produce insecure code nearly 45% of the time and recommends controls throughout development.

Jul 13, 2026
Security Insights · cyberbuilders.substack.com

EU Cybersecurity and AI Plan Prompts Call for Greater European Investment and Independence

An analysis of the EU’s cybersecurity and AI action plan argues that Europe should expand independent AI security evaluation, build cyber-focused capabilities, and invest far more in its own AI and cybersecurity ecosystem.

Jul 13, 2026
Security Insights · decodedsecurity.com

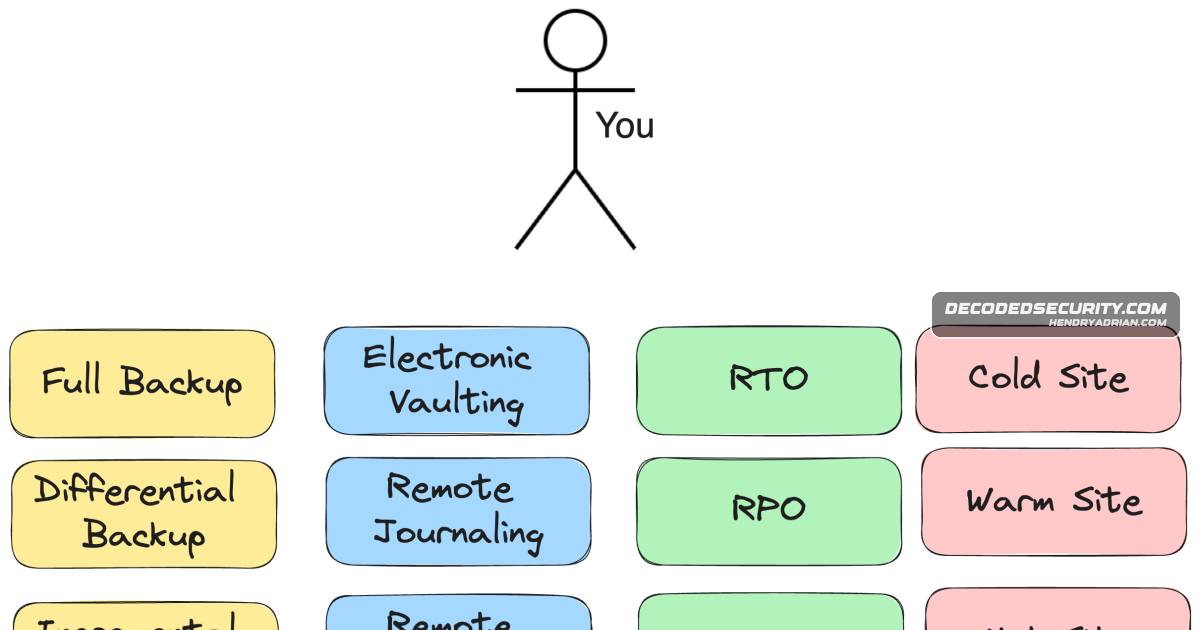
Backup Strategies Explained: Full, Incremental, Differential, and 3-2-1

An explainer compares full, incremental, and differential backups, describes electronic vaulting, remote journaling, and mirroring, and outlines how RPO and the 3-2-1 rule guide resilient backup planning.

Jul 12, 2026
Security Insights · hackingarticles.in

Wireless Pentesting with Claude Desktop and the Aircrack-ng MCP Server

A tutorial uses the Aircrack-ng MCP server with Claude Desktop for wireless testing in an authorized Kali lab, demonstrating WPA2 handshake capture, offline cracking and deauthentication, alongside defenses including WPA3-SAE and Protected Management Frames.

Jul 11, 2026
Security Insights · toxsec.com

Three AI Agent Failures Show the Risks of the “Lethal Trifecta”

Three 2026 agent incidents illustrate how combining untrusted input, sensitive access, and the ability to act can enable persistent prompt injection, browser-mediated token theft, and API-key exposure.

Jul 10, 2026
Security Insights · cisecurity.org

CIS Outlines Five Emerging Security Risks to Large-Scale Events

CIS reviews five emerging risks to major events: drones, synthetic media, extremist attacks, digital ticketing vulnerabilities, and transportation sabotage, and describes planning measures for organizers and public safety officials.

Jul 9, 2026
Security Insights · hackingarticles.in

How Misconfigured SeDebugPrivilege Enables Windows Domain Controller Privilege Escalation

A lab walkthrough demonstrates how granting a standard domain user SeDebugPrivilege can enable LSASS credential extraction or SYSTEM token abuse on a Windows Domain Controller, and outlines Group Policy, LSA Protection, Credential Guard, and monitoring defenses.

Jul 9, 2026
Security Insights · abstract.security

Treat Security Controls as Products Employees Choose to Use

A cybersecurity practitioner argues that security teams should design controls around employees’ work, explain their value, and involve users in decisions. Examples include removable-media restrictions and a collaborative ZTNA rollout.

Jul 9, 2026
Security Insights · huntress.com

How to Build an Effective Security Awareness Training Program

A practical guide to employee security-awareness programs recommends ongoing training, realistic phishing simulations, easy reporting, leadership support, and metrics to help reduce human-related security risks.

Jul 9, 2026
Security Insights · cyberscoop.com

AI Cybersecurity Clearinghouse Must Prioritize Fixes Over Discovery

The 30-day deadline for agencies to establish an AI cybersecurity clearinghouse has passed. The article argues it should prioritize validating, triaging and patching vulnerabilities—not just finding them—and measure remediation outcomes.

Jul 8, 2026
Security Insights · darkowl.com

How Discord and Steam Are Used for Malware, Credential Theft, and Financial Crime

The article explains how criminals and state-linked actors abuse Discord and Steam for phishing, malware delivery, stolen credentials, command-and-control, and money laundering, and how compromised gaming devices can expose enterprise access.

Jul 8, 2026
Security Insights · decodedsecurity.com

A Beginner’s Guide to Recognizing Five Network Denial-of-Service Attacks

A beginner-focused guide explains how to recognize SYN floods, Smurf, Ping of Death, Teardrop, and Land attacks, highlighting identifying network patterns and basic countermeasures.

Jul 8, 2026
PreviousPage 24 of 54 Next
© 2026 cyber.hendryadrian.com