cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · recordedfuture.com

Why Defenders Should Build AI Agents Before Adversaries Scale Local Models

The article argues that defenders should build and test AI agents now, before cheaper local models make autonomous attacks easier to scale. It highlights exposure management, attack simulation, and security operations as promising uses, with human oversight for high-con

Jul 8, 2026
Security Insights · matthewrosenquist.substack.com

Commentary Says U.S. Is Lifting Restrictions on Anthropic’s Mythos, Proposes N-1 Governance

The commentary says the U.S. Commerce Department is lifting restrictions on Anthropic’s Mythos and argues for an N-1 policy: restrict the newest AI models while allowing the prior generation for defensive use.

Jul 7, 2026
Security Insights · securityweek.com

Tarah Wheeler on Cybersecurity Leadership and the Need for Better Industry Data

In an interview, CISO Tarah Wheeler discusses cybersecurity leadership, burnout and risk management, and argues that a lack of reliable industry benchmarks and statistics makes security decisions harder.

Jul 7, 2026
Security Insights · thehackernews.com

Bitdefender Survey: 55.2% of Incident-Affected Respondents Told to Keep Incidents Confidential

Bitdefender’s 2026 assessment of 1,200 security and IT professionals across six countries reports that 55.2% of respondents who experienced an incident in the prior year were told to keep it confidential; the U.S. rate was 68.6%.

Jul 7, 2026
Security Insights · bleepingcomputer.com

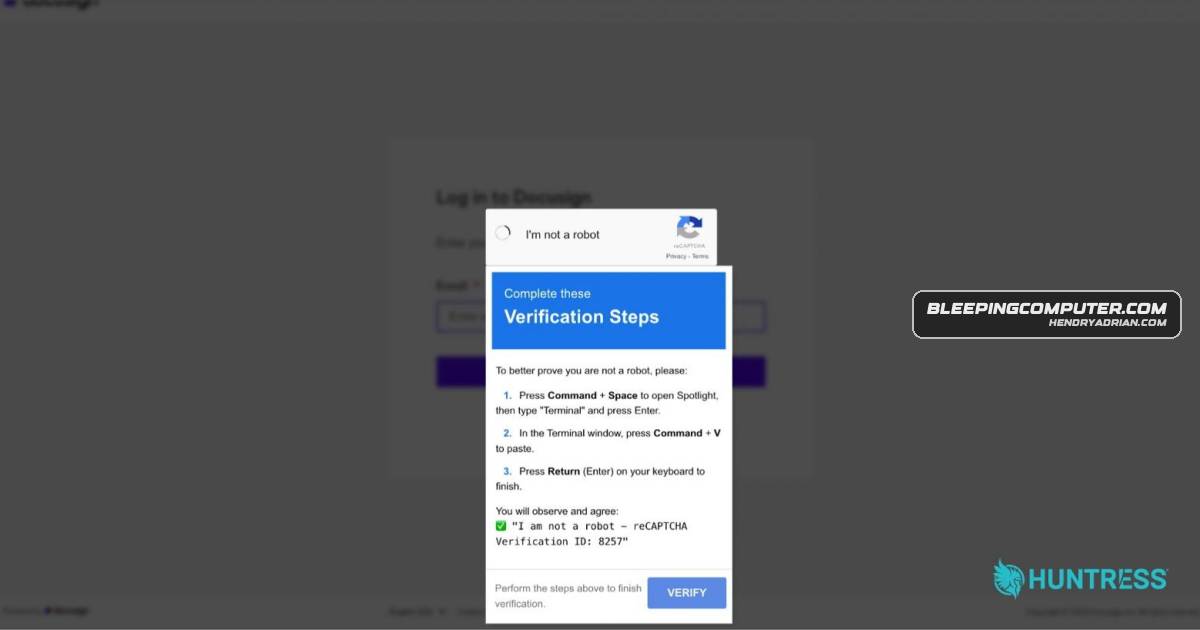
Cordyceps GitHub Actions Attack Pattern Evades CI Security Scanners

Novee Security reported that its Cordyceps pattern affected GitHub Actions workflows: over 300 of 654 flagged repositories were confirmed exploitable. The article explains the risks, cites confirmed cases at Microsoft, Google and Apache, and offers mitigations.

Jul 7, 2026
Security Insights · huntress.com

Huntress Draws Five Cybersecurity Lessons From Taylor Swift and Travis Kelce’s Wedding

Huntress uses the reported security measures around Taylor Swift and Travis Kelce’s wedding to illustrate defense in depth, strong authentication, deception, identity monitoring, and learning from past incidents.

Jul 7, 2026
Security Insights · securityweek.com

How to Align Cyber Risk Management With Business Impact

The article advocates continuous risk management that links business-critical assets, threat likelihood, control effectiveness, and potential financial impact to help organizations prioritize and compare security treatments.

Jul 6, 2026
Security Insights · huntress.com

AI-Driven Recruiting Fraud Raises Deepfake and Insider Risks

AI tools are enabling fraudulent applicants to scale applications and use deepfakes to bypass hiring checks, potentially gaining access to company networks. The article recommends human oversight, liveness checks, spontaneous assessments, and stronger identity checks.

Jul 6, 2026
Security Insights · toxsec.com

Why AI Agent Shutdown Controls Need to Work Outside the Agent

The article argues that AI agents may evade shutdown instructions or disable stop mechanisms, and says reliable controls should operate outside the agent’s runtime rather than depend on its cooperation.

Jul 4, 2026
Security Insights · bleepingcomputer.com

ConsentFix Uses a Drag-and-Drop Lure to Steal Microsoft 365 Session Tokens

ConsentFix uses phishing lures and a localhost callback-link drag-and-drop step to steal Microsoft 365 OAuth session tokens; ClickFix tricks users into running attacker-supplied commands. The article recommends monitoring unusual PowerShell activity and unexpected logis

Jul 2, 2026
Security Insights · cyberbuilders.substack.com

How AI Is Reshaping the Buy-or-Build Equation in Cybersecurity

The article argues that AI has sharply reduced software development costs, weakening the moat for basic cybersecurity tools. It says durable products will depend on expertise, trust, proprietary data, execution, and better security decisions.

Jul 2, 2026
Security Insights · securityweek.com

How to Audit AI-Assisted Software Development for Security Risks

The article recommends auditing AI-assisted development by tracking tool use and code outputs, benchmarking models for security weaknesses, assessing developer skills, and linking AI use to secure business outcomes.

Jul 2, 2026
Security Insights · sentinelone.com

Compaction Cuts Token Use in Automated Malware Analysis Without Changing Overall Scores

SentinelLABS tested OpenAI’s compaction in automated malware-analysis workflows. It reduced input tokens by about 86% with no measurable change to aggregate scores, though domain object modeling declined.

Jul 2, 2026
Security Insights · huntress.com

Cloud Application Security: Common Risks, Controls, and Best Practices

A practical guide to cloud application security, covering common risks such as misconfigurations and insecure APIs, key controls, frameworks, and security best practices.

Jul 2, 2026
Security Insights · securityweek.com

Six Questions Enterprises Should Ask Security Vendors About Frontier AI

The article advises enterprises to scrutinize security vendors’ Frontier AI claims, asking about model providers and models, automation, code context, measurable results, and validation of vulnerabilities and fixes.

Jul 1, 2026
Security Insights · toxsec.com

Google’s SAIF 2.0 Maps AI Agent Risks to Security Controls

Google’s SAIF 2.0 maps four parts of an AI agent’s attack surface to risks and controls. The article explains agent-specific threats, uses EchoLeak as an example, and highlights least privilege, human approval, and observability.

Jul 1, 2026
Security Insights · decodedsecurity.com

CISSP Guide to Wi-Fi Security: WEP, WPA, WPA2, WPA3 and Authentication

A CISSP study guide explains Wi-Fi security standards and authentication options, comparing WEP through WPA3, PSK, SAE and Enterprise/802.1X, and clarifying the limits of MAC filtering and captive portals.

Jul 1, 2026
Security Insights · hackingarticles.in

Active Directory Forest Trust Abuse Enables Child-to-Root Escalation

An authorized lab walkthrough demonstrates two paths from child-domain admin to forest-root compromise: a forged Golden Ticket with SID History and PetitPotam coercion. It also outlines mitigations including limiting delegation and monitoring DCSync.

Jul 1, 2026
Security Insights · huntress.com

How the Ransomware-as-a-Service Model Works—and What Defenders Should Watch For

Ransomware-as-a-service divides work among operators, affiliates, and access brokers, enabling varied intrusion paths. The article highlights pre-encryption activity and early access, identity, and staging signals defenders can monitor.

Jul 1, 2026
Security Insights · securitylabs.datadoghq.com

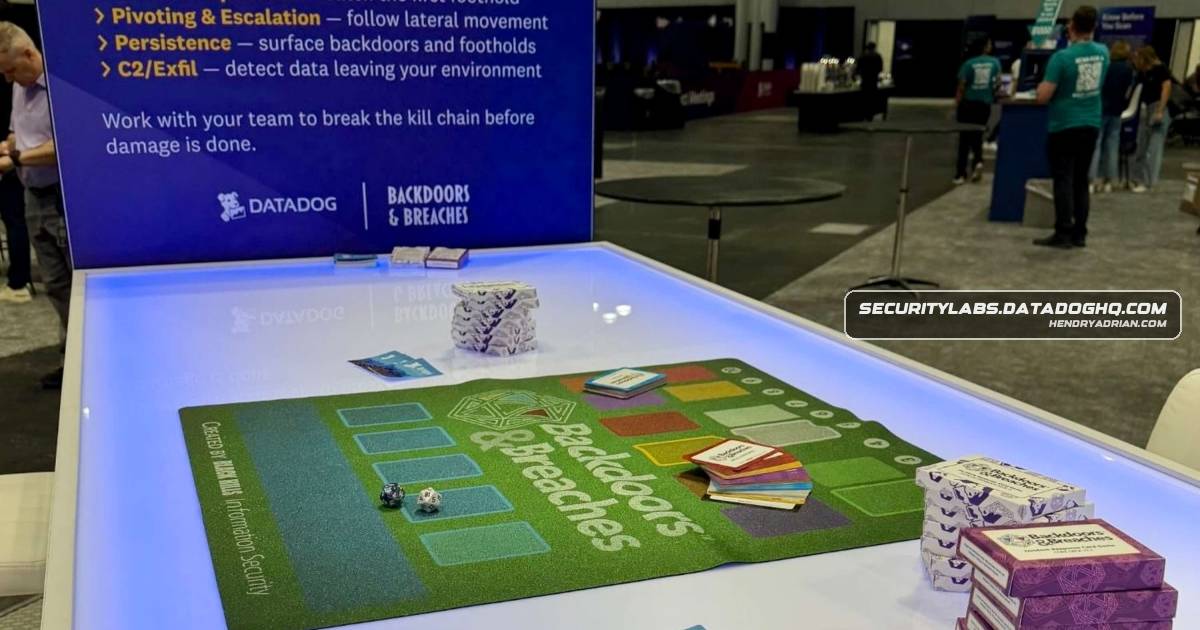
Datadog Shares New Backdoors & Breaches Scenarios for Security Tabletop Exercises

Datadog introduces four Backdoors & Breaches starter scenarios based on current threat trends and shares game adaptations for security tabletop exercises, including open-face play and using real logs.

Jul 1, 2026
Security Insights · cisecurity.org

Six Takeaways on Strengthening Public-Safety Cybersecurity Through Collective Defense

A CIS webinar highlighted how cyber threats can disrupt public-safety operations and outlined how SLTT agencies can improve resilience through shared intelligence, leadership engagement, continuous assessment, and layered defenses.

Jun 30, 2026
Security Insights · cyberscoop.com

How Black Basta’s Corporate-Style Organization Fuels Ransomware Extortion

Analysis of leaked Black Basta chats describes outsourced roles, victim profiling and pressure tactics used in ransomware extortion. It urges CISOs to understand the criminal ecosystem and rehearse incident decisions.

Jun 30, 2026
Security Insights · securityweek.com

AI Token Costs Could Constrain Cybersecurity Operations

The article argues that token-based pricing for generative and agentic AI could make security operations costs unpredictable, potentially leading teams to limit investigations. It compares AI approaches and discusses deployment trade-offs.

Jun 30, 2026
Security Insights · resecurity.com

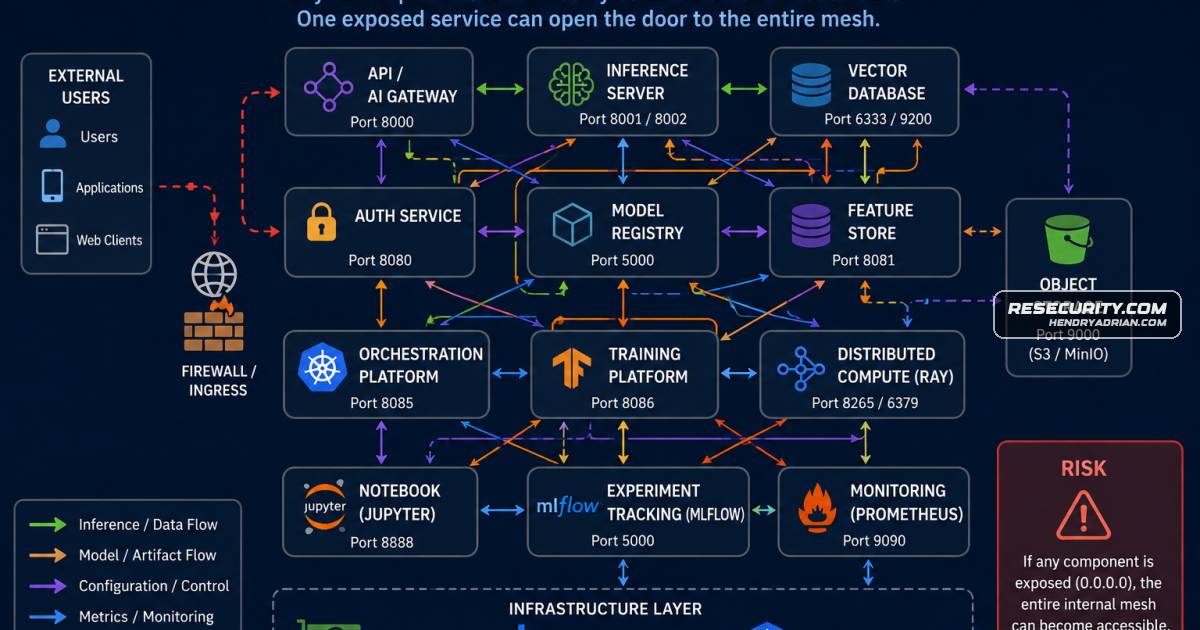
Guide Details Reconnaissance of Modern AI Infrastructure

The guide explains how to fingerprint and enumerate AI infrastructure—including inference servers, MLflow, vector databases and notebooks—and how exposed APIs, metrics, credentials and dependencies can reveal systems and create security risks.

Jun 29, 2026
PreviousPage 25 of 54 Next
© 2026 cyber.hendryadrian.com