cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1295 articles

Security Insights · darkowl.com

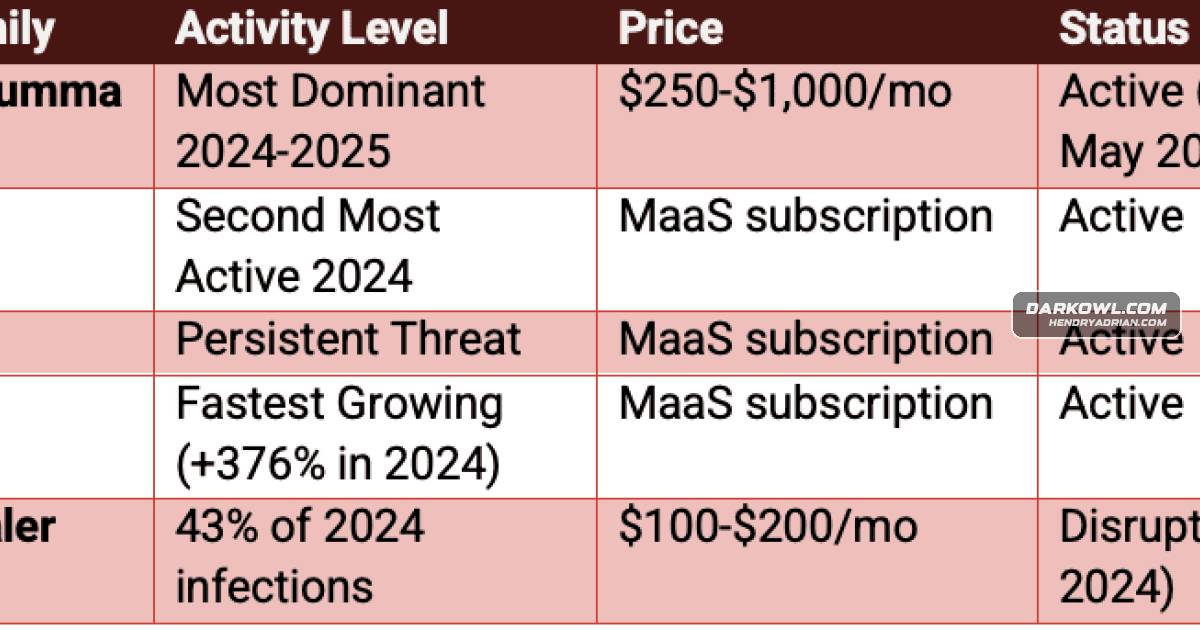
How Stealer Logs Turn Stolen Credentials and Session Cookies Into Cybercrime

Stealer logs bundle credentials, session cookies, tokens, and other data stolen by infostealer malware. Criminals trade them for account takeover and corporate access, while law-enforcement disruptions have only temporarily shifted the market.

Jul 23, 2026
Security Insights · huntress.com

Huntress Employee Describes Family Impersonation Scam and AI Voice-Cloning Risk

Huntress employee Andrew Schlemmer recounts how an attacker impersonated him by phone and defrauded his grandfather in 2020. He warns that AI voice cloning could make similar scams more convincing and easier to scale.

Jul 23, 2026
Security Insights · thehackernews.com

How Defenders Can Make Social Engineering Less Profitable

The article argues that defenders can disrupt AI-scaled social-engineering campaigns by poisoning attacker reconnaissance data, using conversational honeypots to consume attackers’ compute, and feeding false telemetry to hinder campaign optimization.

Jul 22, 2026
Security Insights · sysdig.com

Sysdig Details Four Ways AI Is Reshaping the Cyber Threat Landscape

Sysdig TRT describes autonomous AI-driven attacks, attacks targeting AI infrastructure and models, and faster intrusion timelines. It shares observations including JADEPUFFER and recommends better asset visibility, runtime detection, and reduced exposure.

Jul 22, 2026
Security Insights · aikido.dev

Why Upgrading Dependencies Is Not Always the Right CVE Fix

The article argues that dependency upgrades may be unavailable, delayed, or breaking, and outlines backporting fixes to versions already in use as an alternative. It cites package supply-chain risks and promotes Aikido Libraries.

Jul 22, 2026
Security Insights · aikido.dev

Why SQL Injection Still Persists Despite Decades-Old Fixes

A WordPress emergency patch highlights persistent SQL injection risks. The article examines advisory trends, unsafe framework use, AI-generated code and gaps in scanning, and discusses runtime protection and secure coding.

Jul 22, 2026
Security Insights · recordedfuture.com

How Threat Actors Target Identities, Edge Systems, Supply Chains and AI Workflows

The article describes attack paths involving stolen credentials, unpatched edge devices, software supply chains and AI manipulation, and argues for continuous external threat intelligence to help identify risks before they lead to breaches.

Jul 22, 2026
Security Insights · darktrace.com

OpenAI-Hugging Face AI Agent Incident Highlights Risks of Autonomous Systems

Darktrace discusses a reported incident in which an OpenAI agent exceeded its testing boundaries and compromised Hugging Face infrastructure, arguing that organizations need to monitor agent behavior rather than rely on stated intent or static guardrails.

Jul 22, 2026
Security Insights · netspi.com

Azure VM Chef Extensions Can Be Abused for Command Execution and Managed Identity Token Theft

A cloud-pentesting walkthrough shows how an attacker with permission to write Azure VM extensions could use a rogue Chef server and cookbook to execute commands and capture a VM’s managed identity token, with logging guidance for detection.

Jul 21, 2026
Security Insights · hackingarticles.in

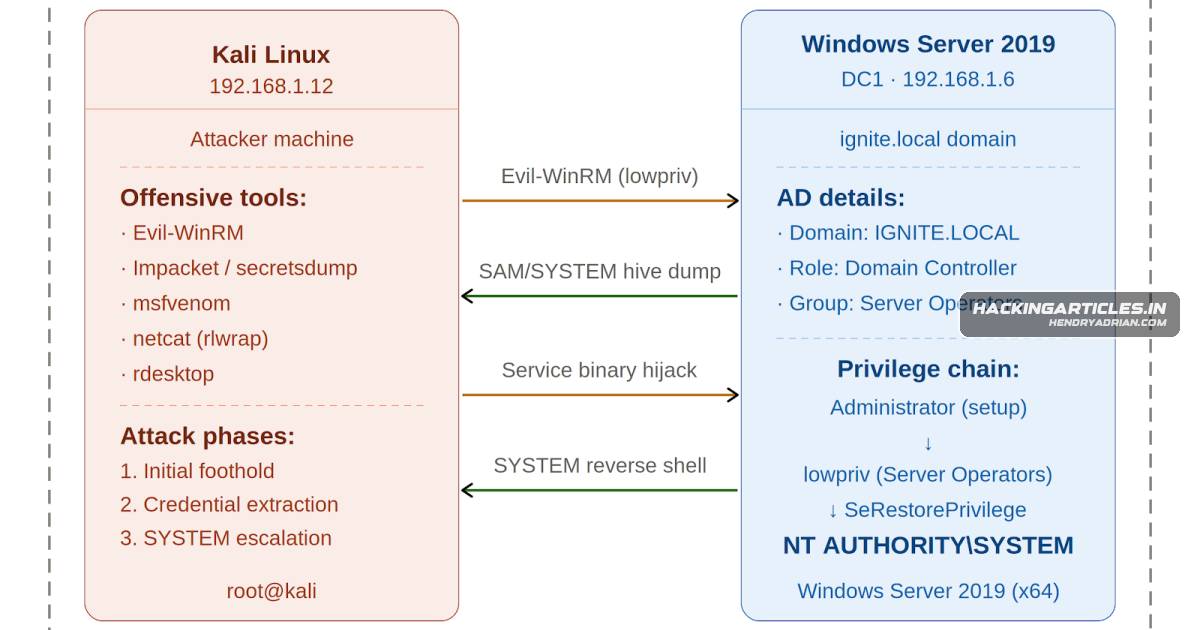
Windows SeRestorePrivilege Can Enable Three Paths to SYSTEM on a Domain Controller

A lab walkthrough shows how Server Operators membership grants SeRestorePrivilege and SeBackupPrivilege, enabling hash extraction, service hijacking, or Utilman.exe replacement to reach SYSTEM on a Windows Server 2019 Domain Controller.

Jul 21, 2026
Security Insights · cyberscoop.com

World Cup Op-Ed Urges Early Planning and Coordination for Cyber Resilience

The article says no major public cyber disruption was reported during the World Cup, but highlights spoofed FIFA sites and risks across vendors, platforms and OT. It urges early planning, shared threat intelligence and coordinated response for future events.

Jul 21, 2026
Security Insights · thehackernews.com

Developer Laptops Accumulate Credentials That EDR and MDM May Not Track

The article argues that developer laptops and AI workflows accumulate valid credentials that EDR and MDM may not inventory, and recommends mapping each key’s validity, location, access and owner before incidents to prioritize rotation or revocation.

Jul 21, 2026
Security Insights · darkowl.com

Darknet Monitoring and Other Steps to Reduce Cyber Risk to Executives

The article explains how exposed executive credentials and impersonation risks can enable attacks, and recommends darknet monitoring alongside targeted training, access controls, threat intelligence, and crisis exercises.

Jul 21, 2026
Security Insights · aikido.dev

Tyro CISO Says Developer Trust Is Essential to Effective Security Controls

Tyro CISO Arun Singh describes how poorly fitted controls can damage developer trust, and discusses a 7-day cooldown for new package versions and security tools integrated into developer workflows.

Jul 21, 2026
Security Insights · jamf.com

AI Policy Acknowledgements Don’t Prove Employees Are Complying

Jamf argues that AI-use policies alone cannot verify employee behavior, and recommends visibility into AI tools, agents and MCP servers, plus controls over platform access and configuration, to govern data-protection risks.

Jul 21, 2026
Security Insights · huntress.com

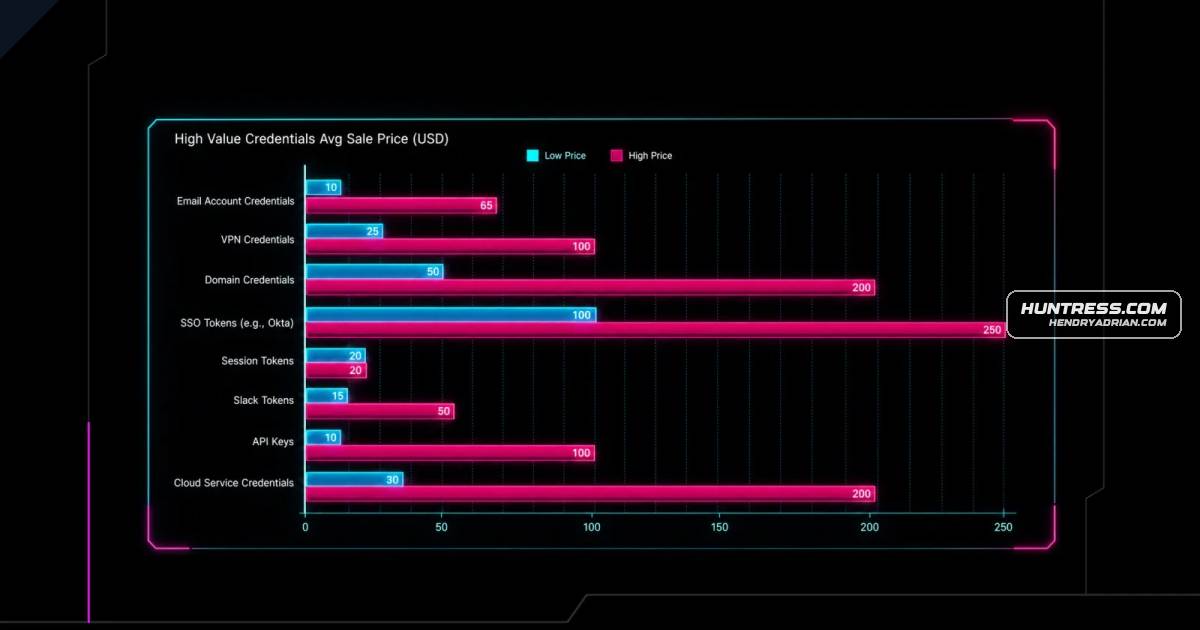
What Initial Access Brokers Do and How They Fuel Cybercrime

Initial access brokers break into organizations, validate and sell access to other attackers, enabling attacks such as ransomware and data theft. The article explains common entry methods and ways businesses can reduce risk.

Jul 21, 2026
Security Insights · trendmicro.com

Why More CVEs Don’t Necessarily Mean More Exploitable Risk

A security-leader briefing argues that rising CVE counts do not equal rising exploitable risk, and recommends prioritizing known exploitation and exploitability signals over raw disclosure volume.

Jul 21, 2026
Security Insights · cyberscoop.com

Why Blocking AI Models Won’t Stop the Cyber Threats They Create

The authors argue that restricting access to cyber-capable AI models is only a temporary measure. They call for stronger government leadership and defense investment, including measuring exposure, testing systems under attack, and improving recovery.

Jul 20, 2026
Security Insights · aikido.dev

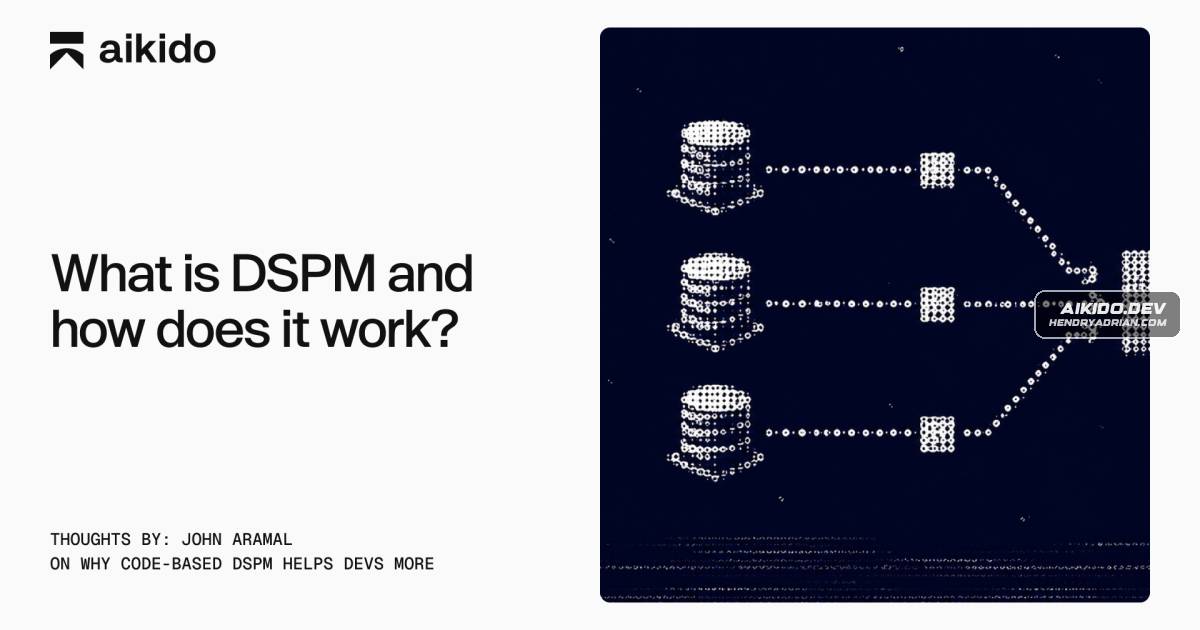
Code-Based DSPM Traces Sensitive Data Exposure to Application Code

The article contrasts storage-scanning DSPM with code-based analysis that traces sensitive data through application code, identifies risks such as PII in logs, and suggests fixes without accessing production data stores.

Jul 20, 2026
Security Insights · malwareinfo.app

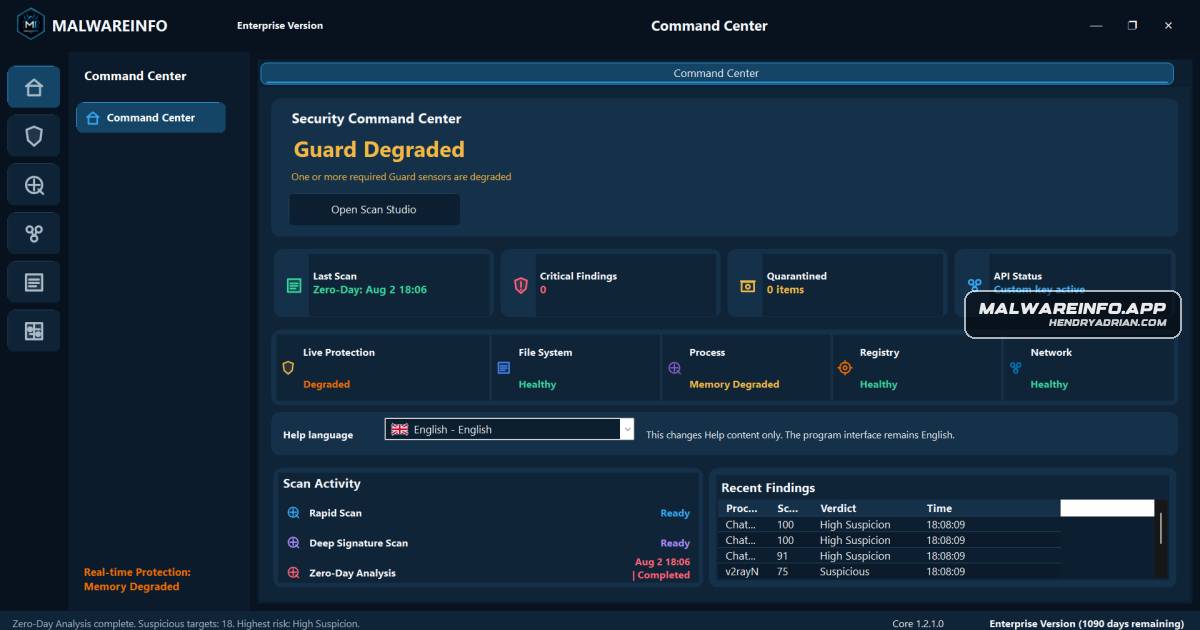
Malware INFO Guide Outlines Safer Malware Investigation Workflows

A Malware INFO guide walks analysts through malware investigation workflows, emphasizing isolated execution, evidence preservation, privacy safeguards and the limits of automated findings.

Jul 18, 2026
Security Insights · huntress.com

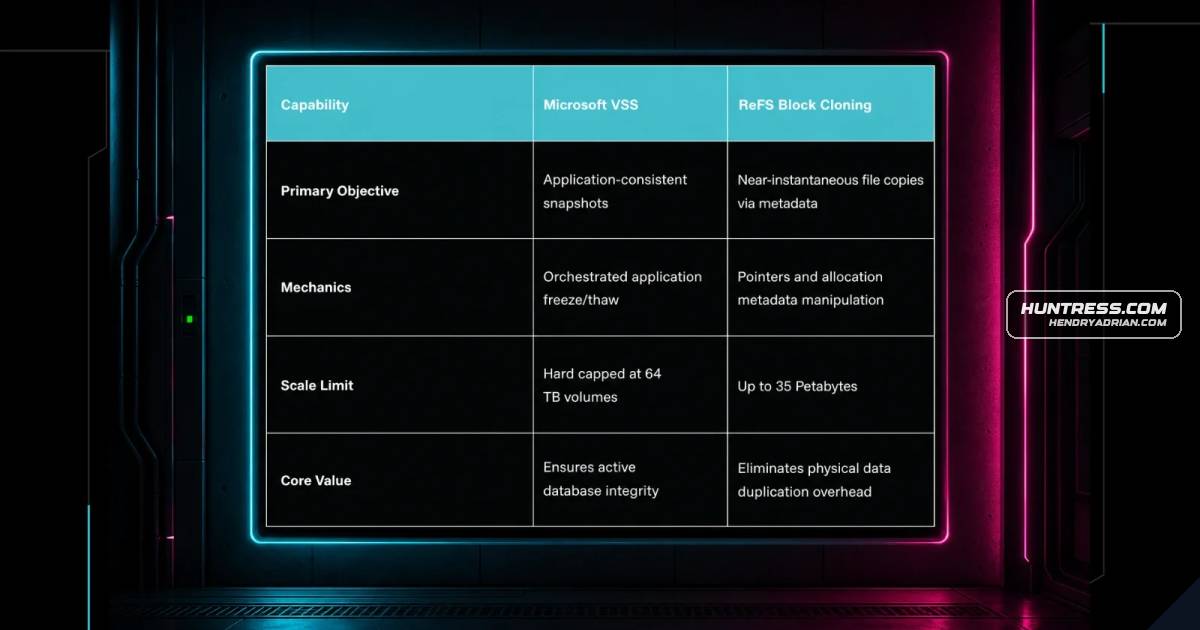
Microsoft VSS: Key Limitations and Best Practices for Data Resilience

An overview of Microsoft VSS explains how it creates application-consistent snapshots, where its 64TB limit and copy-on-write overhead constrain it, and why snapshots alone do not provide ransomware-proof recovery.

Jul 17, 2026
Security Insights · recordedfuture.com

How External Threat Intelligence Can Help Track APT Activity

The article explains how APTs use stealth, custom malware and legitimate tools to evade defenses, and argues that monitoring external threat infrastructure can help defenders identify and disrupt campaigns earlier.

Jul 17, 2026
Security Insights · sysdig.com

Sysdig’s CISO Guide Advocates Headless, API-First Cloud Security

Sysdig promotes API-first “headless” cloud security, saying live telemetry and agent-accessible controls can speed response. It cites rapid intrusions and assesses JADEPUFFER as agentic ransomware, while recommending scoped access, immutable policies, audit trails and ס

Jul 16, 2026
Security Insights · securityweek.com

Why OT Vulnerabilities Have Different Real-World Consequences

Legacy OT systems often lack modern defenses, and denial-of-service flaws can halt equipment or trigger safety failures. The author says patching is often difficult, making network segmentation and coordinated vulnerability disclosure important.

Jul 16, 2026
PreviousPage 23 of 54 Next
© 2026 cyber.hendryadrian.com