Windows Lab Shows Local Privilege Escalation Through Misassigned SeTcbPrivilege
Summary
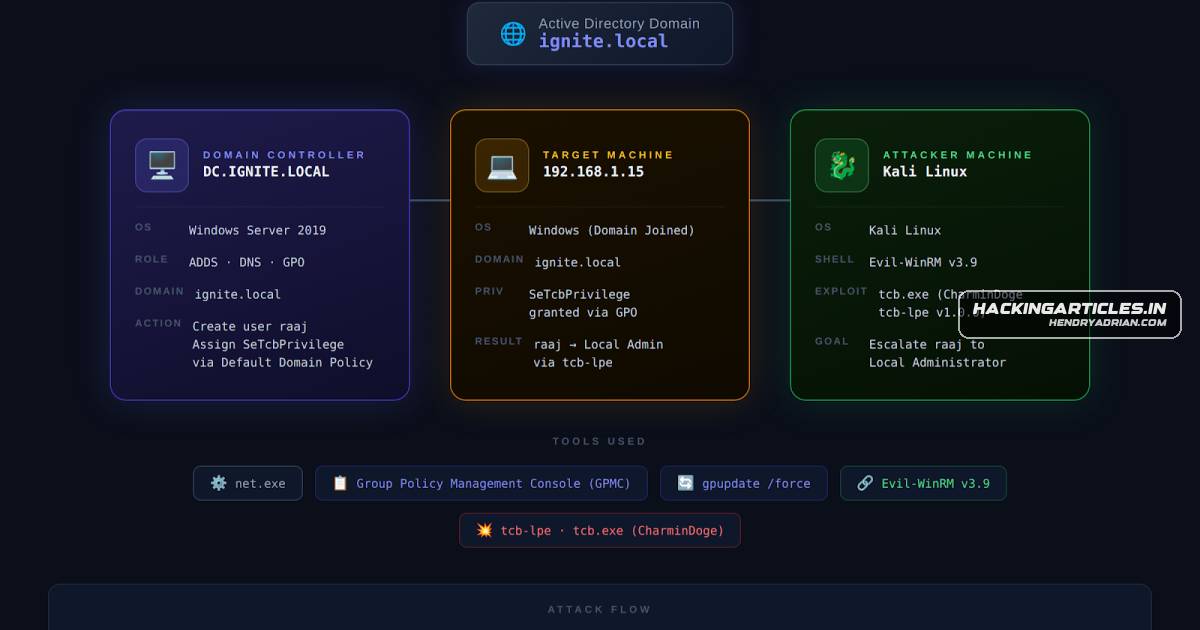
A lab walkthrough demonstrates how a standard domain account granted SeTcbPrivilege through Group Policy can use tcb-lpe to gain local administrator rights, and outlines auditing, monitoring, and least-privilege mitigations.
Key points
- The tutorial assigns SeTcbPrivilege to a standard domain user through the Default Domain Policy in an Active Directory lab.
- The account connects to a Windows host over WinRM and verifies that the privilege is enabled.
- The tcb-lpe tool uses the privilege to run a command as SYSTEM, adding the account to the local Administrators group.
- The article says SeTcbPrivilege is a legitimate Windows right; the risk arises when it is granted to accounts that do not require it.
- Recommended mitigations include auditing Group Policy assignments, restricting the privilege to necessary service accounts, and enforcing least privilege.
- Suggested detection includes correlating sensitive privilege-use and service-installation events; the article also recommends restricting WinRM access and using application control.
Article Details
- Topic
- Windows privilege escalation through misconfigured SeTcbPrivilege assignments and use of the tcb-lpe exploit
People
Products
Evil-WinRMThe attacker operates from a Kali Linux machine, using Evil-WinRM v3.9 to establish a remote shell over WinRM.Group Policy Management ConsoleSupporting tools include net.exe and the Group Policy Management Console (GPMC) on the Domain Controller for user creation and privilege assignment, and tcb-lpe — specifically the precompiled tcb.exe binary authored byMicrosoft WindowsWindows Privilege Escalation: SeTcbPrivilegeWindows Defender Application ControlBlock Unsigned Executables with Windows Defender Application Control
Tools
GPMCSupporting tools include net.exe and the Group Policy Management Console (GPMC) on the Domain Controller for user creation and privilege assignment, and tcb-lpe — specifically the precompiled tcb.exe binary authored bynet.exeSupporting tools include net.exe and the Group Policy Management Console (GPMC) on the Domain Controller for user creation and privilege assignment, and tcb-lpe — specifically the precompiled tcb.exe binary authored bytcb-lpethe Default Domain Policy, verifying the privilege over a WinRM session, and leveraging the open-source tcb-lpe exploit (tcb.exe) to add the compromised account to the local Administrators group — all within a