
GitGuardian Uses MDM to Deploy Honeytokens Across Developer Endpoints
Summary
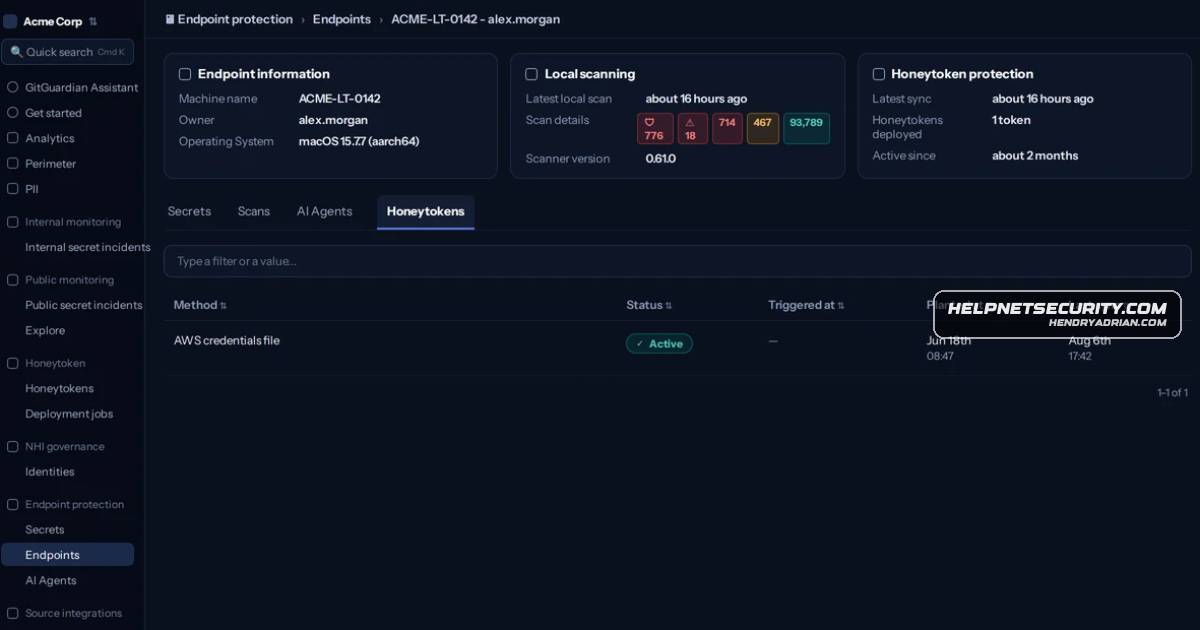
GitGuardian describes using MDM to deploy and replace honeytokens across developer laptops, alerting teams when a decoy credential is used. The article says the current tokens are AWS credentials and notes that deception detects use, not theft.
Key points
- GitGuardian says MDM has supported fleet-wide honeytoken deployment to developer laptops since June 2026, with deleted decoys replaced on the next sync.
- Alerts identify the machine and file associated with a triggered token and can route to existing tools such as email, Slack, Teams, ServiceNow, or webhooks.
- The currently supported honeytokens are AWS credentials issued from an account controlled by GitGuardian; API calls against the key are logged.
- The article describes Shai-Hulud as scanning entire filesystems for secrets and validating found credentials within seconds.
- Honeytokens detect attempted use, not credentials that are stolen but never used; the article presents them as complementary to credential discovery.
- GitGuardian says it is developing coverage for Kubernetes configuration files and package registry logins, and plans to extend placement to CI runners and Kubernetes clusters.
Article Details
- Topic
- GitGuardian’s fleet-wide honeytokens for detecting credential use on developer endpoints