
CVE Surge Shifts Focus to Vulnerability Remediation
Summary
The article argues that rising CVE counts may reflect faster vulnerability discovery, while remediation is the larger bottleneck: NIST’s backlog grew, and Verizon found only 26% of confirmed, actively exploited flaws fully patched in 2025.
Key points
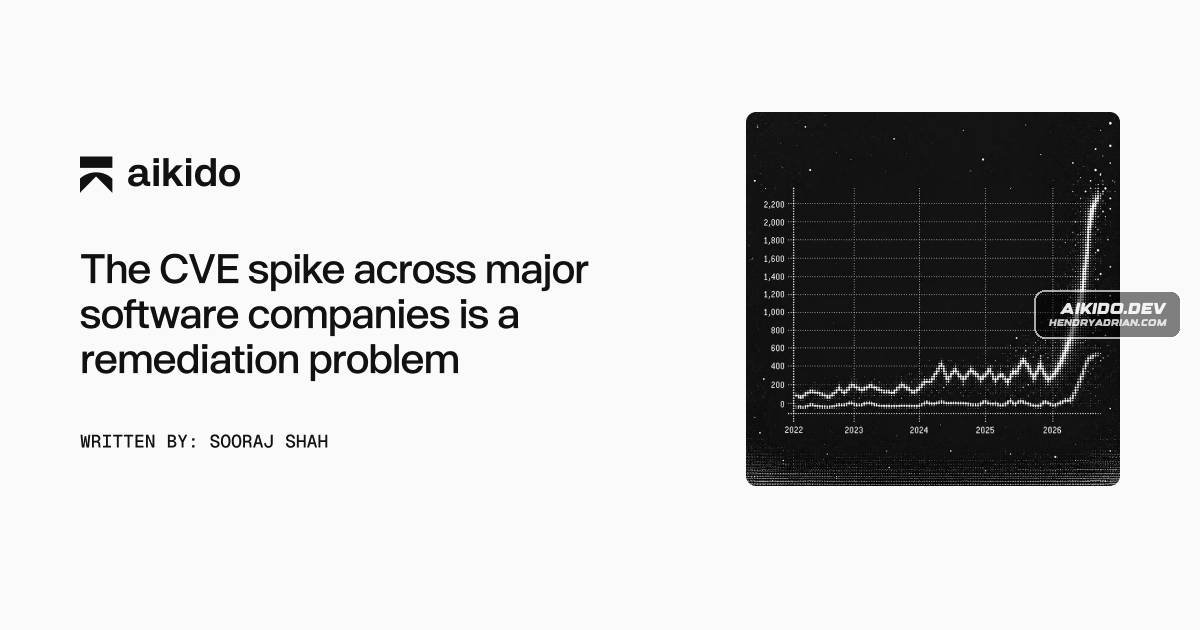
- The article cites an Epoch AI chart shared by a16z showing critical and high CVEs across 21 major software companies rising from under 100 per month to over 600 since spring 2026; it cautions that the increase alone does not establish greater risk.
- It suggests AI-assisted discovery may expose longstanding bugs, while noting that reporting or definition changes could also contribute to the CVE increase.
- A federal audit found NIST’s CVE scoring backlog grew from 13,000 to over 27,000 in 18 months; NIST is prioritizing federal-use, critical-software, and CISA KEV vulnerabilities.
- Verizon’s 2026 DBIR found 26% of confirmed, actively exploited KEV vulnerabilities were fully remediated in 2025, down from 38% the prior year; median time to fully patch rose from 32 to 43 days.
- The article says Aikido Intel flagged an unauthenticated RCE affecting Adobe Commerce and Magento Open Source before Adobe issued a hotfix, and says Aikido shipped a fix more than 24 hours earlier.
- Aikido says 67% of packages in which its Intel service found vulnerabilities during its first year had no public disclosure in major vulnerability databases.
Article Details
- Topic
- The growing volume of vulnerability disclosures and slow remediation, including the reported Stylesmuggler unauthenticated RCE affecting Adobe Commerce and Magento Open Source.
Vendors
AdobeThe data came from Epoch AI and includes counts from Apple, AWS, Microsoft, Google, and Adobe.AikidoAikido Intel flagged it independently, without waiting on Adobe or a CVE number to confirm it was real. It tracked the vulnerability under three separate entities, and Aikido Libraries shipped a working fix for
Products
Adobe CommerceThis month, an unauthenticated RCE vulnerability called Stylesmuggler started hitting Adobe Commerce and Magento Open Source. It didn’t have a CVE attached, nor an advisory from Adobe.Aikido IntelAikido Intel flagged it independently, without waiting on Adobe or a CVE number to confirm it was real. It tracked the vulnerability under three separate entities, and Aikido Libraries shipped a working fix forAikido Librariesa CVE number to confirm it was real. It tracked the vulnerability under three separate entities, and Aikido Libraries shipped a working fix for multiple affected versions. It was shipped as an AutoFix pull requestMagentoThis month, an unauthenticated RCE vulnerability called Stylesmuggler started hitting Adobe Commerce and Magento Open Source. It didn’t have a CVE attached, nor an advisory from Adobe.
Industries
CybersecurityAs AI commoditizes detection and exploitation capabilities, cybersecurity has to reinvent itself around what happens after something's found. That starts with knowing which of the vulnerabilities showing up are actuallySoftwareThe chart shows critical and high CVEs jumping from under 100 a month to over 600 a month since Spring 2026 across 21 major software companies.