
Detecting Linux Privilege Escalation With Wazuh and auditd
Summary
A Wazuh tutorial demonstrates auditd, file integrity monitoring and custom rules to detect Linux privilege escalation techniques, including sudo abuse, ptrace injection, dynamic linker hijacking and cron abuse.
Key points
- The walkthrough uses a Wazuh server and an Ubuntu endpoint to configure detections and simulate privilege escalation activity.
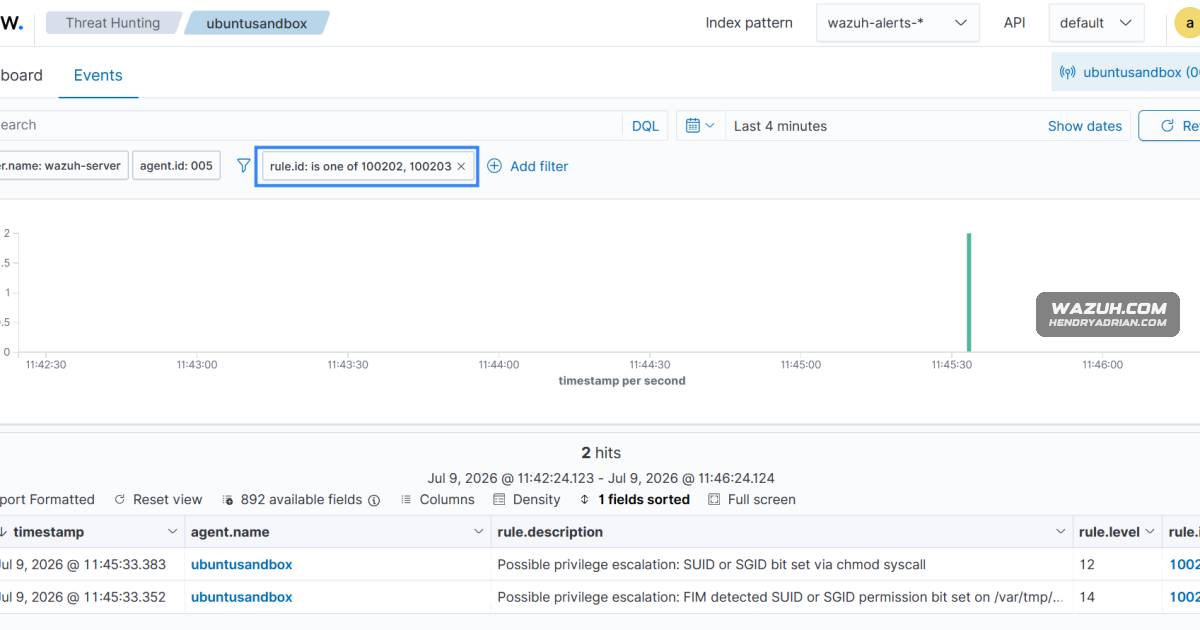
- Auditd tracks sudo execution and permission changes associated with SUID and SGID binaries; custom rules flag sensitive binaries and permission changes.
- File integrity monitoring watches group membership and sudo configuration files, while auditd records user-management commands.
- A ptrace audit rule captures PTRACE_ATTACH requests; the simulation notes that an attempted attachment may fail on a hardened system.
- Auditd and file integrity monitoring track changes to dynamic linker configuration, including /etc/ld.so.preload.
- Cron and logrotate monitoring covers configuration changes and root-privileged execution from writable directories that may indicate PATH hijacking.
- The tutorial maps custom alerts to MITRE ATT&CK and shows how to review them in the Wazuh dashboard.
Article Details
- Defense Focus
- Detect common Linux privilege escalation attempts using audit events, file integrity monitoring, and custom rules.
- Detection Methods
- Alert on sudo execution of binaries that can enable a privileged shell.
- Detect chmod syscalls setting SUID or SGID bits and file permission changes in user-writable directories.
- Monitor usermod and groupmod execution and changes to privileged group and sudo configuration files.
- Detect ptrace attach requests, including non-root requests outside known debugging tools.
- Detect writes and file changes affecting dynamic linker preload configuration.
- Detect cron and logrotate configuration changes and root execution from writable directories.
- Data Sources
- Linux auditd syscall and file-write events from /var/log/audit/audit.log
- File integrity events for permissions and sensitive configuration files
- Rule Types
- Linux auditd rules
- Custom Wazuh XML detection rules with PCRE2 matching
- File integrity monitoring rules
- Platforms
- Linux
- Ubuntu 26.04
- Defensive Actions
- Configure auditd to collect relevant execution, permission-change, ptrace, and file-write events, and forward its log through the endpoint agent.
- Enable real-time integrity monitoring for writable directories and sensitive group, sudo, dynamic linker, and scheduled-task configurations.
- Deploy and reload the custom detection rules, then review privilege escalation and MITRE-mapped events in the dashboard.
- Clean up test accounts, configuration changes, and simulated payloads after validation.
MITRE ATT&CK
T1053.003 · CronThe simulation creates a root cron job that copies bash and sets its SUID bit.T1055 · Process InjectionThe article describes using ptrace to attach to a privileged process and inject code; its test only attempts an attach.T1098.007 · Additional Local or Domain GroupsThe simulation uses usermod to add a test account to the privileged sudo group.T1548.001 · Setuid and SetgidThe simulation sets the SUID bit on a copied bash executable and runs it as a low-privileged user.T1548.003 · Sudo and Sudo CachingThe simulation abuses a NOPASSWD sudoers entry for find to obtain a root shell.T1574.006 · Dynamic Linker HijackingThe simulation writes a benign shared-library path to /etc/ld.so.preload to trigger dynamic linker monitoring.
Vendors
Products
UbuntuIt also shows the auditd, File Integrity Monitoring, and custom rule configurations used to generate alerts for these attacks on Ubuntu endpoints.WazuhThe article demonstrates how Wazuh detects multiple Linux privilege escalation techniques, including sudo abuse, SUID/SGID misuse, group membership changes, ptrace injection, dynamic linker hijacking, and cron abuse.