Analysis Finds Fake Teams MSI Hiding BabaDeda Loader and CNCMachineRMS RAT
Summary
Analysis of a fake Teams MSI found an EV-signed installer that deploys a DLL-side-loading chain through genuine calibre, waits 62 seconds, and unpacks BabaDeda and a CNCMachineRMS RAT. Offline testing did not confirm persistence or C2 activity.
Key points
- The MSI impersonates Microsoft Teams but its metadata identifies an e-book reader; it is signed with an EV certificate issued to Lway Firmware.
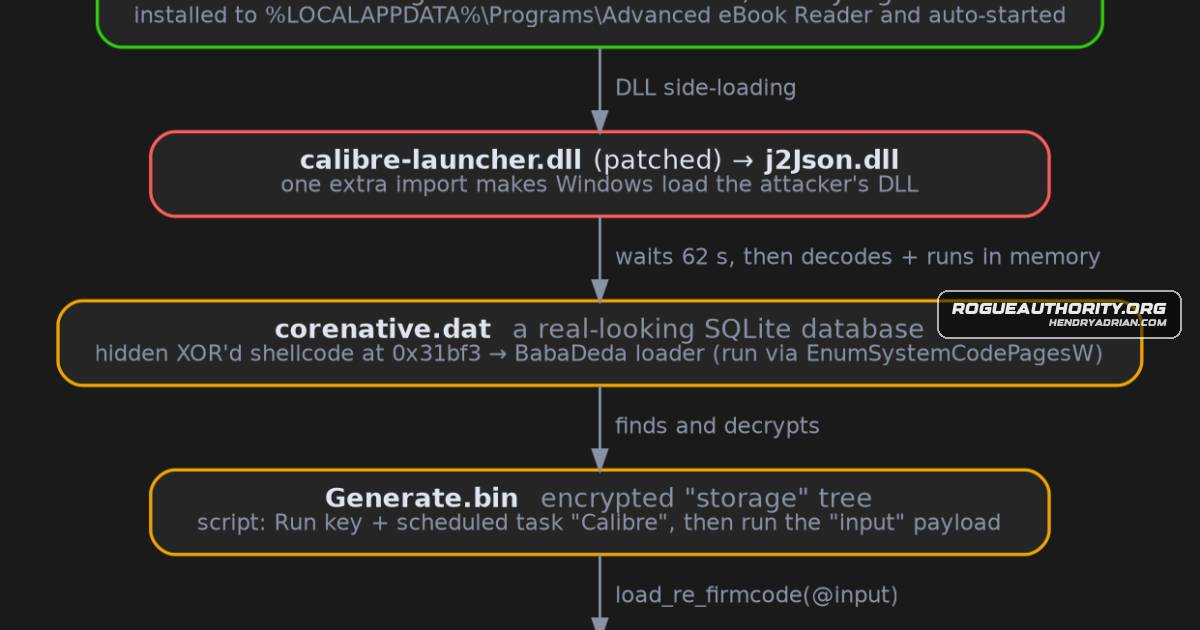
- The package installs genuine calibre alongside a modified, unsigned DLL that loads the first-stage j2Json.dll loader.
- The loader waits 62 seconds, then extracts scrambled code embedded in a SQLite database and executes it in memory.
- The BabaDeda loader locates an encrypted container holding a script configured to create a Calibre Run key and scheduled task, plus the CNCMachineRMS RAT.
- Decoded CNCMachineRMS 1.6.6 strings indicate remote-control, file-management, microphone and camera access, and payload-download capabilities; these capabilities were not observed in operation.
- Offline testing reached stage two, but the process crashed before persistence or network activity; the investigators did not contact the configured servers.
- The article recommends obtaining installers from trusted vendor or company portals and hunting for the named Calibre persistence entries and suspicious files.
Article Details
- Attack Vectors
- A malicious MSI named to resemble a Microsoft Teams installer installs per-user and launches calibre.exe, while its metadata identifies it as an e-book reader.
- The package places an unsigned, modified calibre-launcher.dll beside the genuine signed calibre.exe; loading the launcher causes Windows to load the malicious j2Json.dll.
- The first-stage loader waits 62 seconds, extracts XOR-obfuscated code embedded in corenative.dat, and runs it from memory using EnumSystemCodePagesW as a callback.
- The BabaDeda loader extracts a script and final RAT payload from Generate.bin. The script is configured to create an HKCU Run value and a scheduled task, both named Calibre.
- The CNCMachineRMS RAT is configured to contact wizardexpensive[.]com and 96.62.218[.]59 on port 443. The analysis did not observe live network traffic or confirm these connections.
- Defensive Notes
- Block wizardexpensive[.]com and 96.62.218[.]59, and hunt for connections to these servers.
- Look for an HKCU Run value or scheduled task named Calibre pointing into %LOCALAPPDATA%\Programs\Advanced eBook Reader\.
- Look for an unsigned calibre-launcher.dll beside j2Json.dll outside a normal calibre installation, and for task_payload.bin under a CNCMachineRMS\tasks\ folder.
- Review scheduled tasks created with /SC ONLOGON /RU SYSTEM /RL HIGHEST and Windows Security events 4720 and 4732; the article notes these strings and behaviors are indicators, not observed activity in this test.
- Treat files signed with the Lway Firmware certificate serial 34d898fa7a8ca1ec63fcf8fb76874ad3 as suspect.
- Run installer samples for several minutes during sandbox analysis; this sample's 62-second delay exceeded the 60-second public sandbox run described.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 0efb9058385e057821ee5b6a7282bc6c06b16f4c9ad1d51572325181f8e31a29 | SHA-256 of the patched, malicious calibre-launcher.dll. |
| SHA256 | 3e87cda06f72dc8408483eb497d894de6fbbd47d365ac4d0e763d7a71d9c1125 | SHA-256 of corenative.dat, which contains the obfuscated code used by the loader. |
| SHA256 | 4d7e1145364a12c657973343eb36cad1401fbee385470648b4bbcb8bd4ac4709 | SHA-256 of the decoded BabaDeda loader. |
| SHA256 | 7eae86c5ae86e0074446782aec858b4bc44bbb2f01342f185ecf5f7e20272857 | SHA-256 of PuResources.dll, an attacker-supplied helper DLL in the package. |
| SHA256 | 84190634766ffdd987d8935426b8a65aa409768ab85fd5ed9608f7abda95800c | SHA-256 of Generate.bin, the encrypted container holding the loader script and RAT payload. |
| SHA256 | 96033083a2da941691fb234bf7bf1737df731e5bc26947e4e23ff89ded6f0042 | SHA-256 of SonitusFXSurround.dll, an attacker-supplied helper DLL in the package. |
| SHA256 | a270ce8c4ab1a4edcc474a24c5fb5fac239c48ec961a63df972ec40f0d6fff77 | SHA-256 of j2Json.dll, identified as the first-stage loader. |
| SHA256 | b74b2bfc895f1205dfb389772b201a8e31b7bc4464ff3c4463b417626ecedb1c | SHA-256 of the malicious MSI installer. |
| SHA256 | d9274c98d7be30e6045e63d3acc190055a3849e2992b7382643c16a5aefa22dc | SHA-256 of the decoded CNCMachineRMS RAT. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loader uses rolling XOR to scramble code embedded in corenative.dat, and the RAT's strings and settings are encrypted.T1036.005 · Match Legitimate Resource Name or LocationThe malicious MSI uses a Microsoft Teams-like filename while its metadata identifies it as an e-book reader.T1053.005 · Scheduled TaskThe loader script is configured to create and refresh a scheduled task named Calibre.T1140 · Deobfuscate/Decode Files or InformationThe loader unscrambles the embedded code, and the analysis decoded the RAT's encrypted strings and settings.T1497.001 · System ChecksThe BabaDeda loader checks for virtual-machine vendors and services; the RAT also checks VM-related system characteristics.T1497.003 · Time Based ChecksThe first-stage loader waits 62 seconds before proceeding, a delay the article says is intended to outlast short sandbox runs.T1547.001 · Registry Run Keys / Startup FolderThe loader script is configured to create and periodically rewrite an HKCU Run value named Calibre.T1553.002 · Code SigningThe malicious MSI is signed with an EV certificate issued to Lway Firmware, unrelated to Microsoft or Teams.T1574.002 · DLL Side-LoadingThe package places a malicious j2Json.dll beside the genuine calibre.exe so the trusted program's DLL loading causes the malicious DLL to load.T1620 · Reflective Code LoadingThe loader copies decoded shellcode into executable memory and starts it through EnumSystemCodePagesW.
People
Malware
Products
Tools
ANY.RUNTools used: Malcat, Ghidra, capstone, capa, a sandboxed Wine environment, and ANY.RUN.capaTools used: Malcat, Ghidra, capstone, capa, a sandboxed Wine environment, and ANY.RUN.CapstoneTools used: Malcat, Ghidra, capstone, capa, a sandboxed Wine environment, and ANY.RUN.GhidraTools used: Malcat, Ghidra, capstone, capa, a sandboxed Wine environment, and ANY.RUN.MalcatTools used: Malcat, Ghidra, capstone, capa, a sandboxed Wine environment, and ANY.RUN.