
Signed Fake PeaZip MSI Installs a DLL-Sideloading, Self-Updating Loader
Summary
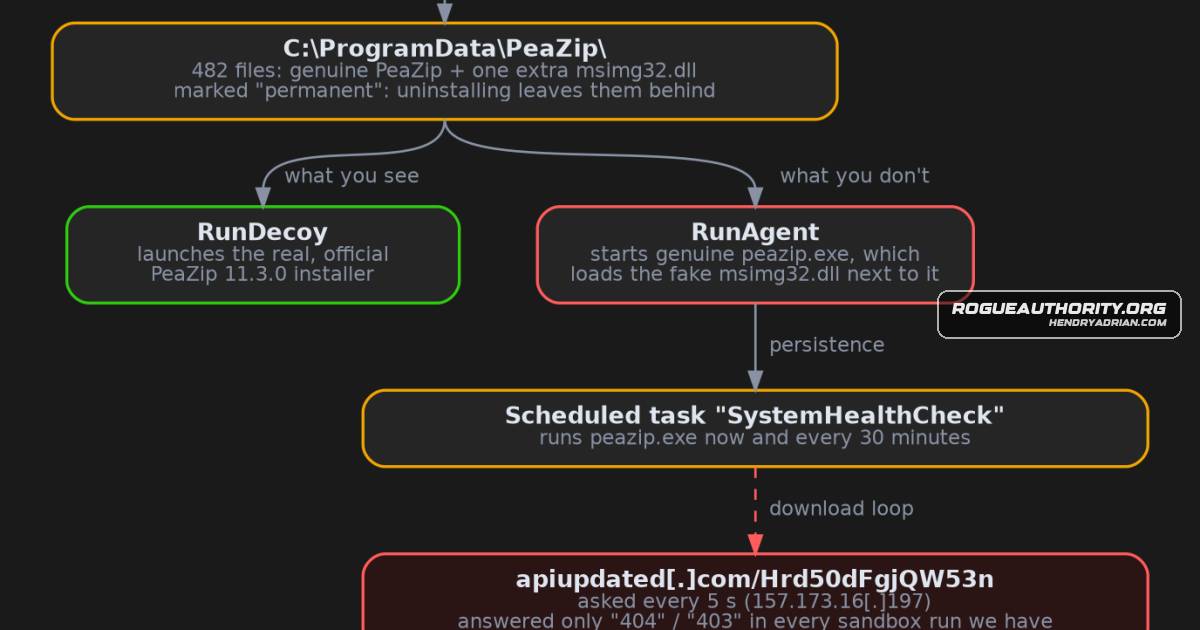
A signed MSI posing as PeaZip 11.4.0 contains the genuine 11.3.0 installer plus a fake msimg32.dll that persists via a scheduled task and polls a server for replacement code. Sandboxes received 404/403 responses; stage two was not observed.
Key points
- The MSI claims to install PeaZip 11.4.0 but bundles the genuine 11.3.0 installer; the article says PeaZip does not publish MSI packages.
- A fake msimg32.dll placed beside the genuine peazip.exe is loaded through DLL sideloading and creates the SystemHealthCheck scheduled task.
- The DLL polls hxxps://apiupdated[.]com/Hrd50dFgjQW53n every five seconds and is designed to replace itself with downloaded content; the next stage was not observed.
- Sandbox runs received 404 responses to the first requests and 403 responses afterward, so it was unclear whether the stage was unstaged or selectively served.
- Most MSI components are marked permanent, so uninstalling the package leaves files behind; the article advises removing the PeaZip folder and task or cleaning/reinstalling the machine.
- Defender guidance includes alerting on msimg32.dll loaded outside System32/SysWOW64 and hunting for the SystemHealthCheck task and the owen_bot_release_peazip_peazip registry key.
Article Details
- Attack Vectors
- A signed MSI posing as a PeaZip 11.4.0 installer runs the genuine PeaZip setup while installing a fake msimg32.dll beside the genuine peazip.exe.
- The fake DLL is loaded through DLL sideloading and creates the SystemHealthCheck scheduled task, which runs peazip.exe every 30 minutes.
- The DLL polls the C2 URL every five seconds and, when it receives an HTTP 200 response, saves the response as thumbs.db, renames it to msimg32.dll, and exits so the replacement can load on the next task run.
- The MSI marks installed components permanent, so uninstalling the package leaves the files and scheduled task behind.
- Defensive Notes
- Download PeaZip only from its official site or GitHub releases; the article says PeaZip does not publish MSI packages.
- If the package was installed, uninstalling is insufficient: remove C:\ProgramData\PeaZip\ and the top-level SystemHealthCheck scheduled task, or clean or reinstall the machine.
- Alert on msimg32.dll loading from locations other than System32 or SysWOW64, especially from C:\ProgramData\.
- Hunt for the \SystemHealthCheck task with action C:\ProgramData\PeaZip\peazip.exe, the registry key HKCU\Software\CustomTest\owen_bot_release_peazip_peazip, and the user agent self_update/1.0.
- Block apiupdated[.]com and 157[.]173[.]16[.]197; flag unsigned msimg32.dll files exporting a function named SelfUpdate.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | apiupdated[.]com | C2 domain serving the fake DLL's update requests. |
| IPV4 | 157[.]173[.]16[.]197 | IP address identified as the C2 server for the fake DLL. |
| SHA256 | 24990cf8916ef624e98cc5461e4e8ac8844fc2cfaca3c49522904a0ad2c0be69 | SHA-256 hash of the fake msimg32.dll installed by the MSI. |
| SHA256 | a8d7e195089b11db3c3c362a4f81b0eb6dc502f204993b73ef37ae0947306a35 | SHA-256 hash of the malicious PeaZip-themed MSI. |
| URL | hxxps[:]//apiupdated[.]com/Hrd50dFgjQW53n | C2 URL polled by the fake DLL for a replacement payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe DLL hides strings with a homemade cipher and resolves Windows functions by hash.T1053.005 · Scheduled TaskThe DLL creates the SystemHealthCheck scheduled task, which runs peazip.exe every 30 minutes.T1071.001 · Web ProtocolsThe DLL polls its C2 URL over HTTPS for a replacement payload.T1105 · Ingress Tool TransferThe DLL downloads a server response and replaces itself with the downloaded file renamed as msimg32.dll.T1204.002 · Malicious FileThe infection begins when a user runs the PeaZip-themed MSI.T1553.002 · Code SigningThe malicious MSI carries a valid code-signing certificate despite being a fake PeaZip installer.T1574.002 · DLL Side-LoadingThe fake msimg32.dll placed beside the genuine peazip.exe is loaded instead of the system DLL.
Vendors
Products
Tools
ANY.RUNTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.Binary RefineryTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.capaTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.CapstoneTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.FLOSSTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.MalcatTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.msitoolsTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.osslsigncodeTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.pefileTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.TriageTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.tsharkTools used: Malcat, msitools, Binary Refinery, osslsigncode, Python (pefile, capstone), FLOSS, capa, a sandboxed Wine setup, tshark, ANY.RUN and Triage.