
Malware Campaign Abuses Exposed SQL Servers to Deploy XMR Miner and Gh0st RAT
Summary
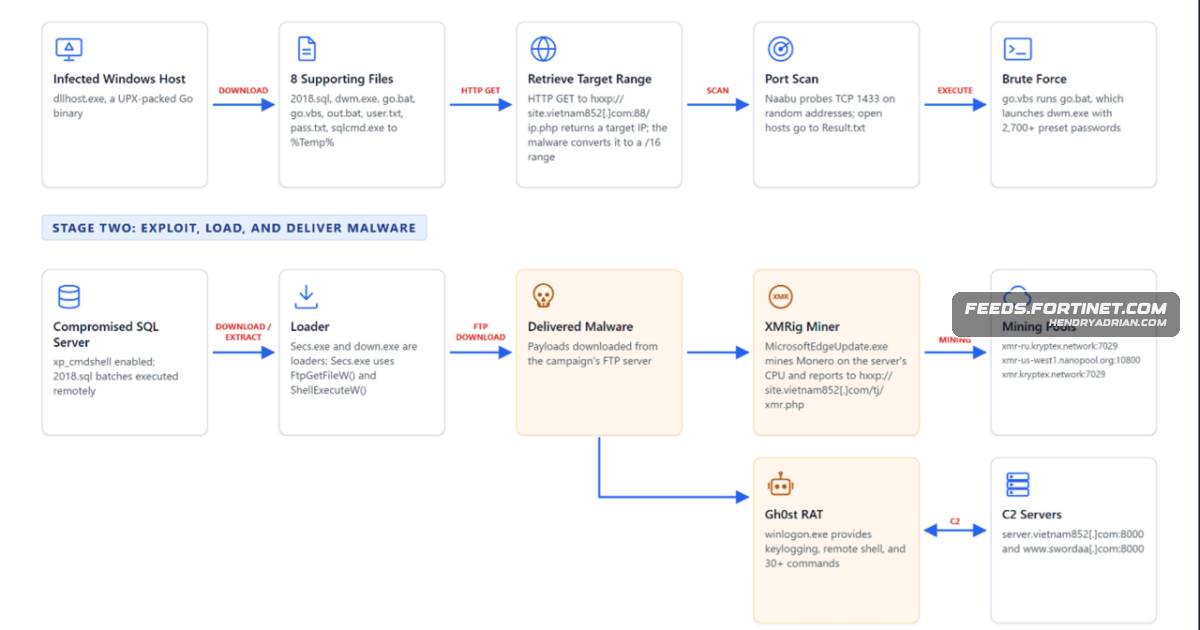
FortiGuard Labs details a campaign that scans for exposed Microsoft SQL Servers, brute-forces logins, and uses T-SQL to deploy a Monero miner and Gh0st RAT, with scheduled tasks for persistence.
Key points
- The malware uses a UPX-packed Go payload embedding Naabu to scan target IP ranges for reachable SQL Servers on TCP port 1433.
- It brute-forces discovered servers using supplied username and password lists, then executes malicious T-SQL commands through the compromised SQL Server.
- The T-SQL enables xp_cmdshell and downloads or extracts a loader, which retrieves and runs additional malware.
- A payload disguised as a Microsoft Edge update mines Monero using the server’s CPU.
- A Gh0st RAT variant supports keylogging, file operations, remote shell access, and other remote-control functions; the analyzed sample also has persistence mechanisms.
- The campaign creates scheduled tasks and uses misleading Microsoft Edge update names to maintain persistence.
- Fortinet lists antivirus, web-filtering, IPS, and port-scan detections for the activity.
Article Details
- Attack Vectors
- The malware scans IP ranges for internet-facing Microsoft SQL Server instances over TCP port 1433, then brute-forces logins using supplied usernames and a list of more than 2,700 predefined passwords.
- After a successful login, the malware uses T-SQL commands to enable xp_cmdshell and download or extract and execute additional malware on the compromised server.
- A loader downloads and executes further payloads, including an XMR miner and a Gh0st RAT variant.
- The malware establishes persistence with scheduled tasks; the RAT also uses a Windows service and a Run key.
- Defensive Notes
- The article recommends enabling tcp_port_scan in the FortiGate DoS policy to detect port scans.
- Fortinet reports that FortiGuard IPS, Web Filtering, and Antivirus services detect or block activity and files associated with the campaign.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ftp[.]vietnam852[.]com | Campaign FTP server used to distribute malware and supporting files. |
| DOMAIN | site[.]hfgjjkrewjk[.]com | Listed campaign domain hosting an XMR miner callback endpoint. |
| DOMAIN | site[.]jiancai008[.]com | Listed campaign domain hosting malware samples. |
| DOMAIN | site[.]vietnam852[.]com | Campaign server used to provide scan ranges, host payloads, and receive miner-related callbacks. |
| DOMAIN | www[.]swordaa[.]com | Hardcoded Gh0st RAT C2 endpoint; the article reports it on port 8000. |
| SHA256 | 124774698fd3ede0800015d19c2bd6c1869d03bbc2e6e8dbe2f69d2978f7f4d0 | SHA-256 of the dwm.exe brute-force and T-SQL execution payload. |
| SHA256 | 125d3a0efe7699bb20397c13f0f4993ad893952727487b4d190e386a5b14c427 | SHA-256 reported for down.exe, google.exe, or payload.exe, campaign payload names. |
| SHA256 | 20983573b840447e1aacd6d3f6dd240732b15037d268d6456f0d3c4ec5051cb0 | Additional SHA-256 reported for down.exe, google.exe, or payload.exe, campaign payload names. |
| SHA256 | 2a0d2889241885d5ea6fe7dd1b1adc83653a0c07b8aaa1b0832e5f9c0225b379 | SHA-256 of the campaign's go.bat file. |
| SHA256 | 2a23e10bfc097e98295cbff8124bd403c4cb677e709b48ccc53d6aca216c3061 | SHA-256 of the MicrosoftEdgeUpdate.exe XMR miner payload. |
| SHA256 | 3f64b0146b323c5716043360e84384a5a197a897f46088df93a910470a29e1a0 | SHA-256 of the winlogon.exe Gh0st RAT payload. |
| SHA256 | 58db0ca2054abe2989412d7a1c8ed16718577f893c196825c848fcd56c7e8f05 | SHA-256 of the embedded executable used as a malware downloader. |
| SHA256 | 79596cf6e267ef5cb658bd97d04e42a41001d36595e370441adb3c2b5dd5666c | SHA-256 of the campaign's go.vbs file. |
| SHA256 | 8ce2cd98ef6ceeece8239936e4aea042c41807f632cd691d5091705bf6c0076d | SHA-256 of the dllhost.exe malware payload. |
| SHA256 | d6e3fd28f479138b336e2c2088ad2e86b7646a163aa453b1703905a4b359070f | SHA-256 of the sqlcmd.exe file downloaded as part of the campaign. |
| SHA256 | da4128aa5d006e05c58f0d240c2d8e5fb02774b6acf314f1230059c7a3498724 | Additional SHA-256 of the MicrosoftEdgeUpdate.exe XMR miner payload. |
| SHA256 | e9d3fd9093c476b8b5de19aa00c50758568649def6491f54fa3e0aba4ea31ac9 | SHA-256 of the campaign's out.bat file. |
| SHA256 | f5444e8e9e9e019693aacb363b7441ac0b8ecfe96a77fd94b9c312a017588eb4 | SHA-256 of 2018.sql, the malicious T-SQL command file. |
| URL | hxxp[:]//ftp[.]vietnam852[.]com:88/test/dllhost.exe | Listed FTP-server URL for a campaign malware payload. |
| URL | hxxp[:]//ftp[.]vietnam852[.]com:88/test/MicrosoftEdgeUpdate.exe | Listed FTP-server URL for the XMR miner payload. |
| URL | hxxp[:]//ftp[.]vietnam852[.]com:88/test/winlogon.exe | Listed FTP-server URL for the Gh0st RAT payload. |
| URL | hxxp[:]//site[.]hfgjjkrewjk[.]com/tj/xmr.php?data= | Listed XMR miner callback endpoint. |
| URL | hxxp[:]//site[.]jiancai008[.]com:88/test/dllhost.exe | Listed URL for the campaign's primary malware payload. |
| URL | hxxp[:]//site[.]jiancai008[.]com:88/test/MicrosoftEdgeUpdate.exe | Listed URL for the campaign's XMR miner payload. |
| URL | hxxp[:]//site[.]jiancai008[.]com:88/test/winlogon.exe | Listed URL for the campaign's Gh0st RAT payload. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/2026/2018.sql | Malicious T-SQL command file downloaded for execution against compromised SQL Servers. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/2026/dwm.exe | URL listed for the executable used to brute-force SQL Server logins and execute T-SQL. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/2026/go.bat | Campaign batch file used to launch the SQL Server brute-force stage. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/2026/go.vbs | Campaign script downloaded to launch supporting attack files. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/down.exe | Malicious executable downloaded and run on compromised SQL Servers. |
| URL | hxxp[:]//site[.]vietnam852[.]com:88/ip.php | Malware URL used to retrieve IP ranges for scanning. |
| URL | hxxp[:]//site[.]vietnam852[.]com/tj/xmr.php?data= | Miner callback endpoint used to report that a compromised host had begun mining. |
MITRE ATT&CK
T1027.002 · Software PackingThe article reports UPX packing for dllhost.exe and Themida packing for the miner and RAT payloads.T1036.005 · Match Legitimate Resource Name or LocationPayloads and scheduled tasks use names such as MicrosoftEdgeUpdate.exe and MicrosoftEdgeUpdateTaskMachineCore to resemble legitimate Microsoft components.T1046 · Network Service DiscoveryNaabu scans target IP ranges for open TCP port 1433 to find reachable Microsoft SQL Servers.T1053.005 · Scheduled TaskThe malware creates scheduled tasks to run payloads repeatedly or daily on compromised servers.T1059.003 · Windows Command Shellgo.bat and other batch commands launch the brute-force payload and schedule tasks.T1059.005 · Visual BasicThe malware runs go.vbs using cscript.exe as an entry point for the downloaded files.T1071.001 · Web ProtocolsThe malware uses HTTP requests to retrieve scan ranges and send host registration and miner-status information.T1071.002 · File Transfer ProtocolsThe downloader retrieves additional executables from the campaign FTP server.T1082 · System Information DiscoveryThe malware collects host details including Windows edition, processor, RAM, installation time, username, and hostname.T1105 · Ingress Tool TransferThe malware downloads scripts, executables, and other supporting files from its campaign servers.T1110.001 · Password Guessingdwm.exe tries usernames and a predefined list of more than 2,700 passwords against discovered SQL Servers.T1496 · Resource HijackingThe XMR miner uses the compromised SQL Server's CPU to mine Monero.T1505.001 · SQL Stored ProceduresThe malware uses T-SQL commands to enable xp_cmdshell and execute commands on compromised SQL Servers.T1543.003 · Windows ServiceThe Gh0st RAT creates a Windows service to run persistently.T1547.001 · Registry Run Keys / Startup FolderThe RAT adds winlogon.exe to the Windows Run key; the campaign also copies Secs.exe to the Startup folder.
Malware
Vendors
Products
FortiClientFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.FortiEDRFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.FortiMailFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.Fortinet FortiGateFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.Microsoft SQL ServerImpacted Users: Microsoft SQL ServerMicrosoft WindowsAffected Platforms: Microsoft Windows
Tools
naabudllhost.exe → ip.php (target IP range for MS SQL Server) → Naabu port scan (TCP Port 1433) → go.vbs / go.bat → dwm.exe brute force → T-SQL execution (2018.sql) → download and run additional malwareUPXThe discovered payload, named dllhost.exe, is packed with UPX (versions 3.9–5.21 detected), as shown in Figure 2.