
BITTER Uses Three Infection Chains to Deploy PapRAT in South Asia
Summary
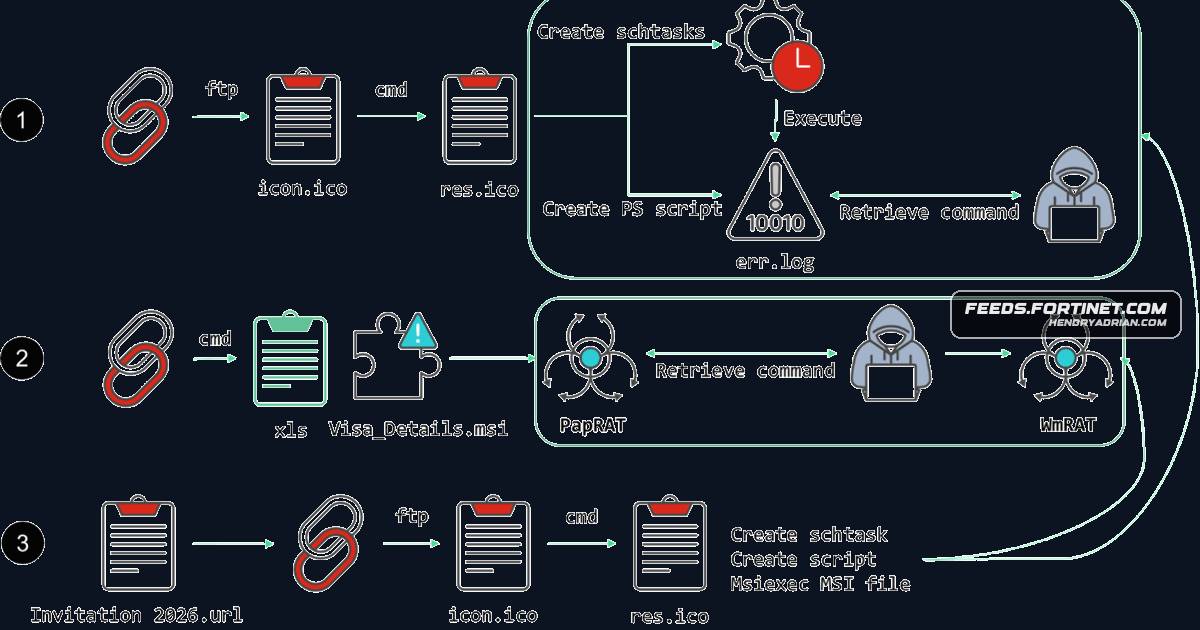
FortiGuard Labs attributes a South Asia-focused campaign to suspected BITTER with high confidence. Three Windows infection chains use LNK, URL and VHDX lures to deploy PapRAT; a Rust variant adds commands and HTTPS C2.
Key points
- FortiGuard Labs reports a campaign targeting South Asian organizations and attributes it to suspected BITTER with high confidence, citing lure filenames, C2 patterns, file metadata and malware analysis.
- The three Windows infection chains use a malicious LNK with ftp.exe, a VHDX image containing an LNK and MSI installer, and a URL shortcut that retrieves an LNK over WebDAV.
- One chain uses ftp.exe to execute local shell commands, create scheduled tasks and run staged scripts; the article says this may evade monitoring focused on PowerShell or wscript.
- PapRAT supports remote command execution, file upload and download, deletion, directory and drive enumeration, and screenshot capture; its C++ version checks in to C2 over plaintext HTTP.
- In one chain, PapRAT downloads WmRAT as a secondary payload. The article describes WmRAT as capable of gathering system information, taking screenshots, listing files and directories, and executing C2 commands.
- A Rust PapRAT variant uses HTTPS C2 and expands the command set from eight to eleven, adding PowerShell execution, sleep/resume polling and a clean-exit command.
- Fortinet recommends caution with unexpected LNK files, URL shortcuts, disk images and MSI packages, and monitoring suspicious execution chains and outbound C2 traffic; it also reports existing FortiGuard detections.
Article Details
- Attack Vectors
- A malicious LNK uses ftp.exe to execute a local script, which creates scheduled tasks and communicates with remote infrastructure.
- A VHDX lure contains an LNK that silently launches an MSI installer while opening a decoy spreadsheet; the installer deploys PapRAT.
- A URL shortcut retrieves files over WebDAV, leading to an LNK and MSI installation of PapRAT.
- PapRAT can execute commands, transfer and delete files, enumerate directories and drives, capture screenshots, and deliver WmRAT. Its Rust variant also supports PowerShell execution.
- Defensive Notes
- Treat unsolicited LNK files, URL shortcuts, disk images, and MSI packages with caution.
- Monitor suspicious scripting, scheduled-task creation, installer activity, and outbound C2 traffic, including activity involving native Windows utilities.
- Fortinet reports that FortiGuard Web Filtering rates associated campaign URLs as malicious and that its Antivirus service detects associated files.
- FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard Antivirus service.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | chestergreenfarming[.]com | Decoded PapRAT C2 domain used in the third infection chain. |
| DOMAIN | gomescareerplans[.]com | Campaign server contacted by the script to retrieve err.log. |
| DOMAIN | goodnfortunes[.]com | Campaign server used for C2 communication and receiving reconnaissance data. |
| DOMAIN | rivingtonclarks[.]com | PapRAT C2 domain; the Rust variant's decoded C2 URL is hosted on this domain. |
| DOMAIN | techtalkhelp[.]com | Server hosting talk.log, which contains a script that fetches additional commands. |
| HOSTNAME | netmansrvdns[.]com | WmRAT C2 host identified in the article. |
| HOSTNAME | rappellingaart[.]com | Campaign WebDAV host used to provide files, including an MSI installer. |
| SHA256 | 411c0b9a2f98b927d806a685faf0c1ab1005647b4816157008892347fb88546b | SHA-256 hash listed for WmRAT. |
| SHA256 | 569a21b519aaac8c92f653d708ab6ef34e3f38ea967f47e041d1e2425f6a4b33 | SHA-256 hash listed for PapRAT. |
| SHA256 | a3081df333ca7f18bd90d10a45125ab5011dcf9d2806feae2935f09cab07da4c | SHA-256 hash listed for a campaign LNK file. |
| SHA256 | ccefbdec2718d864d9d33c743aabfcef88a8d7904d1c598bfcf15cf5f3591c88 | SHA-256 hash listed for a campaign LNK file. |
| SHA256 | e3992f8c945b0761242377cba32d91b0a390c7cecd79478439843d93e6d2b76b | SHA-256 hash listed for a campaign LNK file. |
| URL | hxxp[:]//gomescareerplans[.]com/docs | Campaign URL used by a script to contact a remote server for err.log. |
| URL | hxxp[:]//www[.]rivingtonclarks[.]com/beautiQuewonders/banaNa.php | Campaign URL listed among indicators associated with the PapRAT activity. |
| URL | hxxps[:]//felixfuturenext[.]com/Epistemological/ | Campaign URL listed by Fortinet as associated with the malicious activity. |
| URL | hxxps[:]//goodnfortunes[.]com/ucl.php | Campaign endpoint used to receive reconnaissance data. |
| URL | hxxps[:]//techtalkhelp[.]com/talk.log | Campaign URL used to retrieve the script containing commands that fetch additional instructions. |
MITRE ATT&CK
T1005 · Data from Local SystemThe campaign gathers local directory, task, antivirus, and mounted-drive information and places it in a file for transfer.T1027 · Obfuscated Files or InformationThe campaign uses Base64-encoded script content and obfuscated C2 configuration, including XOR encoding and reversed ROT-3-shifted strings.T1036.005 · Match Legitimate Resource Name or LocationPapRAT masquerades as bruzsvc.exe and uses Microsoft Corporation attribution and the product name Microsoft redistributables in its version resource.T1041 · Exfiltration Over C2 ChannelThe campaign sends reconnaissance output to its C2, and PapRAT uploads files and screenshots through HTTP requests.T1053.005 · Scheduled TaskThe scripts create scheduled tasks that periodically execute commands and maintain contact with campaign infrastructure.T1057 · Process DiscoveryThe reconnaissance script runs tasklist and saves the process list in its collected output.T1059.001 · PowerShellPapRAT's Rust variant adds PowerShell command execution, and the reconnaissance script queries antivirus products using PowerShell.T1059.003 · Windows Command ShellThe LNK chain uses cmd.exe to execute local commands and scripts; PapRAT also runs remote-shell commands through cmd /c.T1071.001 · Web ProtocolsPapRAT communicates with its C2 over HTTP or HTTPS, polling for commands and exchanging data.T1083 · File and Directory DiscoveryThe campaign enumerates directories, including Desktop, Documents, and Downloads; PapRAT also supports directory listing.T1105 · Ingress Tool TransferThe campaign retrieves scripts and MSI files from remote servers and PapRAT downloads WmRAT through its DWW command.T1113 · Screen CapturePapRAT and WmRAT can capture screenshots and return them to C2.T1218.007 · MsiexecLNK files launch MSI installers, including a chain that invokes msiexec to install Imp_Details.msi.T1518.001 · Security Software DiscoveryThe reconnaissance script queries Windows Security Center for installed antivirus product data.
Threat Actors
Malware
Vendors
Products
FortiClientFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.FortiEDRFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.FortiMailFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.Fortinet FortiGateFortinet FortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service, and each solution includes the FortiGuard AntiVirus engine.Microsoft WindowsAffected Platforms: Microsoft Windows
Industries
EnergyBITTER is a suspected South Asian cyberespionage group active since at least 2013, with a history of targeting the government, energy, and engineering sectors.EngineeringBITTER is a suspected South Asian cyberespionage group active since at least 2013, with a history of targeting the government, energy, and engineering sectors.GovernmentBITTER is a suspected South Asian cyberespionage group active since at least 2013, with a history of targeting the government, energy, and engineering sectors.