
FortiGuard Analyzes Flutter-Based Android Gambling Malware TinstaPorn
Summary
FortiGuard researchers analyzed Android/TinstaPorn.A!tr, a Flutter-based gambling app that sends device, phone-number and geolocation data to its operators. The report maps its server infrastructure and API flows, and describes AES/HMAC-protected game traffic.
Key points
- The researchers identify TinstaPorn as an Android Flutter app posing as an online casino; the platform promotes gambling through VIP recharges, rebates, and referrals.
- The app contacts configuration, registration, line-configuration, and game servers, with hard-coded fallback servers when configured servers are unavailable.
- It sends device information and geolocation to its operators; phone numbers are submitted through phone-binding or profile endpoints.
- Game-server requests use AES encryption and HMAC-SHA256 signing. The AES key is returned in cleartext by line-configuration servers, which the researchers say makes the encryption primarily obfuscation and error checking.
- The analysis describes how the app selects a fast game server and uses APIs for authentication, gameplay, payments, withdrawals, and user data.
- FortiGuard says its antivirus detects the malware as Android/TinstaPorn.A!tr and that its web-filtering service blocks the servers.
Article Details
- Attack Vectors
- An Android app posing as an online clone of a casino in Macau draws users into an illegal gambling platform with games whose odds are rigged in the operators’ favor.
- The malware uses hard-coded configuration URLs to obtain registration servers, then obtains line-configuration and game-server details.
- The app sends device information, geolocation, and phone numbers to its servers; the article also describes gambling-related financial loss and addiction exploitation.
- Defensive Notes
- Fortinet reports that FortiGuard Antivirus detects and blocks Android/TinstaPorn.A!tr and that FortiGuard Web Filtering blocks the servers.
- The article says FortiGate, FortiMail, FortiClient, and FortiEDR include FortiGuard Antivirus protection, and advises that protections be kept up to date.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | d9020e64482821585245bf29fc96a046395b33d8e1830e17eeb949a2eb16a4d0 | Hash listed in the article’s Files section for the analyzed malware. |
| URL | hxxps[:]//api[.]cloudfareproxy2618[.]xyz | Listed as a server URL associated with the malware. |
| URL | hxxps[:]//api[.]testylhg24[.]online | Listed as a server URL associated with the malware. |
| URL | hxxps[:]//gitee[.]com/lspxgit/nocode/raw/master/address[.]txt | Malware bootstrap configuration URL; the article reports that it was taken down. |
| URL | hxxps[:]//gitee[.]com/lspxgit/yongli/raw/main/helpline[.]txt | Attacker-used line-configuration resource from which the malware obtains game-server information. |
| URL | hxxps[:]//github[.]com/googleaidog/nocode/blob/master/address[.]txt | Backup bootstrap configuration URL used by the malware; the article says it hosted an old configuration. |
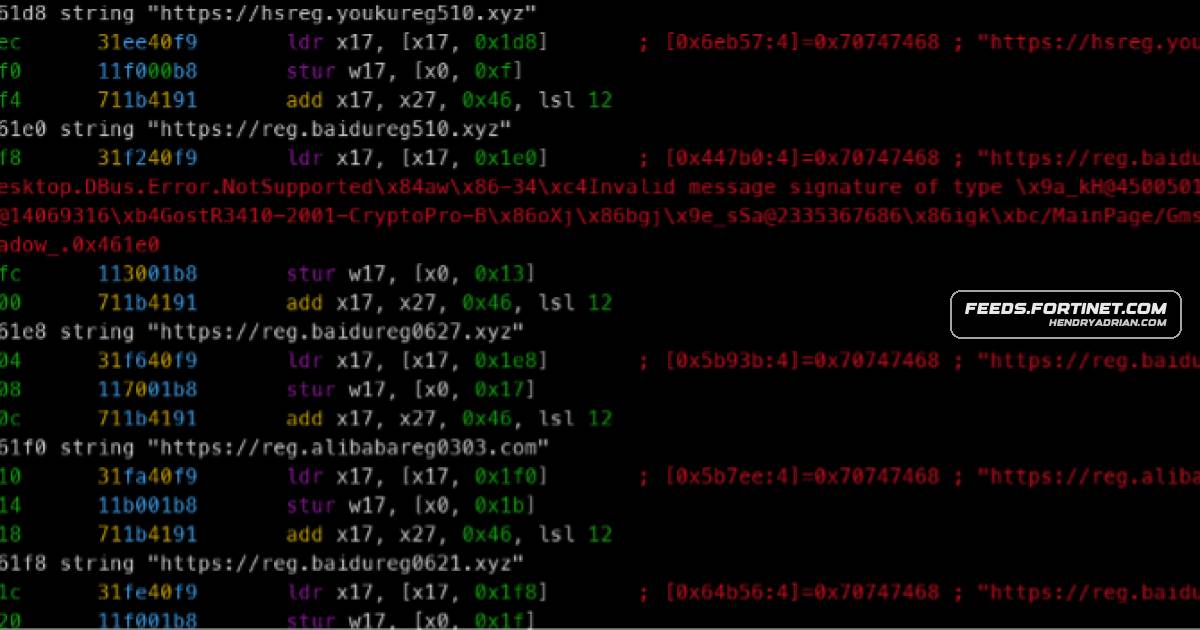
| URL | hxxps[:]//hsreg[.]youkureg510[.]xyz | Listed as a registration server used by the malware. |
| URL | hxxps[:]//line[.]yongli250627linecfg[.]xyz | Listed as malware infrastructure for line configuration or game-server communications. |
| URL | hxxps[:]//raw[.]githubusercontent[.]com/kaerkaerkaerzzz/yongli/main/helpline[.]txt | Backup line-configuration resource used by the malware to obtain game-server information. |
| URL | hxxps[:]//reg[.]alibabareg0303[.]com | Listed as a registration server used by the malware. |
| URL | hxxps[:]//reg[.]baidureg0621[.]xyz | Listed as a registration server used by the malware. |
| URL | hxxps[:]//reg[.]baidureg0627[.]xyz | Listed as a registration server; the article’s telemetry table gives it as an example of a contacted registration domain. |
| URL | hxxps[:]//reg[.]gitshreg611[.]xyz/device/register | Registration-server endpoint returned in the malware’s configuration. |
| URL | hxxps[:]//reg[.]gptreg0706[.]xyz | Listed as a registration server used by the malware. |
| URL | hxxps[:]//up[.]logupload0628[.]xyz/app/log/raw/report | Malware log-server endpoint used to report victim and device telemetry. |
| URL | hxxps[:]//www[.]game250522linecfg[.]xyz | Listed as malware infrastructure for line configuration or game-server communications. |
| URL | hxxps[:]//www[.]tt250627linecfg[.]xyz | Listed as malware infrastructure for line configuration or game-server communications. |
| URL | hxxps[:]//www[.]ylhg250627linecfg[.]xyz | Listed as malware infrastructure; the article identifies this domain as an example of the fastest game server. |
| URL | hxxps[:]//zc[.]nationbj[.]com/device/register | Registration-server endpoint returned in the malware’s configuration. |
MITRE ATT&CK
Malware
Vendors
Products
AndroidAffected Platforms: AndroidFlutterFlutter is an open-source UI framework developed by Google that uses using the Dart programming language to build Android, iOS, web, and desktop applications from a single codebase.FortiClientFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.FortiEDRFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.FortiGuard AntivirusThe malware described in this report is detected and blocked by FortiGuard Antivirus as:FortiGuard IP Reputation and Anti-Botnet Security ServiceThe FortiGuard IP Reputation and Anti-Botnet Security Service proactively blocks infrastructure associated with this campaign by correlating malicious IP intelligence collected from Fortinet’s global sensor network,FortiGuard Web Filtering ServiceThe FortiGuard Web Filtering Service blocks the servers.FortiMailFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.Fortinet FortiGateFortiGate, FortiMail, FortiClient, and FortiEDR support the FortiGuard AntiVirus service.
Tools
BlutterIn 2024, the best available tools were Blutter and JEB.Bytecode StudioFortunately, this has improved in 2026, and we now have better solutions: r2flutter, Bytecode Studio, and AI support within the disassembler (r2ai).JEBIn 2024, the best available tools were Blutter and JEB.r2aiFortunately, this has improved in 2026, and we now have better solutions: r2flutter, Bytecode Studio, and AI support within the disassembler (r2ai).r2flutterFortunately, this has improved in 2026, and we now have better solutions: r2flutter, Bytecode Studio, and AI support within the disassembler (r2ai).