GitLab CI/CD Integer Overflow Enables Command Execution; Fixed Versions Released
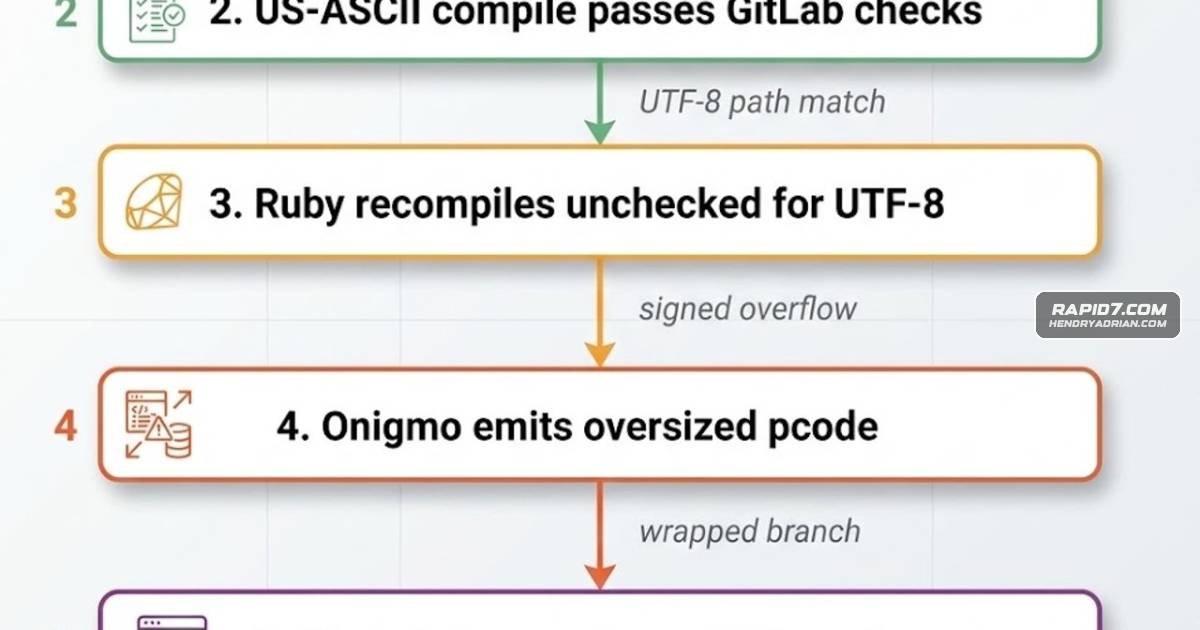
Rapid7 demonstrated command execution as GitLab’s git account via CVE-2026-97229. The exploit requires a malicious configuration and path in a public project; GitLab patched affected releases, and no in-the-wild exploitation was reported at disclosure.