GitLab CI/CD Integer Overflow Enables Command Execution; Fixed Versions Released
Summary
Rapid7 demonstrated command execution as GitLab’s git account via CVE-2026-97229. The exploit requires a malicious configuration and path in a public project; GitLab patched affected releases, and no in-the-wild exploitation was reported at disclosure.
Key points
- CVE-2026-97229 is an integer overflow in GitLab CI/CD regular-expression handling. GitLab assigned it a CVSS score of 10.0 and described possible unauthenticated code execution.
- Rapid7’s PoC ran arbitrary commands as the git operating-system account on GitLab CE 19.4.1 for Linux amd64.
- The demonstrated trigger is an unauthenticated CI lint request, but an attacker must first have write access to create the malicious configuration and specially named path in a public project.
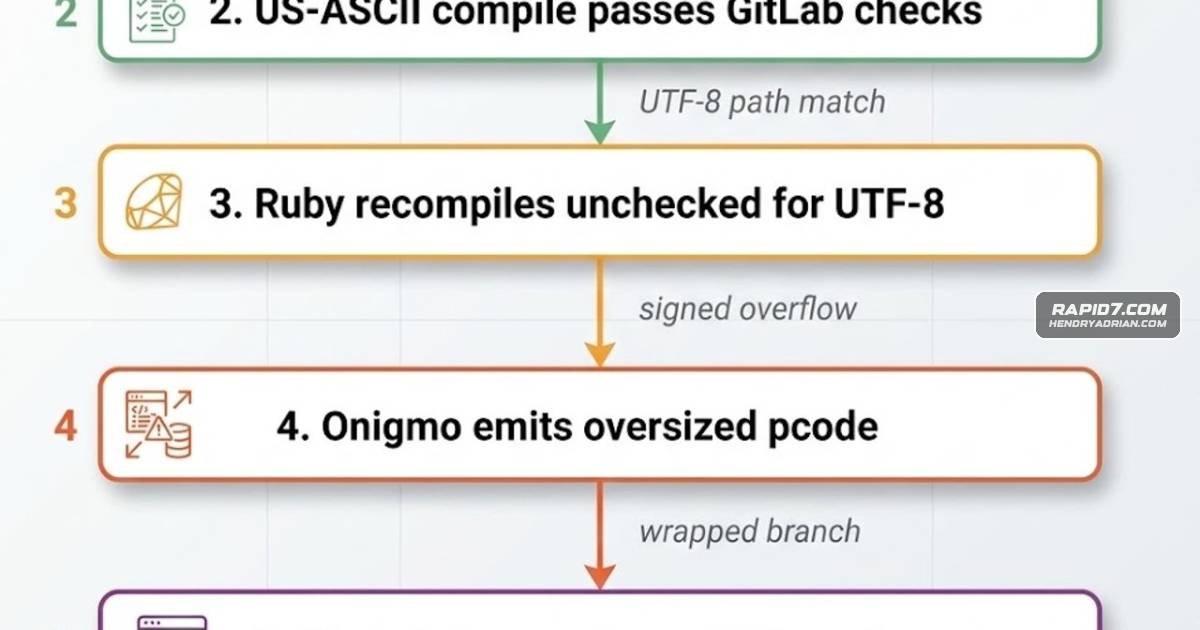
- The exploit uses a repeat-bound scanner bypass and UTF-8 regex recompilation to trigger oversized Onigmo bytecode, then redirects execution to a system() call.
- GitLab reports that GitLab.com was patched before disclosure; Dedicated customers do not need to act. The release notes did not report exploitation in the wild at disclosure.
- Self-managed customers should upgrade to 19.2.8, 19.3.5, or 19.4.2. Temporary measures include restricting credential-free access to attacker-writable public projects or blocking the lint route.
Article Details
- Vulnerability Types
- Integer overflow in Onigmo regular-expression compilation
- Severity
- CVSS 10.0 (assigned by GitLab)
- Affected Versions
- GitLab CE and EE 19.2 before 19.2.8
- GitLab CE and EE 19.3 before 19.3.5
- GitLab CE and EE 19.4 before 19.4.2
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Restrict credential-free access to attacker-writable public projects.
- Block the CI lint route.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe PoC executes an attacker-selected command through system() on the GitLab host, demonstrated with uname -a and id.T1190 · Exploit Public-Facing ApplicationThe exploit triggers the flaw through GitLab's unauthenticated CI lint API request against a public project.