Rapid7 Discloses Critical Unauthenticated SQL Injection in WebAlliance eCommerce
Summary
Rapid7 disclosed CVE-2026-108065, an unauthenticated SQL injection in Channel Software WebAlliance eCommerce. It may expose database information and, with elevated database privileges, enable server commands; Rapid7 advises blocking /preapproval.asmx.
Key points
- The flaw is in the sUserID parameter of the GetUser method in SOAP requests to /preapproval.asmx; a single quote can escape the SQL query.
- The affected database is Microsoft SQL Server, which supports stacked queries.
- Exploitation may expose sensitive database information, including personal information and passwords.
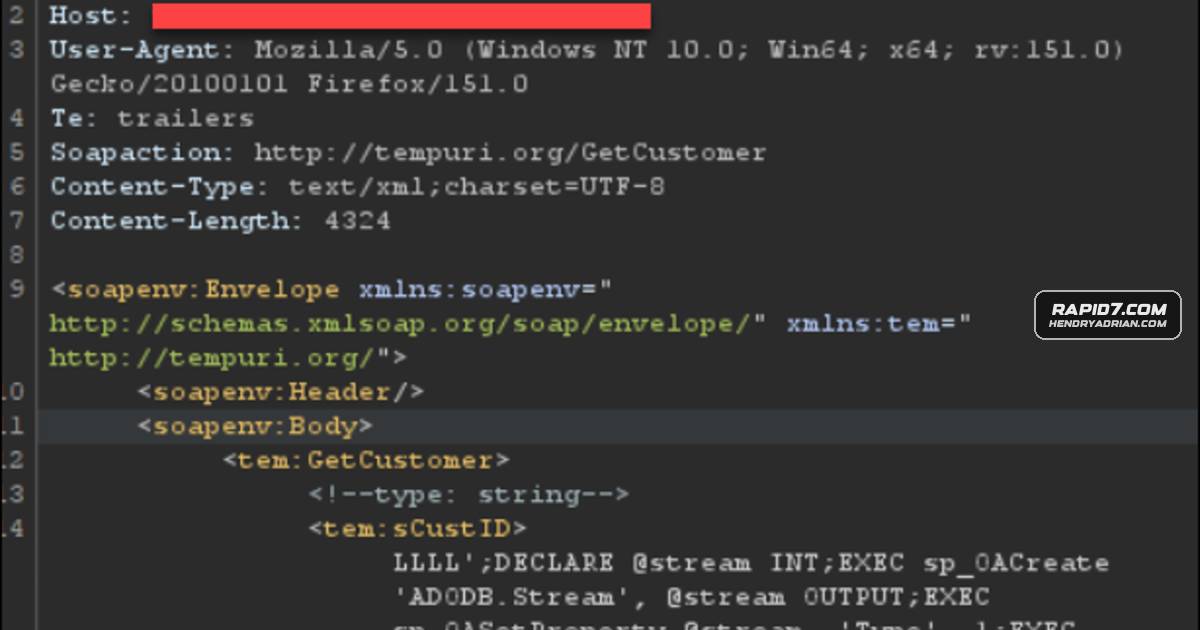
- If the database account has high privileges, the flaw may allow system commands on the database server; Rapid7 describes file upload and command execution scenarios.
- Rapid7 reports discovering and exploiting the issue during black-box testing; it says it could not perform root-cause analysis.
- Rapid7 rates the vulnerability CVSS 9.8 Critical and recommends blocking access to /preapproval.asmx.
- Rapid7 says it contacted Channel Software and received no response before public disclosure on October 14, 2026.
Article Details
- Vulnerability Types
- SQL injection
- Severity
- Critical (CVSSv3.1 9.8)
- Exploitation Status
- reported
- Exploit Availability
- public_poc
- Patch Status
- unknown
- Workarounds
- Block access to /preapproval.asmx.
MITRE ATT&CK
T1190 · Exploit Public-Facing ApplicationThe unauthenticated SQL injection is exploitable through the WebAlliance eCommerce application's /preapproval.asmx endpoint.T1213 · Data from Information RepositoriesThe vulnerability can be used to extract sensitive database information, including user PII and passwords.T1505.003 · Web ShellThe article describes uploading an ASPX file through SQL Ole Automation and browsing to it to run code and system commands, if the database user has sysadmin privileges and the database shares the web application's server.
CVE
People
Vendors
Products
Microsoft SQL ServerThe SQL query can be escaped by inserting a single quote in the parameter. The database is running Microsoft SQL Server which allows for stacked queries. The query can be escaped with ( ‘; ) to inject completely newWebAlliance eCommerceRapid7 discovered CVE-2026-108065, an SQL Injection vulnerability (CWE-89) in Channel Software WebAlliance eCommerce.The exploit allows a malicious actor to read sensitive data from the database, or, if the database