cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1546 articles

Vulnerability & Exploit · malwarebytes.com

Researcher Bypasses Meta Smart Glasses’ Code-Signing Safeguard

Researcher Paula (pamoutaf) found that tampering with a settings file could disable app-signature verification on Ray-Ban Meta glasses, allowing her code to run. Her research did not demonstrate access to camera footage or recordings.

Nov 10, 2026
Vulnerability & Exploit · securityweek.com

SAP Patches Critical ICM2SHELL and ProxyGate Vulnerabilities

SAP released security notes addressing nine critical vulnerabilities. Onapsis says ICM2SHELL enables unauthenticated command execution and that its research lab provided SAP a working exploit; ProxyGate may also enable unauthenticated RCE.

Nov 10, 2026
Vulnerability & Exploit · rapid7.com

N-able Releases N-central Hotfix for Critical Vulnerabilities After PoC Scanning

Rapid7 reports that N-able's N-central faced 33 publicly disclosed issues, including unauthenticated RCE. N-able reported scanning tied to the public PoC but no evidence of successful customer exploitation. Hotfix 2 fixes seven CVEs; hosted systems were upgraded.

Nov 10, 2026
Vulnerability & Exploit · socprime.com

Google Patches Exploited Chrome XML Use-After-Free Zero-Day

Google confirmed CVE-2026-125350, a high-severity Chrome XML use-after-free, is exploited in the wild and released fixed versions. The exploit’s delivery, targets, and achieved impact remain undisclosed.

Nov 10, 2026
Vulnerability & Exploit · socradar.io

Microsoft Mitigates CVSS 10 Entra Device Registration Flaw

CVE-2026-109469 is an authorization-bypass flaw in Entra Device Registration that could allow unauthenticated remote privilege escalation. Microsoft says it has mitigated the issue; no customer patch is needed, and no exploitation has been reported.

Nov 10, 2026
Vulnerability & Exploit · malwarebytes.com

Google Patches Actively Exploited Chrome Zero-Day CVE-2026-125350

Google’s Chrome update for desktop and Android includes a fix for CVE-2026-125350, a high-severity use-after-free flaw in the XML component that Google says is exploited in the wild. Attackers, targets, and delivery method are unknown.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

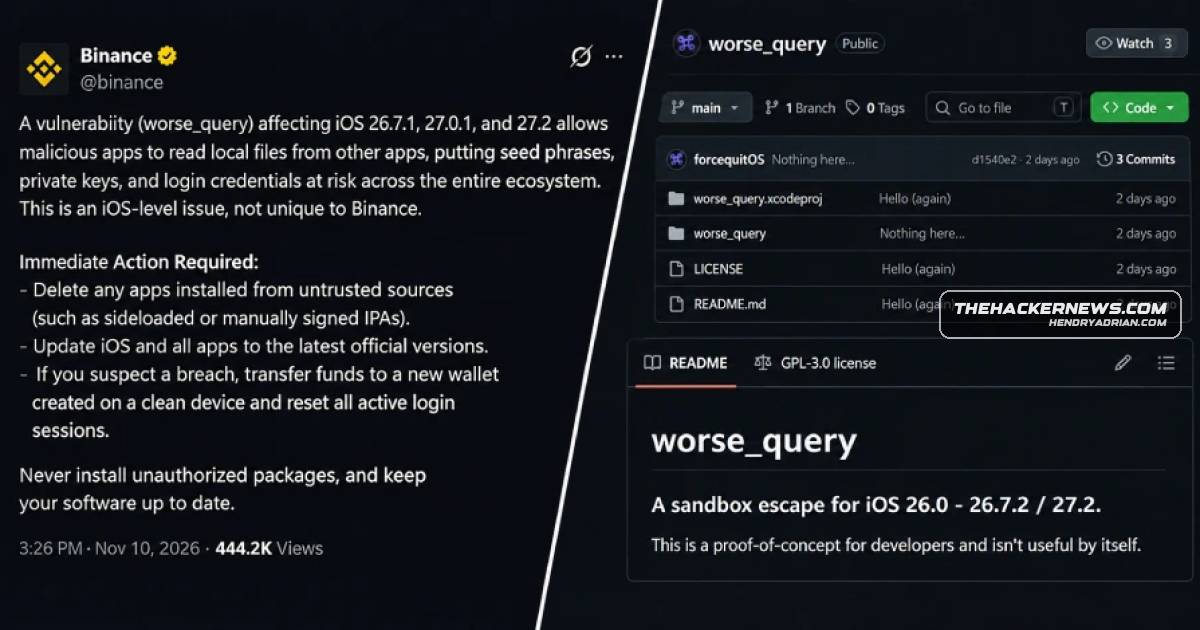
Binance Warns iOS Sandbox Escape Could Expose App Data and Crypto Wallet Keys; No Fix Confirmed

A GitHub proof of concept called worse_query reportedly lets apps with an App Group access other apps’ data on iOS 26 and 27, potentially exposing wallet keys and credentials. No related attacks or thefts were reported, and no fix is confirmed.

Nov 10, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Six Actively Exploited Vulnerabilities to KEV Catalog

CISA added six CVEs to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation. It urges organizations to prioritize remediation and describes updated risk-based requirements for federal agencies.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

Apple Updates Fix iMessage Group-Chat and Bluetooth Pairing Flaws

Apple updates fix two iMessage group-chat flaws, a Brotli decoder out-of-bounds write, and Bluetooth/AirPlay issues. CISA added the Brotli flaw to its Known Exploited Vulnerabilities catalog; Apple did not say whether the flaws were exploited.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

SAP Fixes Four Maximum-Severity Flaws, Including Two That Could Enable Remote Code Execution

SAP fixed four CVSS 10.0 flaws in NetWeaver and Web Dispatcher that reportedly require no login or user action. Two could enable remote code execution; others could allow privileged SAML logins or unauthorized SAP Gateway actions.

Nov 10, 2026
Vulnerability & Exploit · securityweek.com

N-able Takes N-central Offline After Researcher Discloses 30-Plus Alleged Zero-Days

N-able took hosted N-central offline after researcher Sean Bales disclosed more than 30 alleged zero-days. The company said it had no evidence of exploitation and expected a hotfix around midday November 10.

Nov 10, 2026
Vulnerability & Exploit · securityweek.com

CISA Warns of Exploitation of IBM Aspera Faspex and FreeSWITCH Flaws

CISA added IBM Aspera Faspex and SignalWire FreeSWITCH flaws to its KEV catalog after exploitation was reported. The article describes their impacts and patches; details of attacks were not public.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

Google Patches Actively Exploited Chrome XML Use-After-Free Flaw

Google released Chrome updates for nine vulnerabilities, including CVE-2026-125350, an XML use-after-free flaw it says is being exploited in the wild. The company disclosed no attack details or threat actor.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

N-able Takes Hosted N-central Offline After Able2Shell Vulnerability Disclosure

After researcher Sean Bales disclosed Able2Shell flaws with PoC exploits, N-able took Hosted N-central offline and urged on-premises customers to shut down servers. N-able reported no observed active exploitation; watchTowr reported attempts against honeypots.

Nov 10, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Four Product Flaws to KEV Catalog, Citing Active Exploitation

CISA added flaws affecting GPUStack, FreeSWITCH, OpenSSH and IBM Aspera Faspex to its KEV catalog, citing active exploitation. Reports detail activity against the OpenSSH flaw; exploitation details for the other flaws remain unavailable.

Nov 10, 2026
Vulnerability & Exploit · securityweek.com

Google Patches Exploited Chrome XML Zero-Day in Update Fixing Nine Flaws

Google’s Chrome 157 updates fix nine vulnerabilities, including the high-severity CVE-2026-125350 XML use-after-free, which was exploited in the wild. Google has not shared attack details.

Nov 10, 2026
Vulnerability & Exploit · kudelskisecurity.com

Researcher Discloses 33 Alleged N-central Zero-Days in “Able2Shell”

Researcher Sean Bales disclosed 33 alleged N-central zero-days as “Able2Shell,” with four chains reportedly enabling privileged code execution. N-able took hosted services offline and urged on-premises customers to shut down pending a hotfix.

Nov 10, 2026
Vulnerability & Exploit · crowdstrike.com

Microsoft's November 2026 Patch Tuesday Fixes 1,252 Vulnerabilities, Including Exploited Outlook Zero-Day

Microsoft's November 2026 updates address 1,252 vulnerabilities, including an exploited Outlook spoofing flaw that can expose NTLMv2 hashes. The roundup details critical RCE and privilege-escalation flaws across Office, Windows services, LDAP, AD DS, Exchange and Hyper‑

Nov 10, 2026
Vulnerability & Exploit · databreachtoday.com

Worse Query iOS Sandbox Escape Can Expose App Data, Including Crypto Wallets

The Worse Query flaw reportedly lets malicious iOS apps access other apps’ private data. A public proof of concept demonstrates the technique; it requires an App Group container. Apple’s iOS 27.2.1 update did not mention the flaw.

Nov 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Binance Warns iOS Flaw Could Expose Crypto Wallet Secrets

Binance warns that the iOS “worse_query” flaw could let apps access other apps’ files, including wallet secrets. A public tool demonstrates the technique; Apple released updates, but it is unclear whether they fix this issue.

Nov 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Actively Exploited Xen Orchestra Flaw Enables Admin Access and Host Takeover

Vates says attackers are exploiting a Xen Orchestra authentication bypass that can grant admin privileges and enable XCP-ng host takeover. Fixed releases are available; Vates warns detection requires HTTP monitoring.

Nov 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Google Patches Chrome Zero-Day CVE-2026-125350, Eighth Exploited This Year

Google says attackers are exploiting a high-severity use-after-free flaw in Chrome's XML component. Patches are rolling out for Stable Desktop on Windows, macOS, and Linux; Google has not disclosed incident details.

Nov 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

Barracuda Says Attackers Are Exploiting Two Email Security Gateway Flaws

Barracuda says attackers are exploiting two patched flaws affecting its products, including the Email Security Gateway. Successful exploitation requires access to the Admin UI; the company reports activity at a small number of organizations.

Nov 10, 2026
Vulnerability & Exploit · privacyaffairs.com

Researcher Details iOS Microphone Permission Bypass Fixed by Apple

Researcher Mustafa Calap found an iOS app could alter an audiomxd identity token to record audio after microphone permission was denied, without the orange indicator. Apple patched CVE-2026-65339, but its notes do not clarify whether iOS/iPadOS 27 includes the fix.

Nov 9, 2026
PreviousPage 7 of 65 Next
© 2026 cyber.hendryadrian.com