
Binance Warns iOS Sandbox Escape Could Expose App Data and Crypto Wallet Keys; No Fix Confirmed
Summary
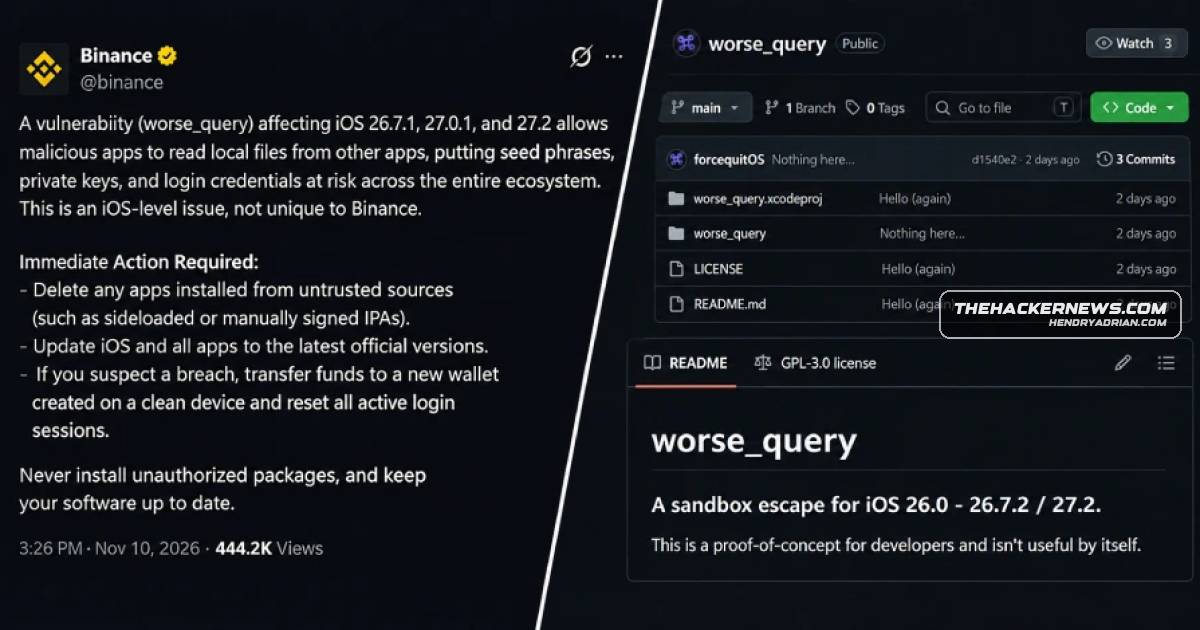
A GitHub proof of concept called worse_query reportedly lets apps with an App Group access other apps’ data on iOS 26 and 27, potentially exposing wallet keys and credentials. No related attacks or thefts were reported, and no fix is confirmed.
Key points
- The worse_query proof of concept can access other apps’ data containers; on iOS 27, it can also reach some system folders.
- An app must set up an App Group container to use the escape.
- WQ Files, a file manager built on worse_query, can reportedly edit, delete, and clear other apps’ data without a jailbreak or kernel exploit.
- WQ Files can be installed through sideloading tools including AltStore and SideStore.
- The article reports no known attacks or thefts involving the escape and names no specific wallet app as exposed.
- Apple’s iOS 27.2.1 and iOS 26.7.3 security notes do not mention worse_query or a sandbox fix; no fix has been confirmed.
- Binance advised removing apps from untrusted sources and updating iOS and apps; users who suspect a breach were advised to move funds to a new wallet on a clean device and reset active sessions.
Article Details
- Vulnerability Types
- iOS sandbox escape
- Cross-app data access
- Affected Versions
- iOS 26
- iOS 27
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- unavailable
- Workarounds
- Delete apps installed from untrusted sources, including sideloaded or manually signed apps.
- Update iOS and all apps.
- If a breach is suspected, move funds to a new wallet created on a clean device and reset all active login sessions.
People
0xjohnnyCollaborated with forcequit on the worse_query sandbox-escape release.Christoph KolbiczDeveloper of WQ Files, an app built on worse_query that can access and modify other apps' data.forcequitResearcher who released the worse_query sandbox-escape proof of concept in collaboration with 0xjohnny.
Vendors
Products
iOSAn iOS sandbox escape published on GitHub lets an app read other apps' files on iPhones running iOS 26 and 27. That puts seed phrases, private keys, and login credentials at risk of exposure to malicious apps, BinanceWQ FilesOne of them is WQ Files, a file manager that developer Christoph Kolbicz built on worse_query. It reaches other apps' data without a jailbreak or a kernel exploit, and it can edit, delete and clear that data.