
N-able Takes Hosted N-central Offline After Able2Shell Vulnerability Disclosure
Summary
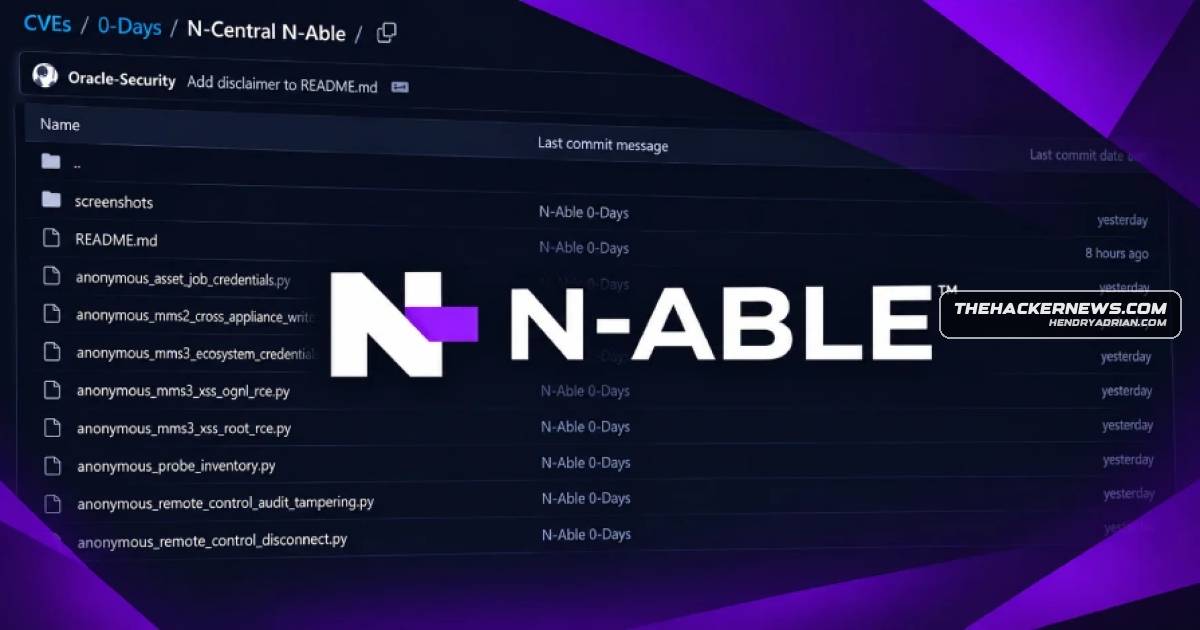
After researcher Sean Bales disclosed Able2Shell flaws with PoC exploits, N-able took Hosted N-central offline and urged on-premises customers to shut down servers. N-able reported no observed active exploitation; watchTowr reported attempts against honeypots.
Key points
- Sean Bales disclosed more than 30 vulnerabilities, collectively called Able2Shell, and PoC exploits tested against N-able N-central Appliance 2026.4.0.31.
- The reported flaws include credential disclosure, arbitrary file writes, directory traversal, XSS, XXE injection, and remote code execution.
- Successful exploitation could enable rogue administrative access to the N-central management interface and command execution as root.
- N-able took Hosted N-central offline, said associated services may be unavailable, and urged on-premises customers to shut down servers until further notice.
- N-able said it had not observed signs of active exploitation and was working on a hot fix.
- watchTowr reported observing exploitation attempts against its N-able N-central honeypots; this does not establish successful compromise of customer systems.
- watchTowr urged users to audit for signs of compromise, restrict access, and follow vendor mitigation guidance.
Article Details
- Vulnerability Types
- Credential disclosure
- Arbitrary file writes
- Directory traversal
- Cross-site scripting (XSS)
- XML external entity (XXE) injection
- Remote code execution (RCE)
- Affected Versions
- N-central Appliance 2026.4.0.31
- Exploitation Status
- reported
- Exploit Availability
- public_poc
- Patch Status
- unavailable
- Workarounds
- Shut down on-premises servers until further notice.
- Restrict access.