cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1546 articles

Vulnerability & Exploit · securityweek.com

Plex2Shell Vulnerabilities Exploited Against QNAP NAS Users

QNAP reports exploitation of Plex2Shell, a four-flaw chain in Plex Media Server that can enable unauthenticated code execution. QNAP says some users’ servers appear compromised, reports no data loss, and advises updating and checking exposed devices.

Nov 9, 2026
Vulnerability & Exploit · securityweek.com

SSHole OpenSSH Authentication Bypass Exploited in the Wild

Threat actors are reportedly exploiting SSHole (CVE-2026-123158), an OpenSSH authentication bypass affecting certain musl-based systems with PAM disabled. OpenSSH 10.6p2 patches the flaw; disabling password authentication is a mitigation.

Nov 9, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Four Actively Exploited Vulnerabilities to KEV Catalog

CISA added four vulnerabilities affecting GPUStack, SignalWire FreeSwitch, OpenBSD OpenSSH and IBM Aspera Faspex to its KEV Catalog based on evidence of active exploitation. Federal agencies must prioritize remediation under BOD 26-04.

Nov 9, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds SonicWall SonicOS MFA Bypass Flaw to KEV Catalog Amid Potential Exploitation Reports

CISA added SonicWall SonicOS flaw CVE-2026-19868 to its KEV catalog. SonicWall says valid credentials for an alternate authentication method may bypass SAML and enforced MFA; it investigated a potential exploitation report and urged customers to update.

Nov 9, 2026
Vulnerability & Exploit · fieldeffect.com

N-able Takes N-central Offline After Disclosure of Alleged Vulnerabilities

After Oracle-Security disclosed 33 alleged N-central vulnerabilities with PoC code, N-able took hosted environments offline and advised on-premises customers to do likewise. N-able said it had observed no active exploitation and was preparing a hotfix.

Nov 9, 2026
Vulnerability & Exploit · huntress.com

N-able Takes N-central Cloud Services Offline After Able2Shell Disclosure

After disclosure of 33 critical N-central vulnerabilities, N-able took hosted services offline. The flaws can enable remote code execution or root privilege escalation; N-able reported no active exploitation and said a hotfix was in development.

Nov 9, 2026
Vulnerability & Exploit · darkreading.com

Claude Document-Processing Flaw Could Run Attacker Code on Linux

AIR Security reports that Claude’s Office Party flaw can load an attacker-controlled library during document processing on some Linux systems, potentially executing code with the AI agent user’s privileges. Anthropic has not fixed it.

Nov 9, 2026
Vulnerability & Exploit · darkreading.com

Microsoft Patches Windows Paint RCE Vulnerability After Fix Timeline Confusion

Microsoft patched CVE-2026-83844, a high-severity Windows Paint out-of-bounds read that can enable local code execution. The fixed version is 11.2609.401.0; Microsoft reported no exploitation to date.

Nov 9, 2026
Vulnerability & Exploit · bleepingcomputer.com

N-able Takes N-central Offline After Researcher Discloses 30+ Alleged Zero-Days

N-able took hosted N-central environments offline and advised on-premises customers to do the same after Sean Bales published 30+ alleged vulnerabilities and proof-of-concept exploits. N-able is developing a hotfix and reports no active exploitation.

Nov 9, 2026
Vulnerability & Exploit · databreachtoday.com

SonicWall Patches Actively Exploited SAML and MFA Bypass Flaw

CVE-2026-19868 lets users with valid alternate-method credentials bypass SAML and SAML-enforced MFA on affected SonicWall firewalls. CISA lists it as exploited; SonicWall is investigating reports and has released fixes and a workaround.

Nov 9, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit SSHole OpenSSH Flaw in Linux Systems

Multiple firms report active exploitation of OpenSSH flaw CVE-2026-123158 on certain musl-based Linux systems. Attackers can bypass authentication under specific conditions; OpenSSH 10.6p2 fixes the flaw.

Nov 9, 2026
Vulnerability & Exploit · isc.sans.edu

SANS Honeypots Record Rising SSHole Exploit Attempts

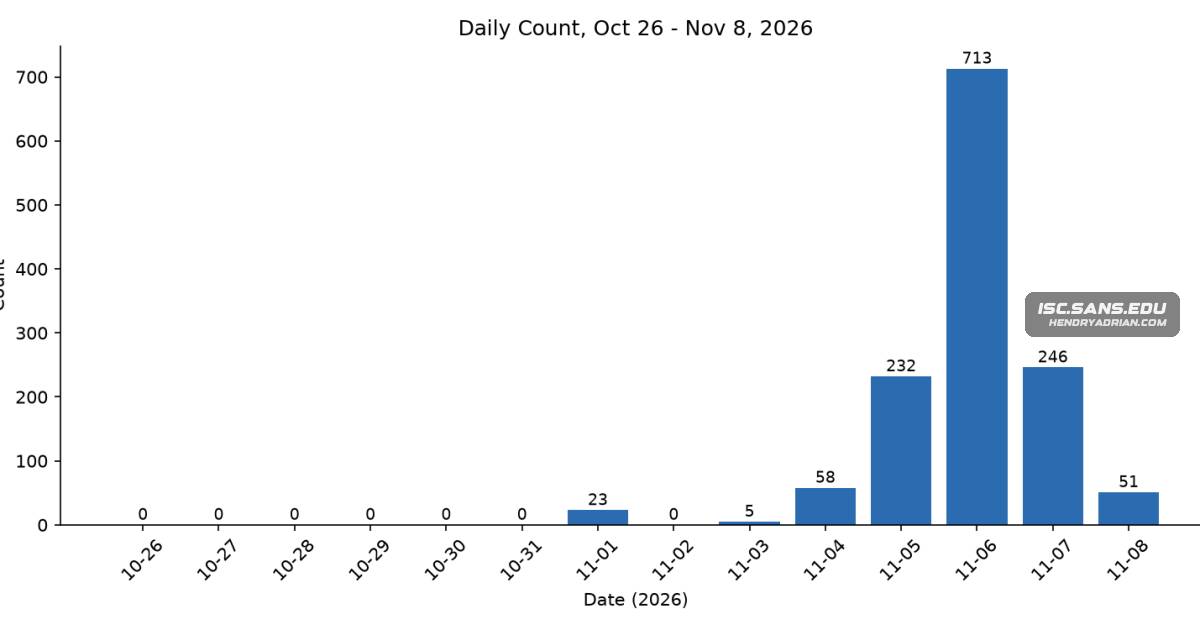
SANS Cowrie honeypots recorded rising SSHole-related activity, with the first identified exploit attempt on Nov. 5 and 713 requests on Nov. 6. The data captures only the first 255 characters of SSH passwords.

Nov 8, 2026
Vulnerability & Exploit · securityweek.com

SonicWall Patches SonicOS Flaw That Can Bypass SAML and MFA

CVE-2026-19868 can let users with valid alternate-method credentials bypass SAML and enforced MFA on affected SonicOS SSL VPNs. SonicWall investigated a report of potential exploitation; CISA added the flaw to its KEV catalog.

Nov 7, 2026
Vulnerability & Exploit · thehackernews.com

WordPress Fix Can Leave a Brief Exploitation Window During Installation

CVE-2026-119977 can leave some WordPress sites exposed while the fix installs, because the updater initially uses old code. Researchers recommend blocking web access to wp-content/upgrade; successful exploitation is not established.

Nov 6, 2026
Vulnerability & Exploit · thehackernews.com

SSHole OpenSSH Flaw Exploited Within Hours; Alpine Honeypot Saw Root Access

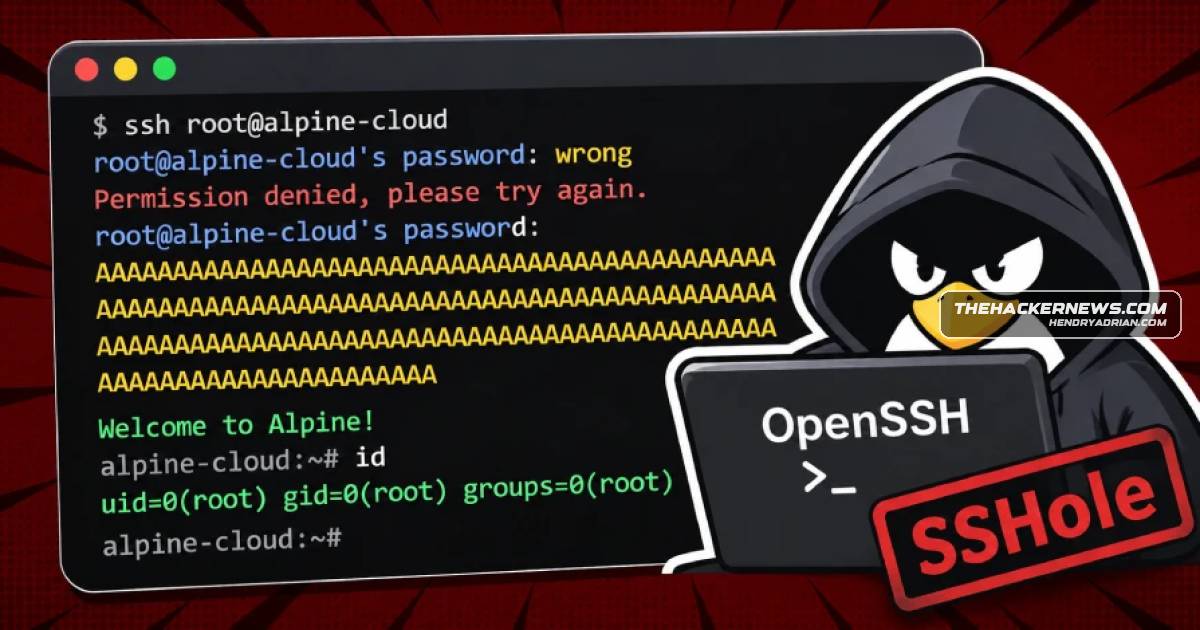
Previdian reported exploitation attempts within nine hours of SSHole’s disclosure and confirmed root access on an Alpine Linux honeypot. The flaw affects specific musl-based OpenSSH configurations; OpenSSH 10.6p2 addresses it.

Nov 6, 2026
Vulnerability & Exploit · securityweek.com

OpenSSH Patches SSHole Authentication Bypass Affecting Some Linux Configurations

OpenSSH 10.6p2 fixes SSHole (CVE-2026-123158), an authentication bypass affecting certain musl-based Linux systems with PAM disabled. Attackers may log in using a 257–1,024-character password; no exploitation reports were known.

Nov 6, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Paint CVE-2026-83844 Fix Requires a Microsoft Store Update

Microsoft Paint's CVE-2026-83844 fix is available through the Store, not Windows Update. The article notes conflicting fixed-version records and provides commands to check per-user and provisioned copies; rollout timing is unclear.

Nov 6, 2026
Vulnerability & Exploit · socprime.com

OpenSSH Password-Authentication Bypass Affects Certain musl-Based Linux Systems

CVE-2026-123158 (“SSHhole”) can bypass SSH password authentication on qualifying musl-based Linux systems, especially Alpine, when PAM is disabled. OpenSSH and Alpine have issued fixes; no in-the-wild exploitation was reported as of Nov. 6, 2026.

Nov 6, 2026
Vulnerability & Exploit · cisa.gov

CISA Adds Actively Exploited SonicWall SonicOS SSLVPN Vulnerability to KEV Catalog

CISA added CVE-2026-19868, a SonicWall SonicOS SSLVPN single-factor authentication vulnerability, to its Known Exploited Vulnerabilities Catalog based on evidence of active exploitation.

Nov 6, 2026
Vulnerability & Exploit · socradar.io

OpenSSH ‘sshole’ Password Bypass Exploited in the Wild, Added to CISA KEV

CVE-2026-123158 lets attackers bypass SSH password checks on some musl-based Linux systems without PAM. Attempts and honeypot compromises were reported; no production compromise was publicly confirmed. OpenSSH 10.6p2 and Alpine packages fix the flaw.

Nov 6, 2026
Vulnerability & Exploit · socradar.io

Microsoft Paint CVE-2026-83844 Requires Store-App Version Checks

CVE-2026-83844 is an out-of-bounds read in Microsoft Paint with potential remote code execution impact. Microsoft reports no known exploitation; organizations should verify Store-installed and provisioned packages are build 11.2609.401.0 or later.

Nov 6, 2026
Vulnerability & Exploit · thehackernews.com

Barracuda Email Security Gateway Flaws Can Be Chained for Unauthenticated Root Access

Researchers showed that CVE-2026-116606 and CVE-2026-111560 can be chained to gain unauthenticated root access to Barracuda Email Security Gateway appliances. Barracuda patched affected products; the ESG fix is firmware 9.4.0.030 or later.

Nov 6, 2026
Vulnerability & Exploit · fieldeffect.com

OpenSSH 10.6p2 Fixes Password Authentication Bypass on Alpine Linux

OpenSSH 10.6p2 fixes CVE-2026-123158, which can allow SSH password authentication bypass on certain musl-based systems, including Alpine Linux. Exploitation requires specific account and configuration conditions; no activity was reported at disclosure.

Nov 6, 2026
Vulnerability & Exploit · bleepingcomputer.com

SonicWall Patches Exploited SonicOS SSL-VPN SAML Authentication Bypass

SonicWall patched seven SonicOS flaws, including CVE-2026-19868, an SSL-VPN SAML authentication bypass affecting SAML-configured services. CISA added it to KEV, confirming in-the-wild exploitation; fixes cover specified Gen7 and Gen8 versions.

Nov 6, 2026
PreviousPage 8 of 65 Next
© 2026 cyber.hendryadrian.com