Huntress Reports Exploitation of Mjobtime SQL Injection Vulnerability
Summary
Huntress observed three customer incidents linked to CVE-2025-51683, a blind SQL injection flaw in Mjobtime 15.7.2. Attackers enabled xp_cmdshell and ran commands; Huntress found no subsequent activity.
Key points
- Huntress analysts linked three customer incidents in 2025 to exploitation of the blind SQL injection vulnerability CVE-2025-51683 in Mjobtime version 15.7.2.
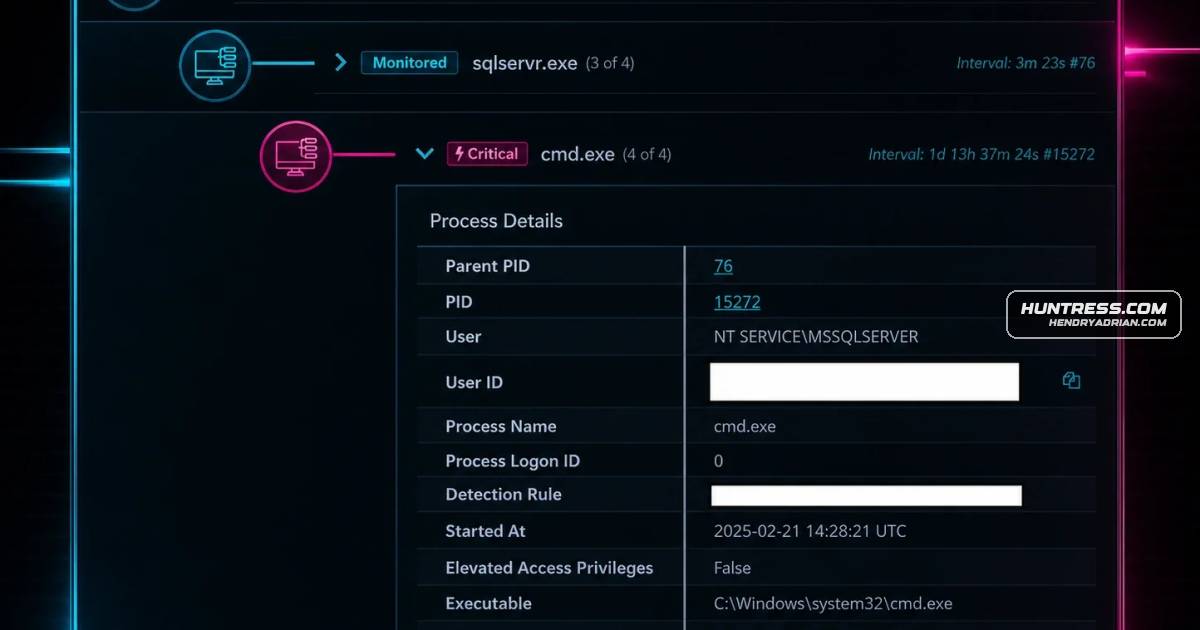
- In the incidents, IIS logs showed repeated POST requests to /Default.aspx/update_profile_Server before xp_cmdshell was enabled on the MSSQL instance.
- In one incident, an attacker ran `net user` and pinged ei0lwafp0h7178z7qer9r9oualgc45su[.]oastify[.]com before Huntress detected the activity and isolated the host.
- In two other incidents, commands using wget and curl targeted the same resource. Huntress reported no further activity after those commands.
- The web and database servers were on the same endpoint in two incidents and on separate endpoints in the third.
- The article found no indication of an available Mjobtime patch and advises users to contact the vendor about remediation.
Article Details
- Vulnerability Types
- Blind SQL injection
- Affected Versions
- Mjobtime 15.7.2
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- unknown
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ei0lwafp0h7178z7qer9r9oualgc45su[.]oastify[.]com | Resource targeted by a ping command during exploitation of Mjobtime; the article does not establish its precise purpose. |
MITRE ATT&CK
CVE
People
Products
FOUNDATIONThis was the case in the fall of 2024 with the FOUNDATION accounting software.Internet Information Services (IIS)Mjobtime is a web-based application, installed on the Microsoft Internet Information Server (IIS) web server, and relies on an MSSQL database backend.MjobtimeAnother such application is named Mjobtime, and is described as “all-in-one construction software for labor time tracking, construction equipment tracking, and reporting.MSSQLThe Huntress SOC team flagged a number of incidents where commands were being run via the installed MSSQL instance (i.e., sqlservr.exe), and in those incidents, the customer had installed the FOUNDATION accounting