
Critical nginx-ui Flaw Enables Unauthenticated Nginx Takeover; Patch Available
Summary
CVE-2026-33032 (CVSS 9.8) lets unauthenticated network attackers invoke nginx-ui MCP tools through /mcp_message, potentially altering Nginx configurations. Version 2.3.4 fixes it; Recorded Future listed it among March’s actively exploited flaws, but details were not yet
Key points
- CVE-2026-33032, dubbed MCPwn, is a CVSS 9.8 authentication bypass in nginx-ui.
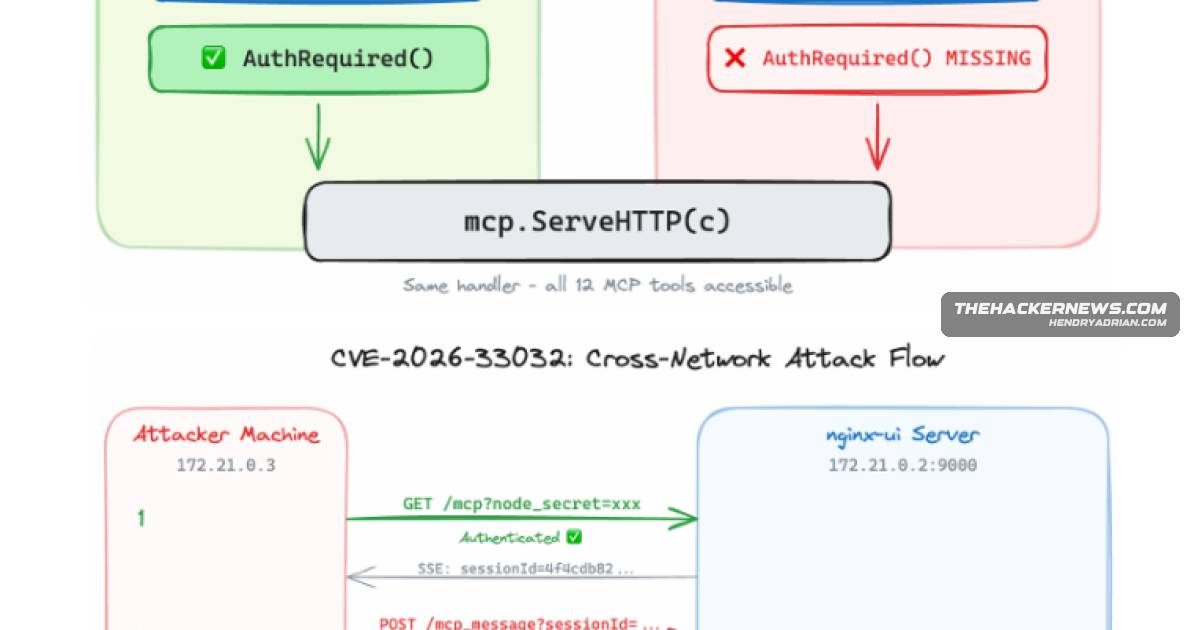
- The /mcp_message endpoint applies IP allowlisting but not authentication; an empty allowlist defaults to allowing all.
- The described exploit uses a GET request to /mcp to obtain a session ID, followed by a POST to /mcp_message to invoke MCP tools without authentication.
- The tools can modify Nginx configuration files and restart or reload the server; the article says exploitation could also enable traffic interception and credential harvesting.
- nginx-ui version 2.3.4, released March 15, 2026, fixes the flaw. Workarounds include adding authentication middleware to /mcp_message or changing the allowlist default to deny-all.
- Shodan data cited in the article showed about 2,689 publicly exposed nginx-ui instances.
- Recorded Future listed the flaw among vulnerabilities actively exploited in March 2026, but the article says details about exploitation activity were unavailable.
Article Details
- Vulnerability Types
- Authentication bypass
- Severity
- Critical (CVSS 9.8)
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Add middleware.AuthRequired() to the /mcp_message endpoint to require authentication.
- Change the IP allowlisting default from allow-all to deny-all.
- Disable MCP functionality and restrict network access as interim measures.
MITRE ATT&CK
CVE
People
Products
NGINXA critical authentication-bypass vulnerability in nginx-ui (CVE-2026-33032) enables attackers to invoke MCP tools via the unauthenticated /mcp_message endpoint to restart Nginx, modify configs, reload the server, andNginx UIA critical authentication-bypass vulnerability in nginx-ui (CVE-2026-33032) enables attackers to invoke MCP tools via the unauthenticated /mcp_message endpoint to restart Nginx, modify configs, reload the server, and
Countries
ChinaData from Shodan shows that there are about 2,689 exposed instances on the internet, with most of them located in China, the U.S., Indonesia, Germany, and Hong Kong.GermanyData from Shodan shows that there are about 2,689 exposed instances on the internet, with most of them located in China, the U.S., Indonesia, Germany, and Hong Kong.Hong KongData from Shodan shows that there are about 2,689 exposed instances on the internet, with most of them located in China, the U.S., Indonesia, Germany, and Hong Kong.IndonesiaData from Shodan shows that there are about 2,689 exposed instances on the internet, with most of them located in China, the U.S., Indonesia, Germany, and Hong Kong.United StatesData from Shodan shows that there are about 2,689 exposed instances on the internet, with most of them located in China, the U.S., Indonesia, Germany, and Hong Kong.