cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

Wordfence Reports 170+ Exploitation Attempts Against Breeze Cache Flaw

Wordfence reported more than 170 exploitation attempts targeting CVE-2026-3844, an unauthenticated arbitrary-file-upload flaw in Breeze Cache versions through 2.4.4 when its Gravatars add-on is enabled. Cloudways fixed it in 2.4.5.
Apr 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited BlueHammer Flaw

CISA set a May 7 patch deadline for federal agencies after CVE-2026-33825 was added to its KEV Catalog. The flaw lets low-privileged local users gain SYSTEM access; Huntress reported hands-on-keyboard activity.

Apr 23, 2026
Vulnerability & Exploit · securityweek.com

Apple Patches iOS Flaw That Retained Deleted Notification Previews

Apple patched CVE-2026-28950, a logging flaw that retained deleted notification previews. The FBI reportedly used it to recover Signal chats; Apple did not confirm exploitation in the wild.

Apr 23, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Defender Zero-Day CVE-2026-33825 Exploited Using Public PoC

Huntress reports attacks using public PoCs for the patched Microsoft Defender privilege-escalation flaw CVE-2026-33825. The activity involved BlueHammer, RedSun and UnDefend; CISA added the flaw to its KEV catalog.

Apr 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

Mirai Campaign Exploits CVE-2025-29635 in End-of-Life D-Link Routers

Akamai SIRT observed attempts exploiting CVE-2025-29635 in D-Link DIR-823X routers, deploying the multi-architecture Mirai variant tuxnokill. The models reached end of life in November 2024; users are advised to upgrade and secure router access.

Apr 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Apple Patches iOS Bug That Could Retain Deleted Notifications

Apple patched CVE-2026-28950 in iOS and iPadOS after deleted notifications could remain stored on devices. Reporting linked retained notification data to recovery of Signal messages, but Apple did not confirm exploitation or that connection.

Apr 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

More Than 1,300 SharePoint Servers Remain Unpatched for Exploited Spoofing Flaw

More than 1,300 internet-exposed SharePoint servers reportedly remain unpatched for CVE-2026-32201, a spoofing flaw Microsoft patched in April 2026. Shadowserver reports fewer than 200 patched; CISA ordered federal agencies to remediate.

Apr 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Patches Critical ASP.NET Core Flaw That Could Enable SYSTEM Privilege Escalation

CVE-2026-40372 could let unauthenticated attackers forge ASP.NET Core authentication cookies and gain SYSTEM privileges. Microsoft released version 10.0.7; customers should redeploy and rotate DataProtection keys.

Apr 22, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Fixes ASP.NET Core Privilege-Escalation Flaw CVE-2026-40372

Microsoft fixed CVE-2026-40372 in ASP.NET Core 10.0.7. A DataProtection regression could let attackers forge payloads and gain SYSTEM privileges on affected non-Windows applications; rotating the key ring is needed to invalidate tokens issued during the vulnerable perio

Apr 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags Cisco SD-WAN Flaw as Actively Exploited, Orders Agencies to Patch

CISA added Cisco Catalyst SD-WAN Manager flaw CVE-2026-20133 to its KEV catalog based on evidence of active exploitation and ordered federal agencies to secure affected systems by April 24. Cisco says it is unaware of public exploitation.

Apr 21, 2026
Vulnerability & Exploit · thehackernews.com

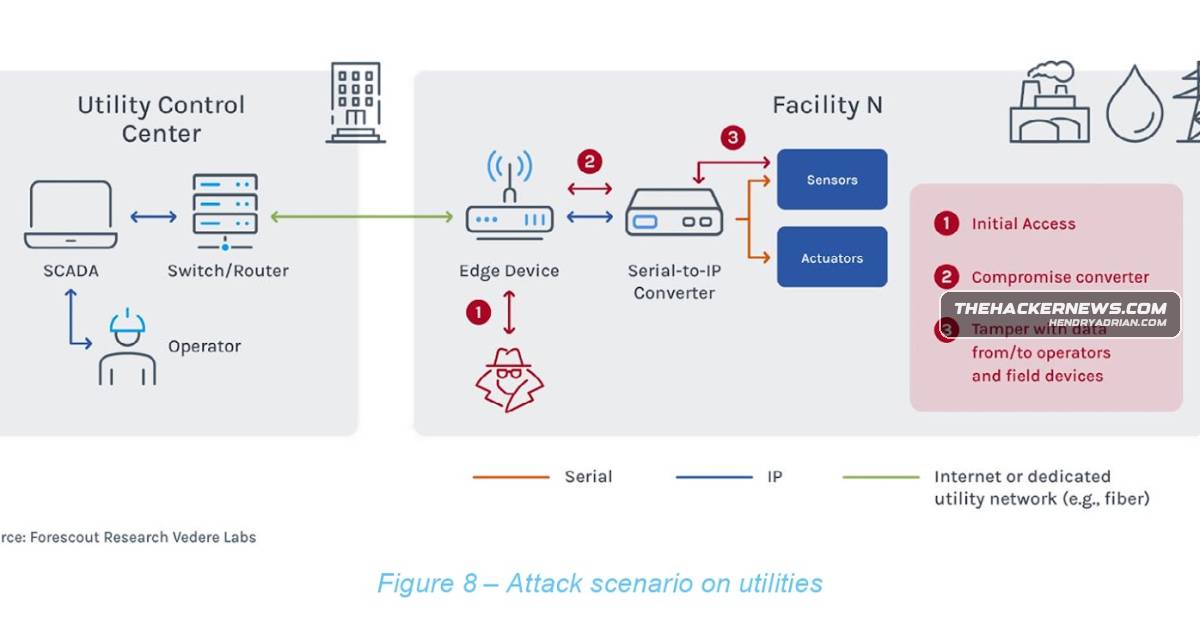
BRIDGE:BREAK Flaws Put Nearly 20,000 Serial-to-IP Converters at Risk

Forescout identified 22 BRIDGE:BREAK flaws in Lantronix and Silex serial-to-IP converters, with nearly 20,000 devices exposed online. Exploitation could disrupt communications or tamper with data; vendors released patches.

Apr 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

Actively Exploited Apache ActiveMQ Flaw Affects 6,400 Exposed Servers

Shadowserver found over 6,400 exposed Apache ActiveMQ servers vulnerable to CVE-2026-34197, an actively exploited authenticated code-execution flaw. Apache patched ActiveMQ Classic 6.2.3 and 5.19.4; CISA set an April 30 deadline for federal agencies.

Apr 21, 2026
Vulnerability & Exploit · thehackernews.com

SGLang CVE-2026-5760 Could Enable RCE via Malicious GGUF Models

CVE-2026-5760 (CVSS 9.8) affects SGLang’s /v1/rerank endpoint: a loaded malicious GGUF model can exploit an unsandboxed Jinja2 template to execute Python code. CERT/CC recommends ImmutableSandboxedEnvironment; no patch response was obtained.

Apr 21, 2026
Vulnerability & Exploit · cyberscoop.com

Google Antigravity Flaw Let Prompt Injection Bypass Secure Mode for Remote Code Execution

Pillar Security said a now-patched flaw in Google Antigravity let prompt injection abuse the native find_by_name tool to bypass Secure Mode and achieve remote code execution. Google patched it Feb. 28 after a Jan. 6 report.

Apr 20, 2026
Vulnerability & Exploit · securityweek.com

BRIDGE:BREAK Flaws in Serial-to-IP Converters Could Enable Remote Attacks

Forescout identified 20 BRIDGE:BREAK vulnerabilities in Lantronix and Silex serial-to-IP converters, including flaws that could enable remote code execution, firmware tampering, denial of service, or device takeover. Both vendors released patches.

Apr 20, 2026
Vulnerability & Exploit · thecyberexpress.com

Cisco Patches ISE and Webex Flaws That Could Enable RCE and User Impersonation

Cisco patched three ISE vulnerabilities that could enable command execution and privilege escalation, plus a Webex SSO flaw that could allow user impersonation. Cisco reported no known exploitation; no workarounds are available.

Apr 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

PoC Published for Critical protobuf.js Flaw Enabling Remote Code Execution

A flaw in protobuf.js versions 8.0.0/7.5.4 and earlier lets malicious schemas trigger code execution. A PoC is available; upgrade to 8.0.1 or 7.5.5. No active exploitation has been observed.

Apr 18, 2026
Vulnerability & Exploit · helpnetsecurity.com

Huntress Says RedSun and UnDefend Exploits Used Alongside BlueHammer

Huntress says attackers used RedSun and UnDefend Microsoft Defender exploit PoCs alongside BlueHammer. The attacks involved renamed files in user folders and commands to map privileges, recover credentials, and enumerate Active Directory.

Apr 18, 2026
Vulnerability & Exploit · thecyberexpress.com

Critical nginx-ui Flaw (CVE-2026-33032) Enables Nginx Server Takeover

CVE-2026-33032 lets unauthenticated attackers use nginx-ui’s MCP endpoint to take over Nginx servers. The article reports in-the-wild exploitation and describes a chain involving CVE-2026-27944; nginx-ui 2.3.4 addresses the issue.

Apr 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags Apache ActiveMQ Flaw CVE-2026-34197 as Actively Exploited

CISA says attackers are actively exploiting CVE-2026-34197, an authenticated code-execution flaw in Apache ActiveMQ. Apache patched ActiveMQ Classic versions 6.2.3 and 5.19.4; federal agencies face an April 30 patching deadline.

Apr 17, 2026
Vulnerability & Exploit · securityweek.com

NomShub Cursor AI Flaw Could Let Malicious Repositories Hijack Developer Macs

Straiker disclosed NomShub, a Cursor AI exploit chain in which prompts in a malicious repository could trigger a sandbox bypass and abuse the remote tunnel for persistent access to macOS devices. Cursor fixed the issue in version 3.0.

Apr 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

RedSun PoC Exploits Microsoft Defender Behavior to Gain SYSTEM Privileges

Chaotic Eclipse’s RedSun PoC reportedly abuses Defender’s Cloud Files behavior to overwrite a system executable and gain SYSTEM on fully patched Windows systems with Defender enabled; Will Dormann confirmed it works.

Apr 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

Huntress Reports Exploitation of Three Leaked Windows Zero-Days

Huntress says attackers used leaked BlueHammer, RedSun and UnDefend Windows exploits to gain elevated privileges. Microsoft patched BlueHammer (CVE-2026-33825); RedSun and UnDefend remain unpatched.

Apr 17, 2026
Vulnerability & Exploit · varonis.com

AWS Updates CloudTrail After Varonis Finds Logging Gap for Anonymous S3 Requests

Varonis Threat Labs reported that anonymous requests to external S3 buckets through VPC endpoints could go unlogged in CloudTrail. AWS updated logging so these requests are recorded as Network Activity events in the endpoint owner's account.

Apr 17, 2026
PreviousPage 54 of 65 Next
© 2026 cyber.hendryadrian.com