
Gogs Zero-Day Flaw Allows Authenticated Users to Execute Remote Code
Summary
Rapid7 says an unpatched argument-injection flaw in Gogs 0.14.2 and 0.15.0+dev lets authenticated non-admin users execute code remotely. Default open registration may let attackers create accounts on exposed servers.
Key points
- The unpatched flaw affects Gogs 0.14.2 and 0.15.0+dev; the article says it has no CVE ID.
- Exploitation requires an authenticated non-admin account, but default open registration may allow attackers to create one.
- A malicious branch name in a pull request can inject an argument into Git rebase during the “Rebase before merging” operation.
- Successful exploitation could allow code execution as the Gogs server process user and expose private repositories, credentials, and connected systems.
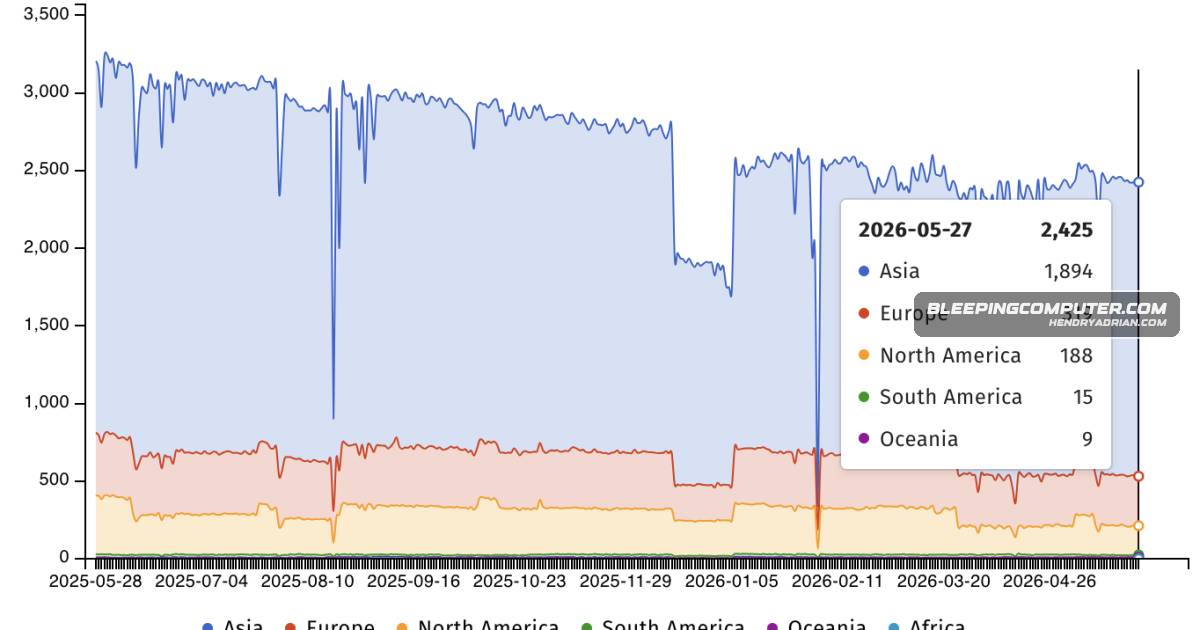
- Shadowserver tracks more than 2,400 exposed Gogs servers; Shodan found just over 1,000 IP addresses with a Gogs fingerprint.
- The researcher reported the flaw to Gogs maintainers, who had acknowledged the report but had not provided a patch or status update, according to the article.
Article Details
- Vulnerability Types
- Argument injection
- Severity
- Critical
- Affected Versions
- Gogs 0.14.2
- Gogs 0.15.0+dev
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- unavailable