
WP Maps Pro Flaw Exploited in Attempts to Create WordPress Admin Accounts
Summary
CVE-2026-8732 lets unauthenticated attackers create WordPress administrator accounts through WP Maps Pro 6.1.0 and older. Defiant reported blocking over 3,600 exploit attempts in 24 hours; version 6.1.1 fixes the flaw.
Key points
- CVE-2026-8732 affects WP Maps Pro versions 6.1.0 and older.
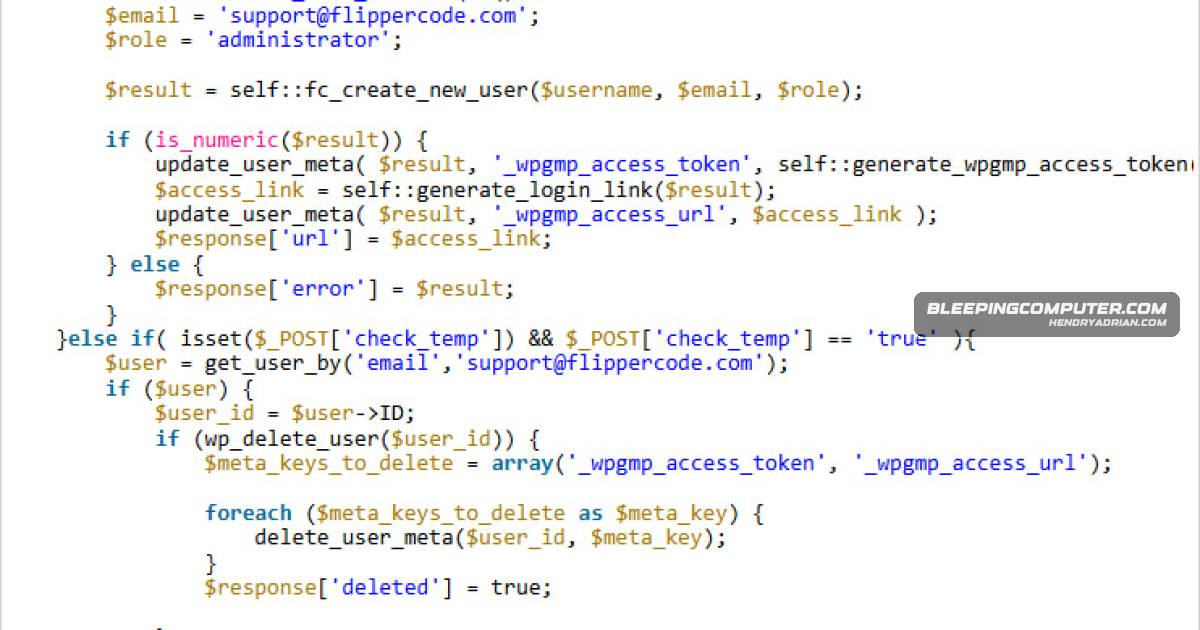
- The plugin’s temporary-access AJAX endpoint was available without authentication and relied on a publicly exposed nonce check.
- A crafted request could create an administrator account and generate a passwordless login URL.
- Defiant reported blocking more than 3,600 exploit attempts in the previous 24 hours; the article does not establish successful compromises.
- WP Maps Pro 6.1.1, released May 20, fixes the vulnerability; administrators are urged to update.
Article Details
- Vulnerability Types
- Unauthenticated administrator account creation
- Severity
- Critical
- Affected Versions
- WP Maps Pro 6.1.0 and older
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
People
Vendors
Products
Wordfence#WPMapsProWordPressHackers are actively targeting WordPress sites running vulnerable WP Maps Pro versions to create rogue administrator accounts without authentication.WP Maps ProHackers are actively targeting WordPress sites running vulnerable WP Maps Pro versions to create rogue administrator accounts without authentication.