cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

Gogs patches zero-day flaw that could enable remote code execution

Gogs released version 0.14.3 to fix a zero-day argument-injection flaw affecting releases through 0.14.2 and 0.15.0+dev. Authenticated users could compromise servers; Rapid7 recommends upgrading or restricting registration and repository creation.
Jun 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Check Point Patches Exploited VPN Zero-Day Linked to Qilin Affiliate

Check Point patched CVE-2026-50751, an authentication bypass actively exploited against a few dozen organizations; one case involved confirmed post-compromise activity associated with a Qilin affiliate. CVE-2026-50752 affects IKEv1 certificate validation; no in-the-wild

Jun 8, 2026
Vulnerability & Exploit · securityweek.com

Actively Exploited Everest Forms Pro Flaw Enables WordPress Site Takeovers

CVE-2026-3300, a CVSS 9.8 flaw in Everest Forms Pro, allows unauthenticated PHP code injection via Complex Calculation forms. Defiant reports exploitation since April 13 and urges upgrading to version 1.9.13 or later.

Jun 8, 2026
Vulnerability & Exploit · securityweek.com

CISA Flags Exploitation of SolarWinds Serv-U DoS Vulnerability

CISA added unauthenticated Serv-U DoS flaw CVE-2026-28318 to its Known Exploited Vulnerabilities catalog. SolarWinds fixed it in Serv-U 15.5.4 Hotfix 1; the attacker and possible zero-day status are unknown.

Jun 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Exploit Everest Forms Pro Flaw to Take Over WordPress Sites

Wordfence reports active exploitation of CVE-2026-3300, an unauthenticated code-execution flaw in Everest Forms Pro 1.9.12 and earlier. Attackers are creating rogue administrator accounts; a patch was released March 18.

Jun 6, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited SolarWinds Serv-U DoS Flaw to KEV

CISA added CVE-2026-28318, an actively exploited SolarWinds Serv-U denial-of-service flaw, to its KEV catalog. SolarWinds patched it in version 15.5.4 HF1; exploitation details and any compromised instances are unknown.

Jun 6, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Warns CVE-2026-20245 in Catalyst SD-WAN Manager Is Under Active Exploitation

Cisco says attackers are exploiting CVE-2026-20245 in Catalyst SD-WAN Manager to run commands as root. Limited cases involved configuration changes pushed to edge devices; no patch or mitigation is available.

Jun 6, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Active Exploitation of SolarWinds Serv-U DoS Flaw

CISA says attackers are exploiting CVE-2026-28318 to crash exposed SolarWinds Serv-U servers without authentication. SolarWinds released a hotfix and mitigations; CISA ordered federal agencies to patch by June 19.

Jun 5, 2026
Vulnerability & Exploit · guardsix.com

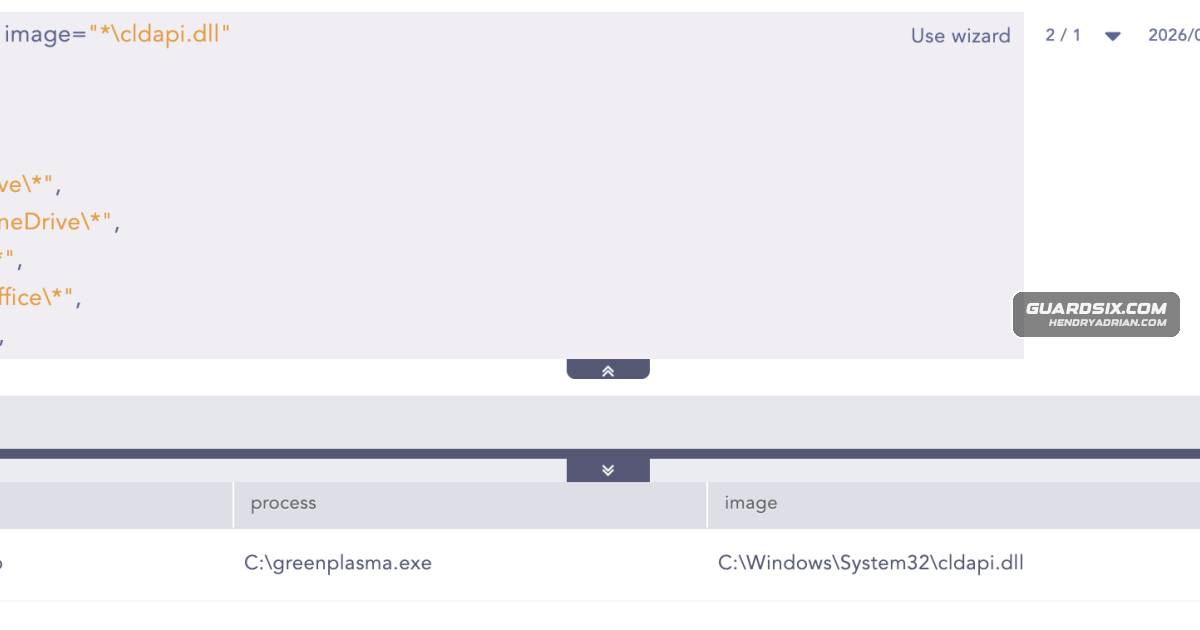
Three Windows Zero-Days Target BitLocker and Enable SYSTEM Privilege Escalation

Chaotic Eclipse disclosed three Windows zero-days: YellowKey bypasses BitLocker via WinRE, while GreenPlasma and MiniPlasma can enable SYSTEM access. Microsoft has a YellowKey mitigation, but no vendor patch is available for GreenPlasma or MiniPlasma.

Jun 5, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Warns of Actively Exploited SD-WAN Zero-Day Enabling Root Access

Cisco says attackers are exploiting unpatched CVE-2026-20245 in Catalyst SD-WAN Manager to gain root privileges. The flaw requires netadmin access; Cisco advises checking logs while a patch remains unavailable.

Jun 5, 2026
Vulnerability & Exploit · securityweek.com

Cisco Warns of Exploited Catalyst SD-WAN Zero-Day, Patch Pending

Cisco says CVE-2026-20245, an unpatched flaw in Catalyst SD-WAN Manager, has been exploited. An authenticated local attacker with netadmin privileges can run commands as root; Cisco observed limited cases involving configuration changes to edge devices.

Jun 5, 2026
Vulnerability & Exploit · thehackernews.com

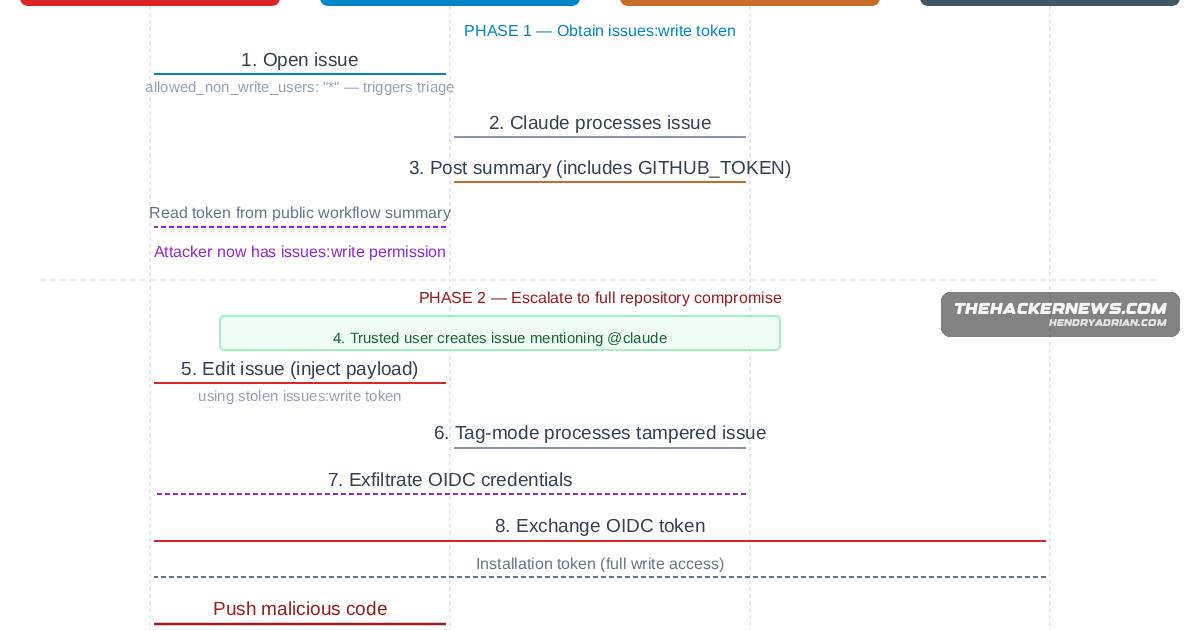
Claude Code GitHub Action Flaw Could Let Malicious Issues Hijack Repositories

A researcher showed how a flawed trigger check and indirect prompt injection could expose workflow secrets and enable repository write access. Anthropic fixed the issue in v1.0.94; the exact path was tested in the researcher’s repos, with no public evidence of live use.

Jun 5, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Patches Unified CM Flaw After CVE-2026-20230 Exploit Code Goes Public

Cisco patched CVE-2026-20230, an unauthenticated SSRF flaw in Unified CM that can enable arbitrary file writes and root escalation when WebDialer is enabled. PoC code is public; Cisco says it has not observed attacks.

Jun 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Critical Unified CM Flaw With Public PoC Exploit Code

Cisco patched CVE-2026-20230, a critical remote SSRF flaw that could let unauthenticated attackers write files and later gain root access on Unified CM systems with WebDialer enabled. Public PoC code exists, but Cisco reports no active exploitation evidence.

Jun 4, 2026
Vulnerability & Exploit · securityweek.com

Mirasvit Magento Extension Flaw Exploited for Remote Code Execution

CISA added CVE-2026-45247 to its KEV catalog after reported in-the-wild exploitation of a remote PHP object injection flaw in Mirasvit Cache Warmer. Install version 1.11.12 or newer; Sansec also described a cookie-based exploitation indicator.

Jun 4, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited Magento Cache Warmer Flaw CVE-2026-45247 to KEV

CISA added CVE-2026-45247, an unauthenticated RCE flaw in Mirasvit Cache Warmer versions before 1.11.12, to its KEV catalog after Sansec and Imperva reported active exploitation. The fix was released May 25, 2026.

Jun 4, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Unified CM Vulnerability With PoC Code Available

Cisco patched CVE-2026-20230 in Unified CM and Unified CM SME. The SSRF flaw could enable file writes leading to root privileges; PoC code is available, but Cisco says it has not seen exploitation.

Jun 4, 2026
Vulnerability & Exploit · securityweek.com

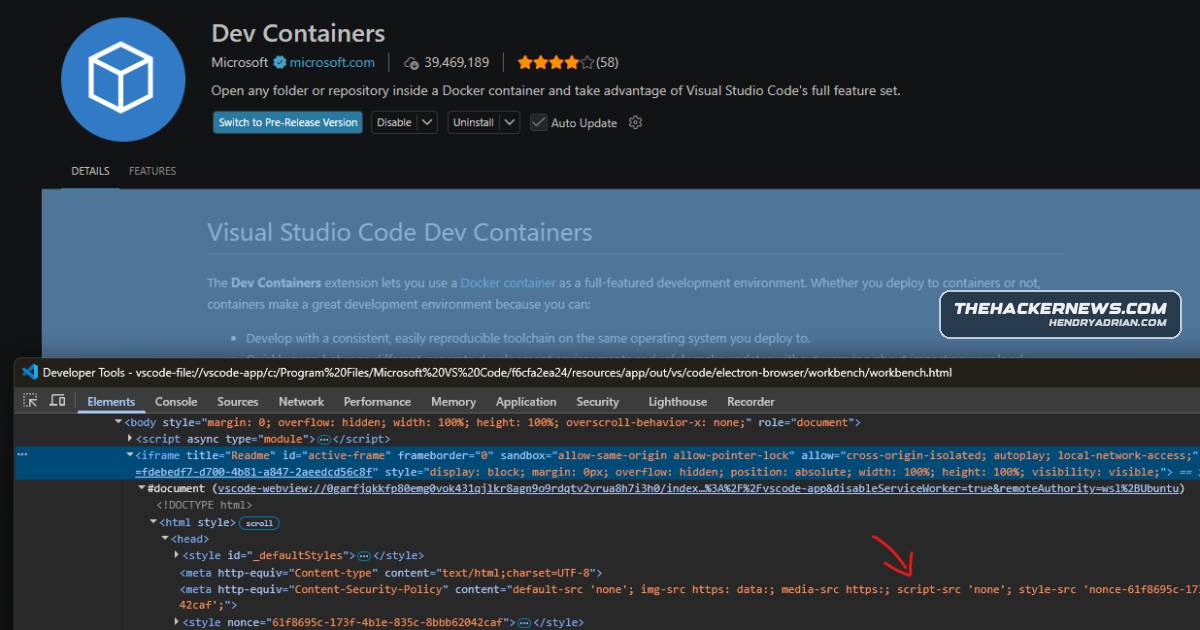
VS Code Flaw Lets Malicious Notebooks Steal GitHub Tokens

A crafted Jupyter notebook opened on github[.]dev can install a malicious extension that steals GitHub tokens. Microsoft says its services are mitigated; the desktop version appears unpatched and may allow remote code execution.

Jun 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

HTTP/2 Bomb DoS Can Exhaust Web Server Memory in Seconds

Researchers say HTTP/2 Bomb combines HPACK amplification with flow-control stalling to exhaust web-server memory. nginx and Apache have fixes; the article says IIS, Envoy, and Pingora had no patches at publication.

Jun 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Adds Android and Linux Flaws to KEV After Exploitation Evidence

CISA added Android CVE-2025-48595 and Linux CVE-2022-0492 to its KEV catalog. Android 14–16 are affected by the first flaw; the second can enable container escape. Federal agencies face a June 5 deadline to patch or stop using affected software.

Jun 3, 2026
Vulnerability & Exploit · thehackernews.com

One-Click Attack Can Steal GitHub OAuth Tokens Through GitHub.dev and VS Code Webviews

A researcher disclosed a one-click attack that can expose GitHub OAuth tokens through GitHub[.]dev and VS Code webviews, potentially exposing private repositories. Microsoft acknowledged the issue and is working on a fix; VS Code Desktop is unaffected.

Jun 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

Acer Plans Fixes for Two Maximum-Severity Zero-Days in Wave 7 Routers

Acer says two zero-days affect Wave 7 routers running firmware T7c_GBL_1.01.000055 or earlier. They can expose plaintext credentials or enable persistent backdoor access. Fixes are planned by the end of June 2026; Acer advises disabling remote management meanwhile.

Jun 3, 2026
Vulnerability & Exploit · securityweek.com

Attackers Target Vulnerabilities in Kirki and Burst Statistics WordPress Plugins

Defiant says it blocked thousands of attacks targeting flaws in Kirki and Burst Statistics WordPress plugins. The bugs can enable administrator account takeover; updates are available for both plugins.

Jun 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

VS Code Zero-Day Can Steal GitHub OAuth Tokens via Malicious Link

Researcher Ammar Askar released a proof-of-concept for an unpatched VS Code flaw that can steal GitHub OAuth tokens through a malicious link and enumerate accessible private repositories. Clearing github[.]dev site data can reduce risk.

Jun 3, 2026
PreviousPage 47 of 65 Next
© 2026 cyber.hendryadrian.com