Three Windows Zero-Days Target BitLocker and Enable SYSTEM Privilege Escalation
Summary
Chaotic Eclipse disclosed three Windows zero-days: YellowKey bypasses BitLocker via WinRE, while GreenPlasma and MiniPlasma can enable SYSTEM access. Microsoft has a YellowKey mitigation, but no vendor patch is available for GreenPlasma or MiniPlasma.
Key points
- YellowKey (CVE-2026-45585, CVSS 6.8) can expose a BitLocker-protected drive after brief physical access by abusing WinRE; Windows 11 and Server 2022/2025 are affected, but Windows 10 is not.
- GreenPlasma abuses Windows CTFMON and Cloud Files-related trust and registry behavior to pursue local privilege escalation; its released PoC is incomplete and may trigger a UAC prompt.
- MiniPlasma exploits a race condition involving the Cloud Files Mini Filter Driver, cldflt.sys, to obtain SYSTEM access; it reportedly revives a flaw associated with CVE-2020-17103.
- The article reports that public PoCs were removed from GitHub and GitLab. Microsoft has published a WinRE remediation script for YellowKey, but no vendor-provided patch is available for GreenPlasma or MiniPlasma.
- Recommended mitigations include application control, a BitLocker startup PIN, restricting physical access and USB boot, and disabling Cloud Files components where they are not needed.
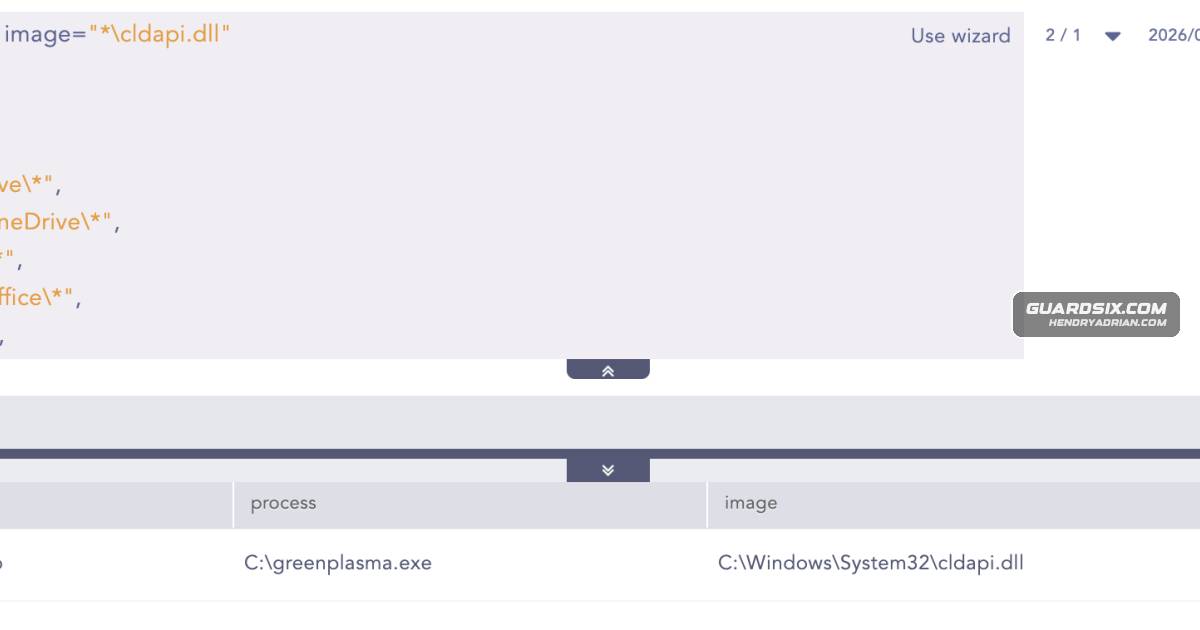
- Suggested detection focuses on unexpected cldapi.dll loads, CloudFiles registry changes and symbolic links, YellowKey-related USB activity, suspicious wermgr.exe execution, and MiniPlasma's named pipe.
Article Details
- Vulnerability Types
- BitLocker drive-encryption bypass (YellowKey)
- Local privilege escalation (GreenPlasma and MiniPlasma)
- Race condition in privileged registry operations (MiniPlasma)
- Severity
- CVSS 6.8 for YellowKey; severity not stated for GreenPlasma or MiniPlasma.
- Affected Versions
- Windows 11
- Windows Server 2022
- Windows Server 2025
- Windows 10 is not affected by YellowKey. The article says MiniPlasma does not appear to affect Windows 10, while Chaotic Eclipse claims all Windows versions are likely vulnerable.
- Exploitation Status
- unknown
- Exploit Availability
- public_poc
- Patch Status
- partial
- Workarounds
- For YellowKey, apply Microsoft's WinRE remediation script, which removes autofstx.exe from the WinRE BootExecute registry value; the article says this is a mitigation, not a permanent fix.
- For YellowKey, use TPM+PIN instead of TPM-only BitLocker mode.
- For YellowKey, restrict physical access and disable USB boot where feasible.
- For GreenPlasma and MiniPlasma, enforce a default-deny application control policy.
- Where Cloud Files functionality is not required, disable cldflt.sys and restrict access to cldp.dll.
MITRE ATT&CK
T1059.003 · Windows Command ShellYellowKey can expose an unrestricted command prompt in WinRE, and MiniPlasma launches cmd.exe in its SYSTEM shell chain.T1068 · Exploitation for Privilege EscalationGreenPlasma and MiniPlasma exploit Windows vulnerabilities to escalate from a user context to SYSTEM; YellowKey also provides unauthorized access to a BitLocker-protected drive.
CVE
CVE-2020-17103It is essentially a revival of CVE-2020-17103, a flaw Google Project Zero's James Forshaw reported to Microsoft in September 2020, and that Microsoft supposedly fixed that December.CVE-2026-45585YellowKey, tracked as CVE-2026-45585 (CVSS 6.8) is a publicly disclosed Windows zero-day vulnerability that bypasses BitLocker drive encryption by abusing behavior in the Windows Recovery Environment (WinRE).
People
Chaotic EclipseSecurity researcher who disclosed YellowKey, GreenPlasma, and MiniPlasma and released a PoC for each.James ForshawGoogle Project Zero researcher whom the article says reported the original CVE-2020-17103 flaw to Microsoft.Nightmare EclipseName the article gives for Chaotic Eclipse; the article says these names refer to the same researcher.
Vendors
Products
BitLockerYellowKey is a BitLocker bypass vulnerability that can potentially provide access to encrypted drives by leveraging weaknesses in the Windows Recovery Environment (WinRE).Microsoft OneDrivecldflt.sys is the kernel-side driver behind OneDrive's "Files On-Demand" feature.Microsoft Windows2026, security researcher Chaotic Eclipse (also known as Nightmare Eclipse) publicly disclosed three new Windows zero-day vulnerabilities dubbed YellowKey, GreenPlasma, and MiniPlasma, releasing a proof-of-conceptWindows 10Windows 10 is not affected.Windows 11YellowKey — Windows 11, Windows Server 2022, and Windows Server 2025.Windows Cloud Files platformPlaceholder files are special files managed by the Windows Cloud Files platform, where the actual contents may reside remotely and are hydrated on demand.Windows Recovery Environment (WinRE)YellowKey is a BitLocker bypass vulnerability that can potentially provide access to encrypted drives by leveraging weaknesses in the Windows Recovery Environment (WinRE).Windows Server 2022YellowKey — Windows 11, Windows Server 2022, and Windows Server 2025.Windows Server 2025YellowKey — Windows 11, Windows Server 2022, and Windows Server 2025.