
One-Click Attack Can Steal GitHub OAuth Tokens Through GitHub.dev and VS Code Webviews
Summary
A researcher disclosed a one-click attack that can expose GitHub OAuth tokens through GitHub[.]dev and VS Code webviews, potentially exposing private repositories. Microsoft acknowledged the issue and is working on a fix; VS Code Desktop is unaffected.
Key points
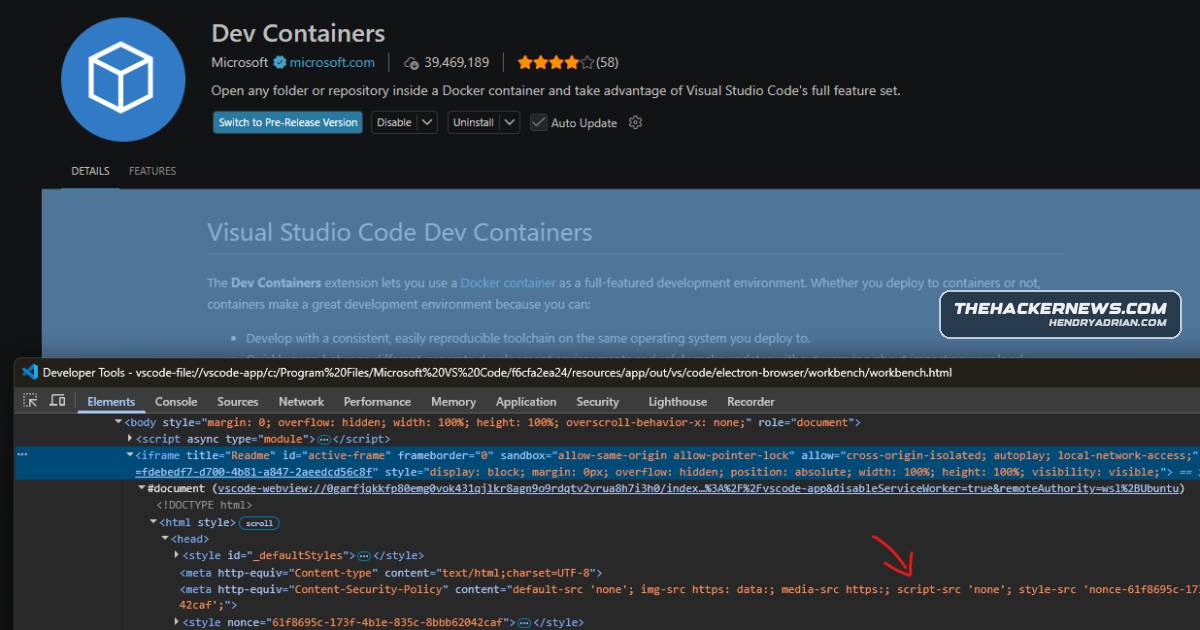
- Clicking a crafted link can trigger malicious JavaScript in an untrusted webview to simulate keypresses and open VS Code’s Command Palette.
- The attack can install an attacker-controlled extension that extracts the OAuth token passed to GitHub[.]dev.
- The researcher says the token can access repositories beyond the one opened, including private repositories.
- Local workspace extensions placed in the .vscode/extensions folder can bypass the publisher trust prompt.
- Microsoft acknowledged the vulnerability and said it is working on a fix; the issue does not affect VS Code Desktop.
Article Details
- Vulnerability Types
- Message-passing vulnerability between the main VS Code window and webviews
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- unavailable
MITRE ATT&CK
T1059.007 · JavaScriptMalicious JavaScript runs inside an untrusted VS Code webview and triggers keypresses in the main editor window.T1176 · Software ExtensionsThe attack installs an attacker-controlled VS Code extension through the local workspace extensions feature.T1204.001 · Malicious LinkThe attack begins when a victim clicks a crafted malicious link.T1213.003 · Code RepositoriesThe extension uses the GitHub API to enumerate private repositories accessible to the victim.T1528 · Steal Application Access TokenThe malicious extension extracts the GitHub OAuth token passed to GitHub.dev.
People
Vendors
GitHubA one-click attack in Microsoft Visual Studio Code and GitHub.dev can let an attacker steal a victim’s GitHub OAuth token after they click a crafted link.MicrosoftA one-click attack in Microsoft Visual Studio Code and GitHub.dev can let an attacker steal a victim’s GitHub OAuth token after they click a crafted link.
Products
GitHubA one-click attack in Microsoft Visual Studio Code and GitHub.dev can let an attacker steal a victim’s GitHub OAuth token after they click a crafted link.github.devA one-click attack in Microsoft Visual Studio Code and GitHub.dev can let an attacker steal a victim’s GitHub OAuth token after they click a crafted link.VSCodeA one-click attack in Microsoft Visual Studio Code and GitHub.dev can let an attacker steal a victim’s GitHub OAuth token after they click a crafted link.