
CYFIRMA Exploit Radar Highlights Five Vulnerabilities and Mitigations
Summary
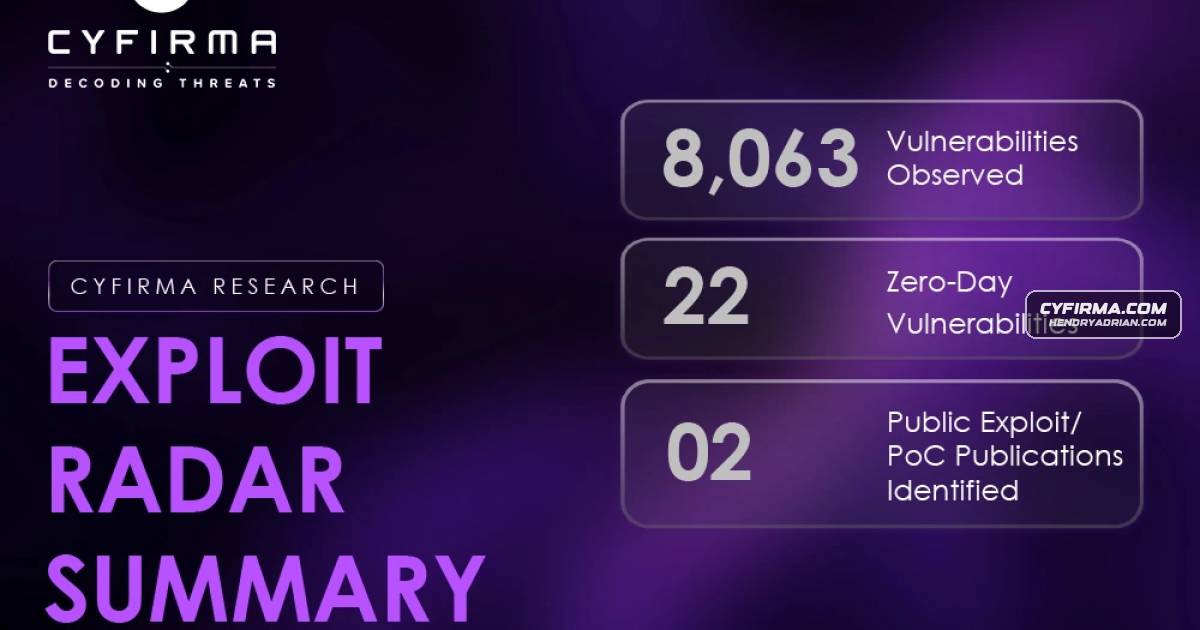
CYFIRMA’s fortnightly summary reports a 23.29% rise in observed vulnerabilities and details five CVEs affecting TOTOLINK, Portabase, blueprintUE, NextScan and Fider, with affected versions, risks and recommended fixes.
Key points
- CYFIRMA reports a 23.29% increase in observed vulnerabilities compared with the previous two weeks; Windows, Chrome and Android were the most affected products or technologies observed.
- CVE-2026-124058 affects TOTOLINK CA300-PoE firmware 6.2c.884; the article describes a remotely exploitable buffer overflow and recommends firmware updates and restricting remote management.
- CVE-2026-67449 affects Portabase versions before 1.21.2; unauthenticated attackers may overwrite sensitive files, including the AES master encryption key. Version 1.21.2 or later is recommended.
- CVE-2026-126812 affects blueprintUE Self-Hosted Edition versions before 4.3.7; exposed MariaDB services with empty root passwords may permit unauthorized database access.
- CVE-2026-126797 affects NextScan versions 1.1.0–1.2.0 and is described as an authentication bypass risk; the article recommends replacing hardcoded JWT signing keys and restricting administrator access.
- CVE-2026-65840 affects Fider before 0.36.0 in multi-tenant mode; the article describes risks involving JWT secrets, administrator accounts and tenant isolation. Single-host deployments are stated to be unaffected.
Article Details
- Vulnerability Types
- Buffer overflow
- Unauthenticated sensitive-file overwrite, including the AES master encryption key
- Unauthorized database access associated with exposed MariaDB services and empty root passwords
- Authentication bypass involving hardcoded JWT signing keys
- Cross-tenant authentication bypass and unauthorized access to sensitive log archives
- Severity
- NVD CVSS scores range from 9.1 to 9.8.
- Affected Versions
- TOTOLINK CA300-PoE 6.2c.884
- Portabase versions before 1.21.2
- blueprintUE Self-Hosted Edition versions 1.0.0 to before 4.3.7
- NextScan versions 1.1.0 to 1.2.0
- Fider versions before 0.36.0 in multi-tenant mode
- Exploitation Status
- unknown
- Exploit Availability
- public_exploit
- Patch Status
- partial
- Workarounds
- Restrict remote access to device management interfaces and disable unnecessary remote administration services.
- Restrict access to Portabase TUS upload endpoints; validate file paths and protect the AES master encryption key.
- Disable empty database root passwords and restrict MariaDB port 3306 to trusted networks.
- Replace hardcoded JWT signing keys with strong secrets and restrict administrator access to trusted users.
- Enforce tenant isolation and verify tenant-specific email authentication.
CVE
CVE-2026-124058TOTOLINK · CA300-PoE1. CVE-2026-124058 – TOTOLINK CA300-PoECVE-2026-126797tongcheng-security-team · NextScan4. CVE-2026-126797 – NextScanCVE-2026-126812blueprintue · blueprintue-self-hosted-edition3. CVE-2026-126812 – blueprintUE Self-Hosted EditionCVE-2026-65840getfider · fider5. CVE-2026-65840 – FiderCVE-2026-67449Portabase · portabase2. CVE-2026-67449 – Portabase
Products
blueprintUE Self-Hosted EditionCVE-2026-126812 – blueprintUE Self-Hosted Edition: Yes, if you use a version earlier than 4.3.7 with an exposed MariaDB service and an empty root password.FiderCVE-2026-65840 – Fider: Yes, if you use a version earlier than 0.36.0 in multi-tenant mode (HOST_MODE=multi).NextScanCVE-2026-126797 – NextScan: Yes, if your organization uses versions 1.1.0 to 1.2.0, which are vulnerable to authentication bypass.PortabaseUpgrade Portabase to version 1.21.2 or later.TOTOLINK CA300-PoECVE-2026-124058 – TOTOLINK CA300-PoE: Yes, if your network device is running firmware version 6.2c.884.