cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1523 articles

Vulnerability & Exploit · thehackernews.com

PTC Patches Critical Windchill and FlexPLM RCE Vulnerability

PTC patched CVE-2026-126325, a critical Windchill and FlexPLM flaw that could enable remote code execution through crafted requests and untrusted-data deserialization. Self-hosted users are urged to patch promptly.
Nov 12, 2026
Vulnerability & Exploit · securityweek.com

N-able Patches N-central Flaws as Attackers Probe Exposed Instances

N-able released patches for several N-central flaws disclosed with proof-of-concept code. The company says unauthenticated vulnerabilities are fixed, scanning is underway, and it has seen no indications of compromise on hosted servers.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

MongoDB Patches Critical Unauthenticated Flaw That Can Crash Lagging Replica-Set Members

CVE-2026-118383 lets unauthenticated clients send two requests that can trigger a crash when a lagging MongoDB replica-set member wins failover. MongoDB released fixes; researchers did not achieve code execution in their lab.

Nov 12, 2026
Vulnerability & Exploit · securityweek.com

Critical Red Hat Quay Flaw Could Expose Private Images and Enable Repository Overwrites

Red Hat says CVE-2026-123710 can let unauthenticated attackers take over Quay registry token signing, access or overwrite repositories, and persist malicious signing keys. The advisory gives no fixed version.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Node.js Fixes HTTP/2 and HTTPS Flaws That Can Crash Servers or Leak Memory

Node.js fixed 16 vulnerabilities, including flaws that let unauthenticated clients crash qualifying HTTP/2 servers or read memory from other connections. Fixes are available in 22.23.5, 24.22.3 and 26.13.1; no workaround is listed.

Nov 12, 2026
Vulnerability & Exploit · thehackernews.com

Apache HTTP/2 Flaw Could Allow Unauthenticated Remote Code Execution

CVE-2026-119618 affects Apache HTTP Server 2.4.55–2.4.70 when HTTP/2 is enabled; version 2.4.71 fixes it. Red Hat says reliable exploit research exists, while Wiz reported no available exploit or in-the-wild activity.

Nov 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

Researcher-Disclosed Windows SignDrop Zero-Day Can Grant SYSTEM Privileges

Researcher Abdelhamid Naceri says SignDrop abuses Windows CLFS authentication-file handling to gain SYSTEM privileges and potentially bypass antimalware tamper protection. He estimates 80% of Windows installations are vulnerable; no patch is available.

Nov 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

Apache Patches Critical HTTP/2 Remote Code Execution Flaw

Apache fixed CVE-2026-119618, a mod_http2 race condition that can enable unauthenticated remote code execution. HTTP/2 must be enabled; Wiz reports many exposed systems and no known public exploits or attacks.

Nov 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

Researchers Report N-able N-central Zero-Day Exploitation Hours After PoC Release

Previdian and Huntback reported exploitation of N-able N-central’s 4EverAble2Shell flaw. Huntback identified at least 21 servers running cryptocurrency miners, including 19 on the latest Hotfix 2; N-able said it had seen no signs of compromise.

Nov 12, 2026
Vulnerability & Exploit · databreachtoday.com

Researcher Releases 4EverAble2Shell and Agent2Shell Exploits for N-central

Sean Bales released two exploit chains targeting N-able N-central. One reportedly enables unauthenticated root access when the legacy API is enabled and exposed; N-able says it has seen no compromise and is restricting features while it remediates.

Nov 12, 2026
Vulnerability & Exploit · isc.sans.edu

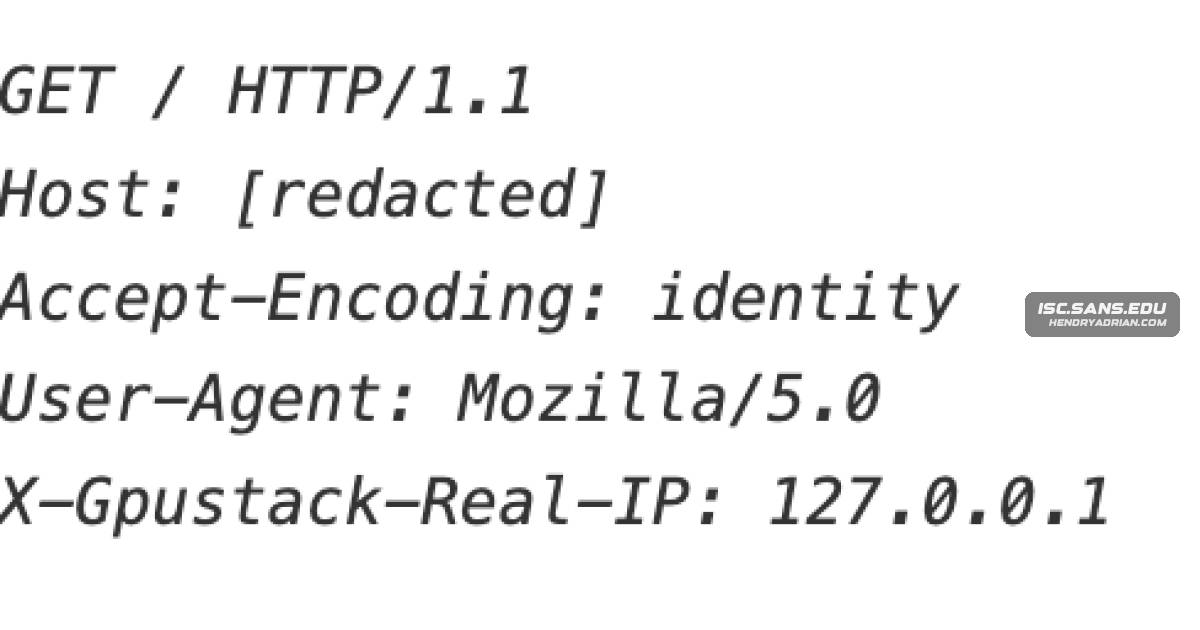
Exploit Attempts Target GPUStack Authentication Bypass (CVE-2026-102895)

Observed requests spoof the X-Gpustack-Real-IP header as 127.0.0.1 to bypass GPUStack authentication. The article says versions before 2.2.0 are affected; it does not establish that the attempts succeeded.

Nov 12, 2026
Vulnerability & Exploit · wiz.io

Apache HTTP/2 Race Condition Could Enable Unauthenticated RCE

CVE-2026-119618 is a race condition in Apache HTTP Server’s mod_http2 that can cause heap corruption and unauthenticated RCE. The article says no exploit or in-the-wild exploitation was known at publication and recommends upgrading or temporarily disabling HTTP/2.

Nov 11, 2026
Vulnerability & Exploit · thehackernews.com

Zoom Patches Two Windows Workplace Flaws That Could Enable Unauthenticated Privilege Escalation

Zoom released updates for two Zoom Workplace for Windows flaws that could let remote attackers escalate privileges without special permissions. The article does not say the flaws are being exploited in the wild.

Nov 11, 2026
Vulnerability & Exploit · securityweek.com

Vates Warns of Exploited Xen Orchestra Authentication Bypass

Vates says a threat actor is exploiting a critical Xen Orchestra authentication bypass and an administrator-only zero-day. The bypass affects releases before 6.9.2 and 6.10.1; a fix for the zero-day is still in development.

Nov 11, 2026
Vulnerability & Exploit · socprime.com

Microsoft Patches Actively Exploited Outlook Flaw That Can Expose NTLMv2 Hashes

Microsoft says CVE-2026-124194 is actively exploited. Opening a crafted Outlook message file can expose NTLMv2 authentication data; November 2026 Office updates fix it. Microsoft and CISA confirm exploitation, but actors and campaign scope remain undisclosed.

Nov 11, 2026
Vulnerability & Exploit · socradar.io

Google Patches Exploited Chrome XML Zero-Day CVE-2026-125350

Google patched CVE-2026-125350, an exploited Chrome use-after-free in XML handling. The article outlines fixed versions, a possible libxslt-related cause that Google has not confirmed, and steps to update Chrome and other Chromium browsers.

Nov 11, 2026
Vulnerability & Exploit · securityweek.com

Attackers Exploit Openwave and Cisco BroadWorks Vulnerabilities

Threat actors are exploiting flaws in Openwave Webtop Media Transcoder and Cisco BroadWorks. CISA added both to its KEV catalog and urged federal agencies to patch by November 24.

Nov 11, 2026
Vulnerability & Exploit · securityweek.com

Two Barracuda Vulnerabilities Exploited in Attacks

Barracuda warned that attackers are exploiting two patched vulnerabilities that could be chained for root access. CISA added both CVEs to its KEV catalog; Previdian observed 17 attempts targeting one flaw.

Nov 11, 2026
Vulnerability & Exploit · securityonline.info

Claude Code Patches Exposure of User Emails in HTTP Headers

The article reports that Claude Code sent authenticated users’ email addresses, and sometimes project-directory names, in HTTP User-Agent headers during web searches and curl requests. Anthropic released fixes in versions 2.1.317 and 2.1.321.

Nov 11, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited BroadWorks and Openwave Flaws to KEV

CISA added flaws affecting Cisco BroadWorks and Openwave Messaging Webtop Media Transcoder to its KEV catalog, citing active-exploitation evidence. Exploitation details and actor attribution are unavailable; FCEB agencies should patch by Nov. 24, 2026.

Nov 11, 2026
Vulnerability & Exploit · darkreading.com

N-able Takes N-central Offline After 33 Flaws Disclosed

N-able took hosted N-central environments offline and advised on-premises users to shut down after 33 flaws and public exploits were disclosed. A hotfix addresses seven CVEs; N-able reported scanning but no observed exploitation.

Nov 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

N-able Releases N-central Hotfixes for Seven Zero-Day Vulnerabilities

N-able released N-central 2026.4 HF2 to patch seven disclosed vulnerabilities. Hosted servers have been upgraded, and on-premises customers are urged to update. Defused reported probing, but N-able has not said the flaws were exploited.

Nov 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags Actively Exploited Cisco BroadWorks XXE Flaw

CISA added Cisco BroadWorks flaw CVE-2026-20320 to its KEV Catalog and urged prompt patching. Malbear Labs separately reported exploitation targeting a European telecom provider and 13 organizations using its infrastructure.

Nov 11, 2026
Vulnerability & Exploit · thehackernews.com

Git Fixes Flaw That Can Run Malicious Code During Recursive Clones

Git fixed CVE-2026-111760, an integer-truncation flaw that can let a malicious repository run code during recursive clones. The article also describes a separate Git server flaw and available mitigations.

Nov 10, 2026
PreviousPage 5 of 64 Next
© 2026 cyber.hendryadrian.com