
Ray CVE-2025-62593 Enables Browser-Driven Remote Code Execution
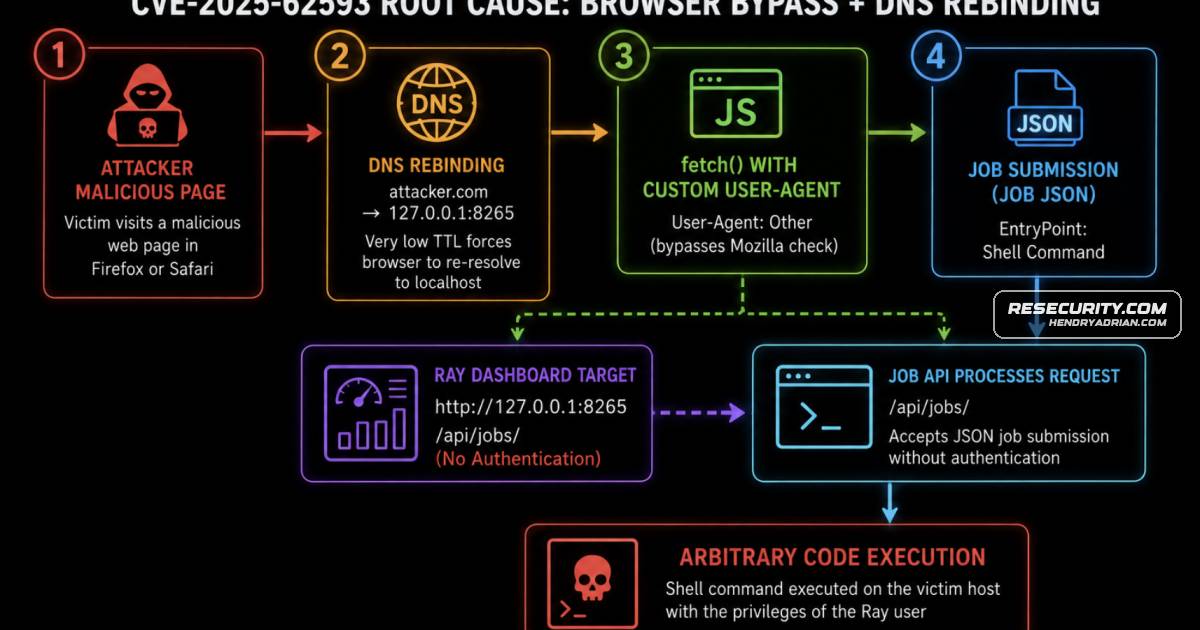
Summary
CVE-2025-62593 affects Ray versions before 2.52.0: DNS rebinding and a bypassable User-Agent check can let a webpage submit unauthenticated jobs to a local Ray Dashboard, potentially enabling code execution. Upgrade to 2.52.0 or later.
Key points
- An attacker-controlled webpage can use DNS rebinding to reach a Ray Dashboard on the victim’s local machine, then bypass browser-request checks by changing the User-Agent header.
- Unauthenticated access to the Ray Jobs API can allow a crafted job to execute code with the privileges of the Ray process.
- The article identifies Ray versions before 2.52.0 as affected; it recommends upgrading to 2.52.0 or later, preferably 2.52.1.
- Token authentication is available in Ray 2.52.0 but is disabled by default and must be enabled.
- CISA added the CVE to its KEV catalog citing active exploitation. BitSight reported RondoDox activity attempting exploitation before public disclosure, but said the observed implementation did not bypass Ray’s browser check.
- Recommended measures include restricting access to Ray management interfaces, enabling authentication, reviewing Jobs API activity, and investigating affected systems for signs of compromise.
Article Details
- Vulnerability Types
- DNS rebinding
- User-Agent-based browser-request protection bypass
- Unauthenticated job submission leading to remote code execution
- Severity
- Critical; GitHub CNA-assigned CVSS 4.0 score 9.4, while NVD CVSS 3.1 score is 8.8 (High).
- Affected Versions
- Ray < 2.52.0
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Enable Ray token authentication for the Dashboard and API interfaces.
- Restrict network access to Ray management interfaces and do not expose port 8265 directly to the Internet.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterA successfully submitted Ray job can execute attacker-controlled commands with the privileges of the Ray process.T1189 · Drive-by CompromiseThe described attack uses an attacker-controlled webpage to make a victim's browser reach a local Ray Dashboard and submit a job.