
Certighost Flaw Lets Low-Privilege AD Users Impersonate Domain Controllers
Summary
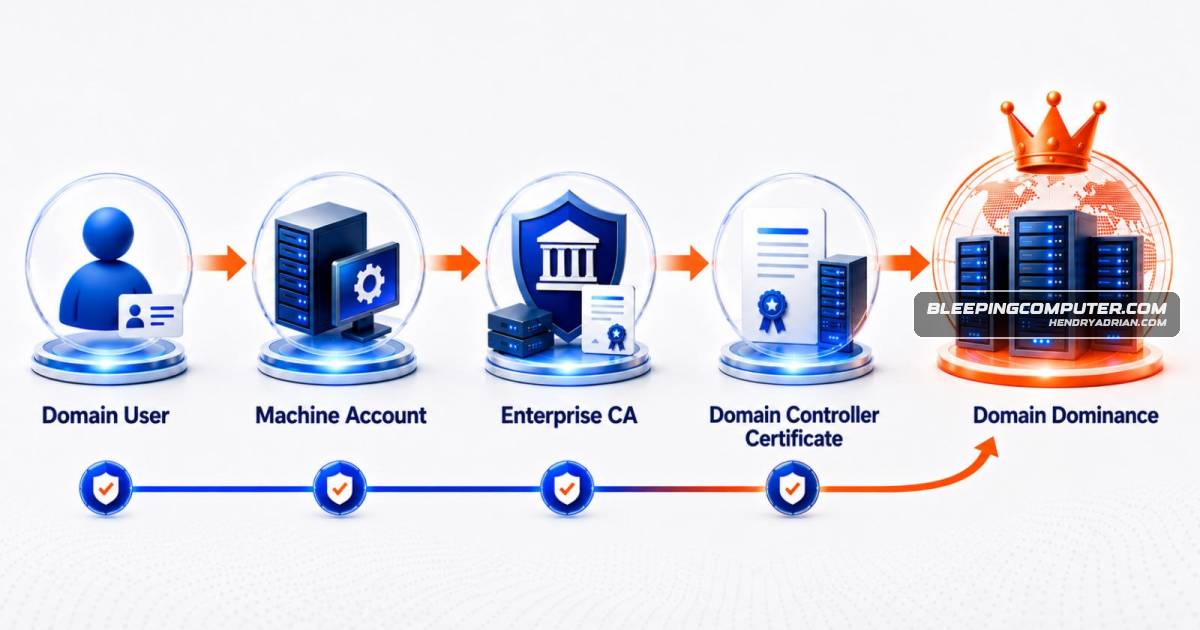
Certighost (CVE-2026-54121) can let a low-privileged Active Directory user obtain a Domain Controller authentication certificate. A public proof of concept was reported, but no in-the-wild exploitation was confirmed; Microsoft released a fix.
Key points
- The article says a working proof of concept was published on July 24, 2026; it reports no confirmed exploitation in the wild.
- The flaw abuses AD CS chase functionality: a CA follows requester-supplied cdc routing without verifying that the endpoint is a legitimate Domain Controller.
- A rogue endpoint can provide forged identity data, prompting the CA to issue a Domain Controller authentication certificate.
- The described attack chain uses PKINIT to obtain a Domain Controller machine-account ticket, then DCSync to retrieve credential material, potentially including the krbtgt hash.
- Microsoft released a fix on July 14, 2026, rated CVSS 8.8; the patch adds destination validation.
- Recommended steps include patching issuing CAs, reducing MachineAccountQuota, restricting CA outbound SMB and LDAP, and monitoring machine-account creation, certificate enrollment and DCSync activity.
Article Details
- Vulnerability Types
- AD CS chase-functionality destination-validation flaw
- Severity
- Critical (CVSS 8.8)
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Disable the vulnerable chase functionality; test first because this may disrupt legitimate enrollment workflows.
MITRE ATT&CK
T1003.006 · DCSyncAfter obtaining the Domain Controller identity, the attacker can perform DCSync to retrieve credential material, including the krbtgt hash.T1558.001 · Golden TicketThe article describes using the krbtgt hash obtained through DCSync to forge Kerberos tickets.T1649 · Steal or Forge Authentication CertificatesA low-privileged domain user can exploit unverified cdc routing to obtain a Domain Controller authentication certificate from an Enterprise CA, then use it with PKINIT.
CVE
Vendors
Products
Active Directory Certificate ServicesCertighost (CVE-2026-54121) is a critical Active Directory Certificate Services flaw that lets a low-privileged domain user trick an Enterprise CA into issuing a Domain Controller authentication certificate, potentiallyMicrosoft Active DirectoryCertighost (CVE-2026-54121) is a critical Active Directory Certificate Services flaw that lets a low-privileged domain user trick an Enterprise CA into issuing a Domain Controller authentication certificate, potentially