
Researchers Detail Two OpenAI Codex Sandbox Escapes
Summary
Researchers described Heapjack and Overpatch, two flaws that could bypass OpenAI Codex sandbox restrictions and run commands on a developer’s machine. OpenAI patched both; users should update Codex Desktop or CLI.
Key points
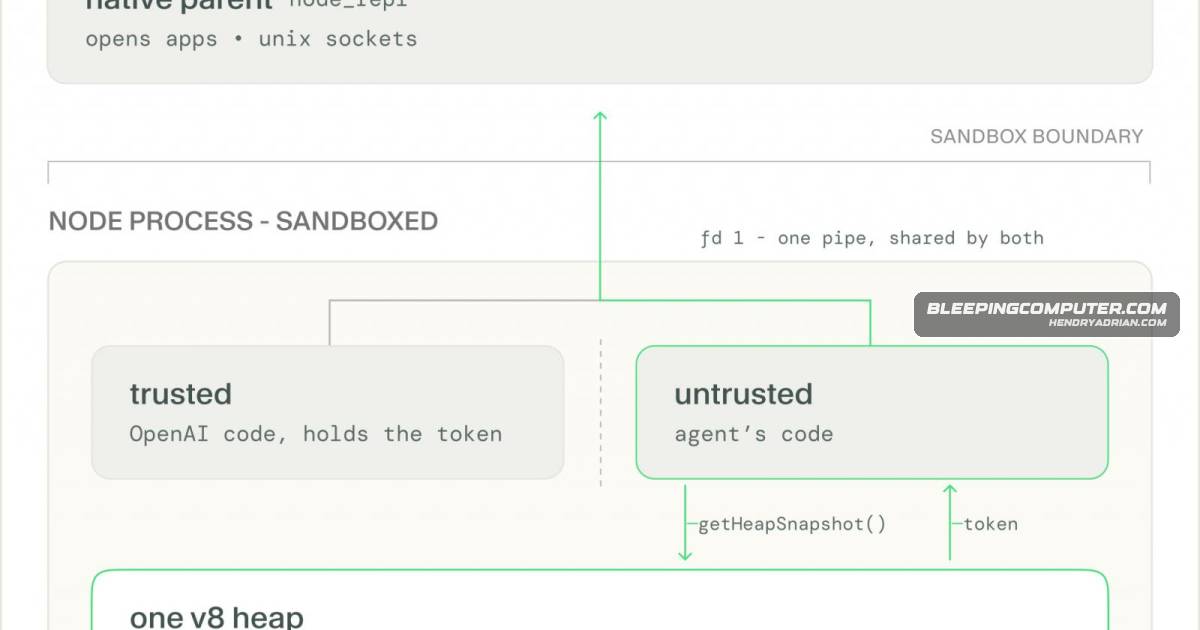
- Heapjack targeted Codex Desktop’s node_repl component: trusted and untrusted JavaScript contexts shared a Node.js process and memory heap, exposing a token used to access an unsandboxed parent process.
- Researchers said Heapjack could enable command execution on a developer’s machine when they opened an attacker-controlled repository and asked Codex about its code—even in read-only mode.
- Overpatch affected Codex CLI’s workspace-write mode. A crafted apply_patch operation could widen write permissions and use a symlink to modify .zshrc outside the project folder.
- The researchers reported both flaws to OpenAI on August 12; according to the article, OpenAI fixed them within eight days.
- Users should update to Codex Desktop build 26.818.21641 or later and Codex CLI 0.149.0 or later.
Article Details
- Vulnerability Types
- Sandbox escape through shared-memory access to a trusted token in node_repl
- Sandbox write-restriction bypass through apply_patch permission handling and a symlink
- Exploitation Status
- not_reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- Update to Codex Desktop build 26.818.21641 or later and Codex CLI 0.149.0 or later.
People
Vendors
Products
CodexResearchers uncovered two sandbox escapes in OpenAI Codex, including Heapjack and Overpatch, that could let attacker-controlled code run commands outside Codex’s intended restrictions.Codex CLIOpenAI patched both issues quickly, and users are advised to update to Codex Desktop build 26.818.21641 or Codex CLI 0.149.0 and later.Codex DesktopOpenAI patched both issues quickly, and users are advised to update to Codex Desktop build 26.818.21641 or Codex CLI 0.149.0 and later.
Tools
apply_patchOverpatch bypassed Codex CLI write restrictions using apply_patch and a symlink.HeapjackResearchers uncovered two sandbox escapes in OpenAI Codex, including Heapjack and Overpatch, that could let attacker-controlled code run commands outside Codex’s intended restrictions.node_replHeapjack abused the node_repl component and shared memory in Node.js.OverpatchResearchers uncovered two sandbox escapes in OpenAI Codex, including Heapjack and Overpatch, that could let attacker-controlled code run commands outside Codex’s intended restrictions.