
WordPress 7.1.1 Fixes Click2Shell Flaw That Can Lead to Server Code Execution
Summary
WordPress 7.1.1 fixes Click2Shell, which can trick a logged-in administrator into installing a theme from WordPress[.]org. Chained with a separate theme flaw, it can enable server code execution; no public exploitation has been reported.
Key points
- A crafted link opened by a logged-in administrator can trigger installation of an inactive theme without an installation click.
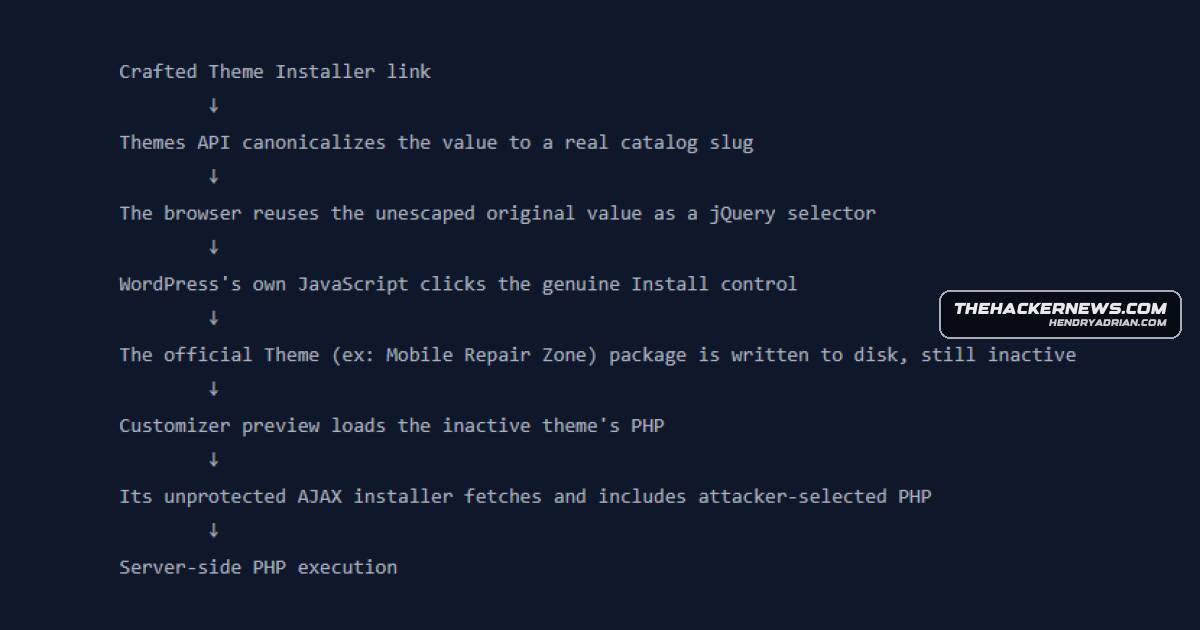
- Researchers at pwn.ai named the attack chain Click2Shell; the core flaw alone does not install an arbitrary theme ZIP or execute code.
- The researchers demonstrated code execution by chaining the forced install with a separate flaw in the Mobile Repair Zone theme.
- WordPress released the fix in version 7.1.1 on September 17; fixes are available for supported branches back to 4.7.
- WordPress advises updating; no separate workaround was offered, and the article reports no sign of real-world exploitation.
- Researchers rated the core flaw 7.1 and the full chain 9.6; no CVE identifier had been assigned at publication.
Article Details
- Vulnerability Types
- Crafted-link-triggered automatic installation and preview of an inactive theme
- Theme background handler downloads and executes a package without authorization or a security token
- Severity
- Researchers rated the core flaw high (CVSS 7.1) and the chained code-execution attack critical (CVSS 9.6); WordPress did not publish its own severity rating.
- Affected Versions
- WordPress 6.0 through releases before 7.1.1
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1059.004 · Unix ShellThe Mobile Repair Zone theme's vulnerable handler ran attacker-supplied code as PHP on the server after the forced theme installation.T1204.001 · Malicious LinkThe chain requires a logged-in administrator to open the crafted link, which redirects browser interaction to the theme Install button.
Vendors
Products
Mobile Repair ZoneResearchers at pwn.ai named the attack chain Click2Shell and showed it could be paired with a separate theme flaw, such as one in Mobile Repair Zone, to achieve code execution on the server.WordPressWordPress released security patches in version 7.1.1 to fix a core flaw that could let a logged-in administrator be tricked into automatically installing a theme from WordPress.org through a crafted link.