

SonicWall SMA 1000 Flaw Sees 135 Exploitation Attempts After Patch
Threat intelligence firms observed 135 attempts to exploit critical pre-authenticated SSRF flaw CVE-2026-102255 in SonicWall SMA 1000 appliances after patches were released.
Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.
1553 articles
Threat intelligence firms observed 135 attempts to exploit critical pre-authenticated SSRF flaw CVE-2026-102255 in SonicWall SMA 1000 appliances after patches were released.

Attackers are exploiting CVE-2026-85097 in Bricksforge for unauthenticated PHP code execution on WordPress sites. Versions through 3.1.8.9 are affected; site owners should update and check for signs of compromise.
Attack attempts targeting critical pre-authentication SSRF flaw CVE-2026-102255 in SonicWall SMA1000 appliances were observed two days after disclosure. SonicWall urged customers to update affected models.

Security vendors observed attempts to exploit CVE-2026-102255, a maximum-severity SSRF flaw in SonicWall SMA 1000 appliances. SonicWall has released a hotfix and urges customers to apply it.

GitLab patched CVE-2026-97229, a critical integer overflow in its CI/CD regular expression compiler that could let unauthenticated attackers execute code. Self-managed installations should upgrade; GitLab.com is patched.
Citrix disclosed CVE-2026-107406, a critical memory overflow in NetScaler ADC and Gateway that could enable unauthenticated code execution or denial of service on affected SAML-configured appliances. It recommends upgrading to patched builds.
Cisco patched five critical NX-OS flaws that can enable unauthenticated remote code execution or denial of service on configured Nexus switches. No active exploitation was confirmed as of October 9, 2026.

Researchers found more than 2,000 internet-exposed GPU servers running NVIDIA DCGM Exporter. CVE-2026-47483 lets unauthenticated requests to profiling endpoints crash the exporter; NVIDIA recommends upgrading to version 4.8.2 or later.

Researchers published AnyPwn, an exploit for a pre-authentication heap overflow in AnyDesk Linux 8.0.2 that can enable root command execution. Update to 8.0.3 or later; exploitability through relay connections remains unresolved.

Attackers are exploiting two AhsayCBS flaws to gain remote code execution and deploy web shells and XMRig miners. Huntress says version 10.3.4 may also be affected and recommends restricting management-interface access.
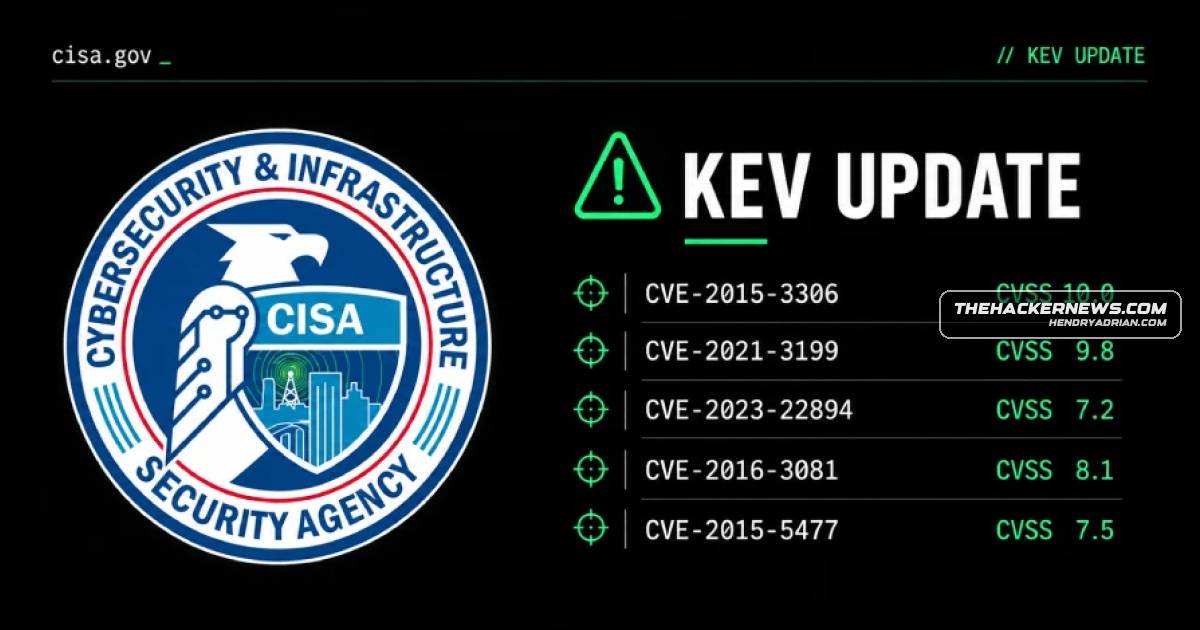
CISA added five vulnerabilities exploited in activity linked to Flax Typhoon to its KEV catalog. Federal agencies must patch them or stop using affected products by October 11, 2026.
CISA reports active global exploitation of critical NetScaler zero-days, including flaws enabling remote code execution. It urges organizations to check for compromise, apply Citrix updates promptly, preserve evidence, and follow recovery guidance.

Attackers are exploiting two unpatched AhsayCBS vulnerabilities for unauthenticated remote code execution. Huntress says at least five organizations were targeted, and recommends restricting access to the management interface while investigating for compromise.

A flaw in GoBalance can let attackers recover some Tor onion services’ master keys from a public descriptor and hijack their addresses. Dread and Omega moved to new addresses; affected operators must migrate because published keys cannot be recalled.
Citrix patched CVE-2026-107406, a critical NetScaler ADC and Gateway memory overflow that could enable remote code execution or denial of service in deployments configured as SAML identity or service providers. No in-the-wild exploitation was reported.

Citrix urged customers to patch CVE-2026-107406, a critical NetScaler memory-overflow flaw that could enable remote code execution or denial of service. Fixes are available, and Citrix says it is unaware of unmitigated exploits.
Cisco patched critical CVE-2026-76471, a flaw in NX-API affecting certain Nexus switches and UCS 6300 fabric interconnects. Exploitation can enable root-level code execution or device reloads; exposure depends on access and platform configuration.
Researchers reported active exploitation of two AhsayCBS flaws, affecting versions through 10.3.4 at disclosure. Chained, unauthenticated attacks can give SYSTEM access; observed activity included web shells and cryptomining.
Attackers exploited two AhsayCBS flaws to deploy JSP webshells and an XMRig miner at five or more organizations. Huntress says the latest version, 10.3.4, is also affected; it recommends restricting management access and investigating for compromise.
Researchers observed exploitation attempts against CVE-2026-102255, a maximum-severity flaw in certain SonicWall SMA1000 appliances. SonicWall patched it three days earlier, but researchers have not confirmed successful compromises.
Citrix disclosed CVE-2026-107406, a memory overflow affecting NetScaler ADC and Gateway appliances configured as SAML IdPs or SPs. It can enable remote code execution or denial of service; Citrix says it has no evidence of exploitation and urges upgrades.
Cisco released patches for 35 vulnerabilities across its products, including more than a dozen critical flaws. The company says it is unaware of any exploitation in the wild.
Attackers began targeting critical CVE-2026-21589 in Atlassian Data Center products hours after PoC publication. The flaw can expose files, including Crowd credentials; patches are available for all affected versions.
SonicWall and Splunk released patches for multiple vulnerabilities, including critical flaws that could enable code execution. SonicWall said there is no evidence the issues are being exploited in the wild.