cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · darkreading.com

AgentCorruption Flaw Could Expose AWS Bedrock AgentCore Environments to Takeover

Researchers found that a prompt to a public-facing Bedrock AgentCore agent could expose instance credentials and enable access to other agents and secrets in an AWS region. AWS updated IMDS settings and default permissions; researchers reported no known exploitation.

Oct 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco warns of five critical flaws that could let attackers take over Nexus switches

Cisco disclosed five critical NX-OS flaws that could enable root-level code execution or denial of service on some Nexus switches, plus four Cisco License flaws. It recommends upgrades and disabling affected features when unnecessary.

Oct 8, 2026
Vulnerability & Exploit · helpnetsecurity.com

Attackers Target Critical Atlassian Data Center File-Access Flaw CVE-2026-21589

Attackers are attempting to exploit CVE-2026-21589, a critical file-access flaw in Atlassian Data Center products. The flaw can expose sensitive files; Atlassian urges customers to patch, restrict internet access, and review logs.

Oct 7, 2026
Vulnerability & Exploit · thehackernews.com

SonicWall Releases Hotfixes for Critical Pre-Authentication SSRF Flaw in SMA1000 Appliances

SonicWall released hotfixes for four SMA1000 flaws, including a CVSS 10.0 SSRF vulnerability reachable without authentication. The company says it has no evidence the new flaws are being exploited.

Oct 7, 2026
Vulnerability & Exploit · thehackernews.com

Critical LMCache Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-105192 lets unauthenticated attackers run code on exposed LMCache multiprocess servers. Versions 0.3.9 through 0.5.5 and some prereleases are affected; no fix is available, and operators should avoid routable addresses.

Oct 7, 2026
Vulnerability & Exploit · malwarebytes.com

Google Releases October Android Security Updates for Android 14 and Later

Google's October Android security updates fix critical vulnerabilities and cover Android 14 and newer. Device vendors may delay patches, leaving some supported phones exposed while older devices may not receive them.

Oct 7, 2026
Vulnerability & Exploit · socradar.io

Critical Atlassian Flaw Exposes Files in Eight Self-Hosted Products

CVE-2026-21589 allows unauthenticated access to specific files in the web roots of eight self-hosted Atlassian products. Atlassian has issued fixes; it reports no evidence of exploitation as of October 7.

Oct 7, 2026
Vulnerability & Exploit · helpnetsecurity.com

SonicWall Patches Four Vulnerabilities in SMA 1000 Appliances

SonicWall patched four vulnerabilities in SMA 1000 appliances, including a pre-authentication SSRF flaw. Affected physical and virtual models should be upgraded to firmware 12.4.3-03670 or 12.5.0-03082 or later.

Oct 7, 2026
Vulnerability & Exploit · rapid7.com

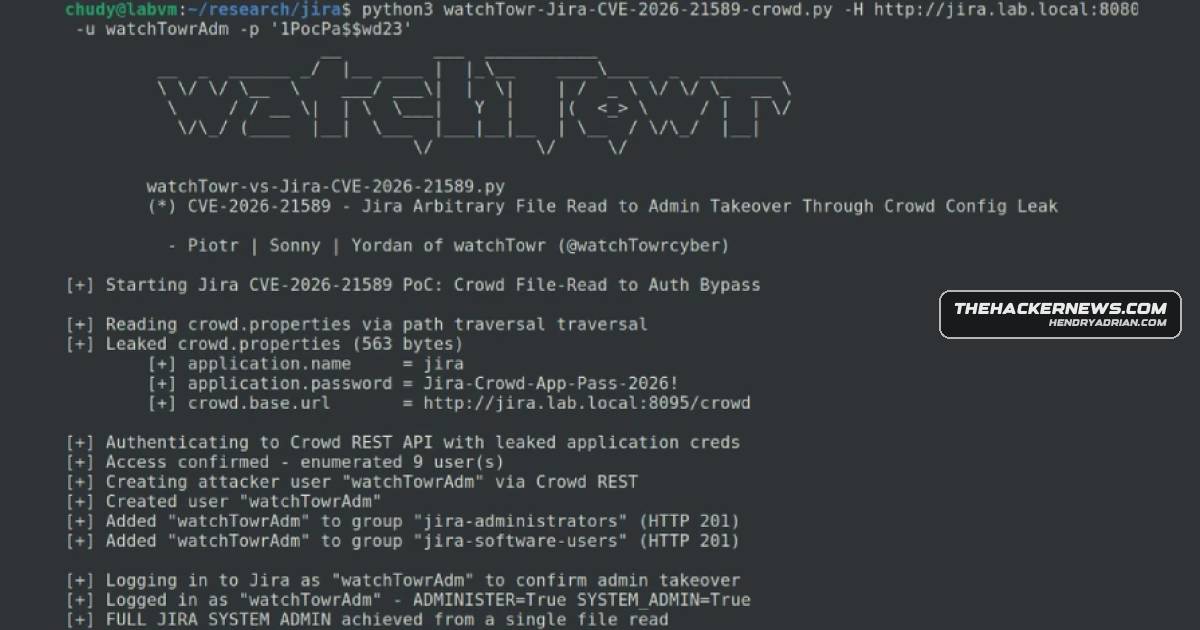
Critical Atlassian File-Access Flaw Affects Eight Products; Patches Available

CVE-2026-21589 lets unauthenticated attackers read files in the web root of eight Atlassian products. Public PoCs are available; Rapid7 urges emergency patching, log review, and credential rotation if protected files were accessed.

Oct 7, 2026
Vulnerability & Exploit · thehackernews.com

Atlassian Data Center Flaw Exploited Within Two Hours of Public Technical Details

Attackers have targeted CVE-2026-21589, a critical unauthenticated file-access flaw in Atlassian Data Center products. Honeypots recorded attempts within two hours of public technical details; no use of obtained credentials has been observed.

Oct 7, 2026
Vulnerability & Exploit · securityweek.com

Chrome 155 Update Fixes 247 Vulnerabilities, Including Four Critical Flaws

Google’s Chrome 155 update fixes 247 vulnerabilities, including four critical use-after-free flaws. The update is rolling out for Windows, macOS, and Linux; Google reported no known exploitation in the wild.

Oct 7, 2026
Vulnerability & Exploit · malwarebytes.com

Google Updates Chrome and ChromeOS to Fix Critical Security Flaws

Google released Chrome and ChromeOS updates that include 247 security fixes, including four critical issues. The article details three high-impact Chrome flaws and explains how to install the updates.

Oct 7, 2026
Vulnerability & Exploit · securityweek.com

Google’s October 2026 Android Update Patches 25 Vulnerabilities

Google’s October 2026 Android updates fix 25 Framework and System vulnerabilities, including seven critical flaws. Pixel and Android Automotive OS devices also received fixes; Google did not report in-the-wild exploitation.

Oct 7, 2026
Vulnerability & Exploit · securityweek.com

Atlassian Patches Critical File-Access Flaw Affecting Eight Products

Atlassian patched an unauthenticated file-access vulnerability affecting all versions of eight products. The flaw requires knowing a target file’s exact path; there is no evidence of in-the-wild exploitation.

Oct 7, 2026
Vulnerability & Exploit · fieldeffect.com

Attackers Exploit Atlassian CVE-2026-21589 After Public PoC Release

Attackers reportedly began exploiting CVE-2026-21589 two days after public PoC code appeared. The unauthenticated path-traversal flaw affects self-hosted Atlassian Data Center products; Atlassian Cloud is not affected.

Oct 7, 2026
Vulnerability & Exploit · fieldeffect.com

SonicWall fixes critical unauthenticated SSRF flaw in SMA1000 appliances

SonicWall issued hotfixes for four SMA1000 vulnerabilities, including an unauthenticated SSRF flaw that can let remote attackers make appliances reach internal functionality. The company reported no evidence of exploitation.

Oct 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

SonicWall patches maximum-severity SSRF flaw in SMA1000 gateways

SonicWall released hotfixes for an unauthenticated SSRF flaw in SMA1000 gateways. The company says it has no evidence of exploitation and urges customers to update affected appliances.

Oct 7, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers exploit critical unauthenticated Atlassian flaw after public PoC

Attackers began probing CVE-2026-21589 within hours of a public PoC. The unauthenticated flaw affects eight self-hosted Atlassian products and can expose files; in certain Crowd-integrated setups, credentials could enable Jira administrator access.

Oct 7, 2026
Vulnerability & Exploit · socradar.io

Citrix Patches Exploited NetScaler Zero-Day Causing Denial of Service

Citrix patched CVE-2026-88779, a zero-day memory overflow affecting SAML-configured, customer-managed NetScaler appliances. Exploitation causes denial of service; administrators should upgrade to fixed builds and investigate unexplained instability.

Oct 6, 2026
Vulnerability & Exploit · thehackernews.com

LibreOffice and OpenOffice Flaws Let Spreadsheets Run Code Without Macro Warnings

Researchers demonstrated that malicious spreadsheets can run attacker-controlled Java code in LibreOffice and OpenOffice without a macro warning when Java support is enabled. LibreOffice has patched its flaw; OpenOffice's remains unfixed.

Oct 6, 2026
Vulnerability & Exploit · thehackernews.com

Critical Atlassian Flaw Allows Unauthenticated File Reads Across Eight Self-Hosted Products

CVE-2026-21589 lets unauthenticated attackers read specifically named files in the web roots of eight self-hosted Atlassian products. Atlassian released fixes and temporary blocking rules; its cloud products are patched.

Oct 6, 2026
Vulnerability & Exploit · cyberscoop.com

Citrix Patches Actively Exploited NetScaler Zero-Day Affecting SAML-Enabled Systems

Citrix patched actively exploited CVE-2026-88779, a NetScaler flaw that can cause denial of service on SAML-enabled deployments. CISA added it to its known exploited vulnerabilities catalog; researchers warned it could aid exploitation of another flaw.

Oct 6, 2026
Vulnerability & Exploit · therecord.media

CISA Orders Patch for Actively Exploited Citrix NetScaler DoS Flaw

CISA ordered federal agencies to patch actively exploited Citrix NetScaler vulnerability CVE-2026-88779 by Wednesday and conduct forensic triage. Citrix says the flaw can disrupt availability but has not identified an impact on data integrity.

Oct 6, 2026
Vulnerability & Exploit · fieldeffect.com

Citrix Patches Actively Exploited NetScaler SAML Vulnerability

Citrix says attackers are exploiting CVE-2026-88779 in SAML-enabled NetScaler deployments. The flaw can cause authentication-service crashes and outages; affected systems need the October 3 updates.

Oct 6, 2026
PreviousPage 24 of 65 Next
© 2026 cyber.hendryadrian.com