CISA Adds Five Flax Typhoon-Exploited Flaws to KEV, Sets October 11 Federal Deadline
Summary
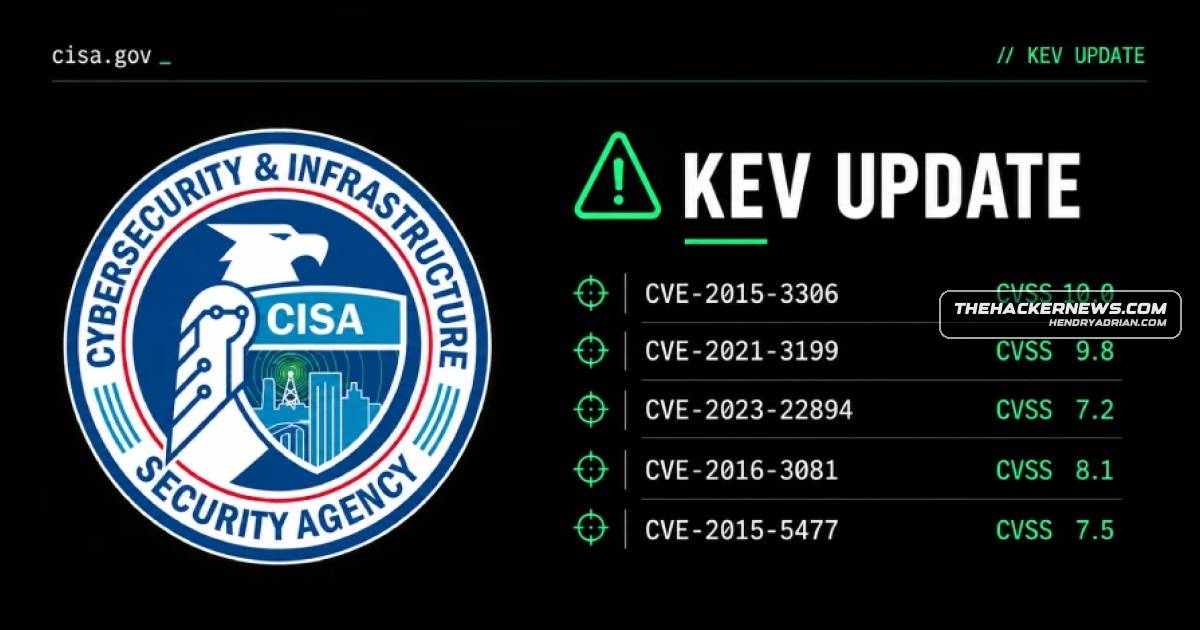
CISA added five vulnerabilities exploited in activity linked to Flax Typhoon to its KEV catalog. Federal agencies must patch them or stop using affected products by October 11, 2026.
Key points
- CISA added five security flaws to its Known Exploited Vulnerabilities catalog following their exploitation by Flax Typhoon.
- A joint advisory from authorities in seven countries described operations targeting eight vulnerabilities, including the five newly added to KEV.
- The activity reportedly uses scanning tools, cross-site scripting, and password spraying against Microsoft Exchange for initial access.
- Attackers reportedly establish persistence through VPN software and use scripts to exfiltrate emails and credentials.
- The three other vulnerabilities in the joint advisory were already listed in KEV.
- Federal agencies must apply patches or discontinue use of affected products by October 11, 2026. The article does not name the vulnerabilities or affected products.
Article Details
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- unknown